The CISA Vulnerability Bulletin provides a summary of new vulnerabilities that have been recorded by the National Institute of Standards and Technology (NIST) National Vulnerability Database (NVD) in the past week. NVD is sponsored by CISA. In some cases, the vulnerabilities in the bulletin may not yet have assigned CVSS scores. Please visit NVD for updated vulnerability entries, which include CVSS scores once they are available.
Vulnerabilities are based on the Common Vulnerabilities and Exposures (CVE) vulnerability naming standard and are organized according to severity, determined by the Common Vulnerability Scoring System (CVSS) standard. The division of high, medium, and low severities correspond to the following scores:
- High: vulnerabilities with a CVSS base score of 7.0–10.0
- Medium: vulnerabilities with a CVSS base score of 4.0–6.9
- Low: vulnerabilities with a CVSS base score of 0.0–3.9
Entries may include additional information provided by organizations and efforts sponsored by CISA. This information may include identifying information, values, definitions, and related links. Patch information is provided when available. Please note that some of the information in the bulletin is compiled from external, open-source reports and is not a direct result of CISA analysis.
| Primary Vendor -- Product | Description | Published | CVSS Score | Source & Patch Info |
|---|---|---|---|---|
| kamailio -- kamailio | The Kamailio SIP before 5.5.0 server mishandles INVITE requests with duplicated fields and overlength tag, leading to a buffer overflow that crashes the server or possibly have unspecified other impact. | 2023-03-15 | 9.8 | CVE-2020-27507 MISC MISC |
| stoqey -- gnuplot | An issue found in Stoqey gnuplot v.0.0.3 and earlier allows attackers to execute arbitrary code via the src/index.ts, plotCallack, child_process, and/or filePath parameter(s). | 2023-03-10 | 9.8 | CVE-2021-33360 MISC MISC |
| qualcomm -- ar8035_firmware | Memory corruption due to improper validation of array index in Multi-mode call processor. | 2023-03-10 | 9.8 | CVE-2022-33256 MISC |
| combodo -- itop | Combodo iTop is an open source, web-based IT service management platform. Prior to versions 2.7.8 and 3.0.2-1, the reset password token is generated without any randomness parameter. This may lead to account takeover. The issue is fixed in versions 2.7.8 and 3.0.2-1. | 2023-03-14 | 9.8 | CVE-2022-39216 MISC MISC MISC |
| qualcomm -- apq8009_firmware | Memory corruption in Video due to double free while playing 3gp clip with invalid metadata atoms. | 2023-03-10 | 9.8 | CVE-2022-40515 MISC |
| qualcomm -- apq8009_firmware | Memory corruption in Bluetooth HOST while processing the AVRC_PDU_GET_PLAYER_APP_VALUE_TEXT AVRCP response. | 2023-03-10 | 9.8 | CVE-2022-40537 MISC |
| ibexa -- kernel | An issue was discovered in eZ Publish Ibexa Kernel before 7.5.28. Access control based on object state is mishandled. | 2023-03-12 | 9.8 | CVE-2022-48367 MISC MISC |
| 10web -- map_builder_for_google_maps | The 10Web Map Builder for Google Maps WordPress plugin before 1.0.73 does not properly sanitise and escape some parameters before using them in an SQL statement via an AJAX action available to unauthenticated users, leading to a SQL injection | 2023-03-13 | 9.8 | CVE-2023-0037 MISC MISC |
| akuvox -- e11_firmware | The Akuvox E11 secure shell (SSH) server is enabled by default and can be accessed by the root user. This password cannot be changed by the user. | 2023-03-13 | 9.8 | CVE-2023-0345 MISC |
| akuvox -- e11_firmware | Akuvox E11 uses a weak encryption algorithm for stored passwords and uses a hard-coded password for decryption which could allow the encrypted passwords to be decrypted from the configuration file. | 2023-03-13 | 9.8 | CVE-2023-0353 MISC |
| alpatateknoloji -- licensed_warehousing_automation_system | Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in Alpata Licensed Warehousing Automation System allows Command Line Execution through SQL Injection.This issue affects Licensed Warehousing Automation System: through 2023.1.01. | 2023-03-10 | 9.8 | CVE-2023-1091 MISC |
| saysis -- starcities | Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in Saysis Starcities allows SQL Injection.This issue affects Starcities: through 1.3. | 2023-03-10 | 9.8 | CVE-2023-1198 MISC |
| froxlor -- froxlor | Authentication Bypass by Primary Weakness in GitHub repository froxlor/froxlor prior to 2.0.13. | 2023-03-10 | 9.8 | CVE-2023-1307 MISC CONFIRM |
| online_graduate_tracer_system_project -- online_graduate_tracer_system | A vulnerability classified as critical has been found in SourceCodester Online Graduate Tracer System 1.0. Affected is an unknown function of the file admin/adminlog.php. The manipulation of the argument user leads to sql injection. It is possible to launch the attack remotely. The exploit has been disclosed to the public and may be used. The identifier of this vulnerability is VDB-222696. | 2023-03-10 | 9.8 | CVE-2023-1308 MISC MISC MISC |
| online_graduate_tracer_system_project -- online_graduate_tracer_system | A vulnerability classified as critical was found in SourceCodester Online Graduate Tracer System 1.0. Affected by this vulnerability is an unknown functionality of the file admin/search_it.php. The manipulation of the argument input leads to sql injection. The attack can be launched remotely. The exploit has been disclosed to the public and may be used. The identifier VDB-222697 was assigned to this vulnerability. | 2023-03-10 | 9.8 | CVE-2023-1309 MISC MISC MISC |
| online_graduate_tracer_system_project -- online_graduate_tracer_system | A vulnerability, which was classified as critical, has been found in SourceCodester Online Graduate Tracer System 1.0. Affected by this issue is some unknown functionality of the file admin/prof.php. The manipulation of the argument id leads to sql injection. The attack may be launched remotely. The exploit has been disclosed to the public and may be used. VDB-222698 is the identifier assigned to this vulnerability. | 2023-03-10 | 9.8 | CVE-2023-1310 MISC MISC MISC |
| friendly_island_pizza_website_and_ordering_system_project -- friendly_island_pizza_website_and_ordering_system | A vulnerability, which was classified as critical, was found in SourceCodester Friendly Island Pizza Website and Ordering System 1.0. This affects an unknown part of the file large.php of the component GET Parameter Handler. The manipulation of the argument id leads to sql injection. It is possible to initiate the attack remotely. The exploit has been disclosed to the public and may be used. The associated identifier of this vulnerability is VDB-222699. | 2023-03-10 | 9.8 | CVE-2023-1311 MISC MISC MISC |
| lmxcms -- lmxcms | A vulnerability has been found in lmxcms 1.41 and classified as critical. Affected by this vulnerability is the function update of the file AcquisiAction.class.php. The manipulation of the argument id with the input -1 and updatexml(0,concat(0x7e,user()),1)# leads to sql injection. The attack can be launched remotely. The exploit has been disclosed to the public and may be used. The associated identifier of this vulnerability is VDB-222727. | 2023-03-10 | 9.8 | CVE-2023-1321 MISC MISC |
| lmxcms -- lmxcms | A vulnerability was found in lmxcms 1.41 and classified as critical. Affected by this issue is the function reply of the file BookAction.class.php. The manipulation of the argument id with the input 1) and updatexml(0,concat(0x7e,user()),1)# leads to sql injection. The attack may be launched remotely. The exploit has been disclosed to the public and may be used. The identifier of this vulnerability is VDB-222728. | 2023-03-10 | 9.8 | CVE-2023-1322 MISC MISC |
| liferea_project -- liferea | A vulnerability was found in liferea. It has been rated as critical. Affected by this issue is the function update_job_run of the file src/update.c of the component Feed Enrichment. The manipulation of the argument source with the input |date >/tmp/bad-item-link.txt leads to os command injection. The attack may be launched remotely. The exploit has been disclosed to the public and may be used. The name of the patch is 8d8b5b963fa64c7a2122d1bbfbb0bed46e813e59. It is recommended to apply a patch to fix this issue. The identifier of this vulnerability is VDB-222848. | 2023-03-11 | 9.8 | CVE-2023-1350 MISC MISC MISC |
| computer_parts_sales_and_inventory_system_project -- computer_parts_sales_and_inventory_system | A vulnerability classified as critical has been found in SourceCodester Computer Parts Sales and Inventory System 1.0. This affects an unknown part of the file cust_transac.php. The manipulation of the argument phonenumber leads to sql injection. It is possible to initiate the attack remotely. The exploit has been disclosed to the public and may be used. The identifier VDB-222849 was assigned to this vulnerability. | 2023-03-11 | 9.8 | CVE-2023-1351 MISC MISC MISC |
| design_and_implementation_of_covid-19_directory_on_vaccination_system_project -- design_and_implementation_of_covid-19_directory_on_vaccination_system | A vulnerability, which was classified as critical, has been found in SourceCodester Design and Implementation of Covid-19 Directory on Vaccination System 1.0. This issue affects some unknown processing of the file /admin/login.php. The manipulation of the argument txtusername/txtpassword leads to sql injection. The attack may be initiated remotely. The exploit has been disclosed to the public and may be used. The associated identifier of this vulnerability is VDB-222851. | 2023-03-11 | 9.8 | CVE-2023-1352 MISC MISC MISC |
| simple_bakery_shop_management_system_project -- simple_bakery_shop_management_system | A vulnerability, which was classified as critical, has been found in SourceCodester Simple Bakery Shop Management System 1.0. Affected by this issue is some unknown functionality of the component Admin Login. The manipulation of the argument username/password with the input admin' or 1=1 -- leads to sql injection. The attack may be launched remotely. The exploit has been disclosed to the public and may be used. The identifier of this vulnerability is VDB-222860. | 2023-03-12 | 9.8 | CVE-2023-1357 MISC MISC |
| gadget_works_online_ordering_system_project -- gadget_works_online_ordering_system | A vulnerability, which was classified as critical, was found in SourceCodester Gadget Works Online Ordering System 1.0. This affects an unknown part of the file /philosophy/admin/login.php of the component POST Parameter Handler. The manipulation of the argument user_email leads to sql injection. It is possible to initiate the attack remotely. The exploit has been disclosed to the public and may be used. The identifier VDB-222861 was assigned to this vulnerability. | 2023-03-12 | 9.8 | CVE-2023-1358 MISC MISC MISC |
| xhcms_project -- xhcms | A vulnerability was found in XHCMS 1.0. It has been declared as critical. This vulnerability affects unknown code of the file login.php of the component POST Parameter Handler. The manipulation of the argument user leads to sql injection. The attack can be initiated remotely. The exploit has been disclosed to the public and may be used. VDB-222874 is the identifier assigned to this vulnerability. | 2023-03-13 | 9.8 | CVE-2023-1368 MISC MISC MISC |
| friendly_island_pizza_website_and_ordering_system_project -- friendly_island_pizza_website_and_ordering_system | A vulnerability classified as critical was found in SourceCodester Friendly Island Pizza Website and Ordering System 1.0. This vulnerability affects unknown code of the file paypalsuccess.php of the component POST Parameter Handler. The manipulation of the argument cusid leads to sql injection. The attack can be initiated remotely. The exploit has been disclosed to the public and may be used. The identifier of this vulnerability is VDB-222904. | 2023-03-13 | 9.8 | CVE-2023-1378 MISC MISC MISC |
| online_tours_&travels_management_system_project -- online_tours&_travels_management_system | A vulnerability, which was classified as problematic, was found in SourceCodester Online Tours & Travels Management System 1.0. Affected is an unknown function of the file admin/ab.php. The manipulation of the argument img leads to unrestricted upload. It is possible to launch the attack remotely. The exploit has been disclosed to the public and may be used. VDB-222978 is the identifier assigned to this vulnerability. | 2023-03-14 | 9.8 | CVE-2023-1391 MISC MISC MISC |
| online_pizza_ordering_system_project -- online_pizza_ordering_system | A vulnerability has been found in SourceCodester Online Pizza Ordering System 1.0 and classified as critical. Affected by this vulnerability is the function save_menu. The manipulation leads to unrestricted upload. The attack can be launched remotely. The exploit has been disclosed to the public and may be used. The associated identifier of this vulnerability is VDB-222979. | 2023-03-14 | 9.8 | CVE-2023-1392 MISC MISC MISC |
| online_graduate_tracer_system_project -- online_graduate_tracer_system | A vulnerability was found in SourceCodester Online Graduate Tracer System 1.0. It has been classified as critical. This affects the function mysqli_query of the file bsitemp.php. The manipulation of the argument id leads to sql injection. It is possible to initiate the attack remotely. The exploit has been disclosed to the public and may be used. The identifier VDB-222981 was assigned to this vulnerability. | 2023-03-14 | 9.8 | CVE-2023-1394 MISC MISC MISC |
| microsoft -- multiple_products | Remote Procedure Call Runtime Remote Code Execution Vulnerability | 2023-03-14 | 9.8 | CVE-2023-21708 MISC |
| microsoft -- multiple_products | HTTP Protocol Stack Remote Code Execution Vulnerability | 2023-03-14 | 9.8 | CVE-2023-23392 MISC |
| microsoft -- multiple_products | Microsoft Outlook Elevation of Privilege Vulnerability | 2023-03-14 | 9.8 | CVE-2023-23397 MISC |
| microsoft -- multiple_products | Internet Control Message Protocol (ICMP) Remote Code Execution Vulnerability | 2023-03-14 | 9.8 | CVE-2023-23415 MISC |
| samsung -- exynos_modem_5300_firmware | The Samsung Exynos Modem 5123, Exynos Modem 5300, Exynos 980, Exynos 1080, and Exynos Auto T512 baseband modem chipsets do not properly check format types specified by the Session Description Protocol (SDP) module, which can lead to a denial of service. | 2023-03-13 | 9.8 | CVE-2023-24033 MISC MISC |
| netiq -- advanced_authentication | Broken access control in Advanced Authentication versions prior to 6.4.1.1 and 6.3.7.2 | 2023-03-15 | 9.8 | CVE-2023-24468 MISC MISC |
| art_gallery_management_system_project -- art_gallery_management_system | Art Gallery Management System v1.0 was discovered to contain a SQL injection vulnerability via the viewid parameter on the enquiry page. | 2023-03-15 | 9.8 | CVE-2023-24726 MISC MISC MISC |
| dlink -- dir-867_firmware | OS Command injection vulnerability in D-Link DIR-867 DIR_867_FW1.30B07 allows attackers to execute arbitrary commands via a crafted LocalIPAddress parameter for the SetVirtualServerSettings to HNAP1. | 2023-03-13 | 9.8 | CVE-2023-24762 MISC MISC |
| funadmin -- funadmin | Funadmin v3.2.0 was discovered to contain a SQL injection vulnerability via the selectFields parameter at \controller\auth\Auth.php. | 2023-03-10 | 9.8 | CVE-2023-24774 MISC |
| trendmicro -- apex_one | An uncontrolled search path element vulnerability in the Trend Micro Apex One Server installer could allow an attacker to achieve a remote code execution state on affected products. | 2023-03-10 | 9.8 | CVE-2023-25143 MISC |
| prestashop -- dpd_france | PrestaShop dpdfrance <6.1.3 is vulnerable to SQL Injection via dpdfrance/ajax.php. | 2023-03-13 | 9.8 | CVE-2023-25207 MISC MISC |
| dlink -- dir-820l_firmware | OS Command injection vulnerability in D-Link DIR820LA1_FW105B03 allows attackers to escalate privileges to root via a crafted payload. | 2023-03-13 | 9.8 | CVE-2023-25279 MISC MISC |
| swig-templates_project -- swig-templates | An issue was discovered in swig-templates thru 2.0.4 and swig thru 1.4.2, allows attackers to execute arbitrary code via crafted Object.prototype anonymous function. | 2023-03-15 | 9.8 | CVE-2023-25344 MISC MISC |
| samsung -- exynos_850_firmware | An issue was discovered in Samsung Mobile Chipset and Baseband Modem Chipset for Exynos 850, Exynos 980, Exynos 1080, Exynos 1280, Exynos 2200, Exynos Modem 5123, Exynos Modem 5300, and Exynos Auto T5123. A heap-based buffer overflow in the 5G MM message codec can occur due to insufficient parameter validation when decoding the Emergency number list. | 2023-03-13 | 9.8 | CVE-2023-26072 MISC MISC MISC MISC MISC MISC |
| samsung -- exynos_850_firmware | An issue was discovered in Samsung Mobile Chipset and Baseband Modem Chipset for Exynos 850, Exynos 980, Exynos 1080, Exynos 1280, Exynos 2200, Exynos Modem 5123, Exynos Modem 5300, and Exynos Auto T5123. A heap-based buffer overflow in the 5G MM message codec can occur due to insufficient parameter validation when decoding the extended emergency number list. | 2023-03-13 | 9.8 | CVE-2023-26073 MISC MISC MISC MISC MISC MISC |
| samsung -- exynos_850_firmware | An issue was discovered in Samsung Mobile Chipset and Baseband Modem Chipset for Exynos 850, Exynos 980, Exynos 1080, Exynos 1280, Exynos 2200, Exynos Modem 5123, Exynos Modem 5300, and Exynos Auto T5123.. A heap-based buffer overflow in the 5G MM message codec can occur due to insufficient parameter validation when decoding operator-defined access category definitions. | 2023-03-13 | 9.8 | CVE-2023-26074 MISC MISC MISC MISC MISC MISC |
| samsung -- exynos_850_firmware | An issue was discovered in Samsung Mobile Chipset and Baseband Modem Chipset for Exynos 850, Exynos 980, Exynos 1080, Exynos 1280, Exynos 2200, Exynos Modem 5123, Exynos Modem 5300, and Exynos Auto T5123. An intra-object overflow in the 5G MM message codec can occur due to insufficient parameter validation when decoding the Service Area List. | 2023-03-10 | 9.8 | CVE-2023-26075 MISC MISC MISC MISC MISC MISC |
| samsung -- exynos_1280_firmware | An issue was discovered in Samsung Mobile Chipset and Baseband Modem Chipset for Exynos 1280, Exynos 2200, Exynos Modem 5123, Exynos Modem 5300, and Exynos Auto T5123. An intra-object overflow in the 5G SM message codec can occur due to insufficient parameter validation when decoding reserved options. | 2023-03-13 | 9.8 | CVE-2023-26076 MISC MISC MISC MISC |
| moosikay_project -- moosikay | E-Commerce System v1.0 ws discovered to contain a SQL injection vulnerability via the id parameter at /admin/delete_user.php. | 2023-03-13 | 9.8 | CVE-2023-27052 MISC |
| tenda -- w15e_firmware | Tenda V15V1.0 V15.11.0.14(1521_3190_1058) was discovered to contain a buffer overflow vulnerability via the wifiFilterListRemark parameter in the modifyWifiFilterRules function. This vulnerability allows attackers to cause a Denial of Service (DoS) via a crafted request. | 2023-03-13 | 9.8 | CVE-2023-27061 MISC |
| tenda -- w15e_firmware | Tenda V15V1.0 V15.11.0.14(1521_3190_1058) was discovered to contain a buffer overflow vulnerability via the DNSDomainName parameter in the formModifyDnsForward function. This vulnerability allows attackers to cause a Denial of Service (DoS) via a crafted request. | 2023-03-13 | 9.8 | CVE-2023-27063 MISC |
| bp_monitoring_management_system_project -- bp_monitoring_management_system | BP Monitoring Management System v1.0 was discovered to contain a SQL injection vulnerability via the emailid parameter in the login page. | 2023-03-14 | 9.8 | CVE-2023-27074 MISC |
| maddy_project -- maddy | maddy is a composable, all-in-one mail server. Starting with version 0.2.0 and prior to version 0.6.3, maddy allows a full authentication bypass if SASL authorization username is specified when using the PLAIN authentication mechanisms. Instead of validating the specified username, it is accepted as is after checking the credentials for the authentication username. maddy 0.6.3 includes the fix for the bug. There are no known workarounds. | 2023-03-13 | 9.8 | CVE-2023-27582 MISC MISC MISC MISC |
| panindex_project -- panindex | PanIndex is a network disk directory index. In Panindex prior to version 3.1.3, a hard-coded JWT key PanIndex is used. An attacker can use the hard-coded JWT key to sign JWT token and perform any actions as a user with admin privileges. Version 3.1.3 has a patch for the issue. As a workaround, one may change the JWT key in the source code before compiling the project. |
2023-03-13 | 9.8 | CVE-2023-27583 MISC MISC MISC |
| perfree -- perfreeblog | An arbitrary file upload vulnerability in the /admin/user/uploadImg component of PerfreeBlog v3.1.1 allows attackers to execute arbitrary code via a crafted JPG file. | 2023-03-15 | 9.8 | CVE-2023-27757 MISC |
| netgear -- rax30_firmware | NETGEAR Nighthawk WiFi6 Router prior to V1.0.10.94 contains a buffer overflow vulnerability in various CGI mechanisms that could allow an attacker to execute arbitrary code on the device. | 2023-03-10 | 9.8 | CVE-2023-27852 MISC |
| netgear -- rax30_firmware | NETGEAR Nighthawk WiFi6 Router prior to V1.0.10.94 contains a format string vulnerability in a SOAP service that could allow an attacker to execute arbitrary code on the device. | 2023-03-10 | 9.8 | CVE-2023-27853 MISC |
| webpack.js -- webpack | Webpack 5 before 5.76.0 does not avoid cross-realm object access. ImportParserPlugin.js mishandles the magic comment feature. An attacker who controls a property of an untrusted object can obtain access to the real global object. | 2023-03-13 | 9.8 | CVE-2023-28154 MISC MISC |
| sap -- netweaver_application_server_abap | SAP NetWeaver AS for ABAP and ABAP Platform - versions 700, 701, 702, 731, 740, 750, 751, 752, 753, 754, 755, 756, 757, 791, allows an attacker to exploit insufficient validation of path information provided by users, thus exploiting a directory traversal flaw in an available service to delete system files. In this attack, no data can be read but potentially critical OS files can be deleted making the system unavailable, causing significant impact on both availability and integrity | 2023-03-14 | 9.6 | CVE-2023-27501 MISC MISC |
| akuvox -- e11_firmware | The Akuvox E11 libvoice library provides unauthenticated access to the camera capture for image and video. This could allow an attacker to view and record image and video from the camera. | 2023-03-13 | 9.1 | CVE-2023-0349 MISC |
| akuvox -- e11_firmware | The Akuvox E11 password recovery webpage can be accessed without authentication, and an attacker could download the device key file. An attacker could then use this page to reset the password back to the default. | 2023-03-13 | 9.1 | CVE-2023-0352 MISC |
| akuvox -- e11_firmware | The Akuvox E11 web server can be accessed without any user authentication, and this could allow an attacker to access sensitive information, as well as create and download packet captures with known default URLs. | 2023-03-13 | 9.1 | CVE-2023-0354 MISC |
| siemens -- mendix_saml | A vulnerability has been identified in Mendix SAML (Mendix 7 compatible) (All Versions >= 1.16.4 < 1.17.2), Mendix SAML (Mendix 8 compatible) (All versions >= 2.2.0 < 2.2.3), Mendix SAML (Mendix 9 compatible, New Track) (All versions >= 3.1.9 < 3.2.5), Mendix SAML (Mendix 9 compatible, Upgrade Track) (All versions >= 3.1.9 < 3.2.5). The affected versions of the module insufficiently verifies the SAML assertions. This could allow unauthenticated remote attackers to bypass authentication and get access to the application. | 2023-03-14 | 9.1 | CVE-2023-25957 MISC |
| ibm -- financial_transaction_manager | IBM Financial Transaction Manager 3.2.0 through 3.2.10 could allow an authenticated user to perform unauthorized actions due to improper validation. IBM X-Force ID: 192954. | 2023-03-10 | 8.8 | CVE-2020-5002 MISC MISC |
| qualcomm -- apq8009_firmware | Memory corruption in modem due to buffer overflow while processing a PPP packet | 2023-03-10 | 8.8 | CVE-2022-33213 MISC |
| veronalabs -- wp_statistics | SQL Injection vulnerability in VeronaLabs WP Statistics plugin <= 13.2.10 versions. | 2023-03-13 | 8.8 | CVE-2022-38074 MISC |
| richplugins -- plugin_for_google_reviews | SQL Injection (SQLi) vulnerability in RichPlugins Plugin for Google Reviews plugin <= 2.2.3 versions. | 2023-03-15 | 8.8 | CVE-2022-44580 MISC |
| seerox -- wp_dynamic_keywords_injector | Cross-Site Request Forgery (CSRF) vulnerability in Seerox WP Dynamic Keywords Injector plugin <= 2.3.15 versions. | 2023-03-14 | 8.8 | CVE-2022-47141 MISC |
| themeisle -- multiple_page_generator | Cross-Site Request Forgery (CSRF) vulnerability in Themeisle Multiple Page Generator Plugin – MPG plugin <= 3.3.9 versions. | 2023-03-14 | 8.8 | CVE-2022-47143 MISC |
| kesz1 -- ipblocklist | Cross-Site Request Forgery (CSRF) vulnerability in Kesz1 Technologies ipBlockList plugin <= 1.0 versions. | 2023-03-14 | 8.8 | CVE-2022-47147 MISC |
| piwebsolution -- css_js_manager,_async_javascript,_defer_render_blocking_css_supports_woocommerce | Cross-Site Request Forgery (CSRF) vulnerability in Pi Websolution CSS JS Manager, Async JavaScript, Defer Render Blocking CSS supports WooCommerce plugin <= 2.4.49 versions. | 2023-03-14 | 8.8 | CVE-2022-47154 MISC |
| supsystic -- slider | Cross-Site Request Forgery (CSRF) vulnerability in Supsystic Slider by Supsystic plugin <= 1.8.5 versions. | 2023-03-14 | 8.8 | CVE-2022-47155 MISC |
| dh_-anti_adblocker_project -- dh-_anti_adblocker | Cross-Site Request Forgery (CSRF) vulnerability in Dannie Herdyawan DH – Anti AdBlocker plugin <= 36 versions. | 2023-03-14 | 8.8 | CVE-2022-47162 MISC |
| voidcoders -- void_contact_form_7_widget_for_elementor_page_builder | Cross-Site Request Forgery (CSRF) vulnerability in voidCoders Void Contact Form 7 Widget For Elementor Page Builder plugin <= 2.1.1 versions. | 2023-03-13 | 8.8 | CVE-2022-47166 MISC |
| hmplugin -- accept_stripe_donation_-_aidwp | Cross-Site Request Forgery (CSRF) vulnerability in HM Plugin Accept Stripe Donation – AidWP plugin <= 3.1.5 versions. | 2023-03-14 | 8.8 | CVE-2022-47422 MISC |
| my_calendar_project -- my_calendar | Cross-Site Request Forgery (CSRF) vulnerability in Joseph C Dolson My Calendar plugin <= 3.3.24.1 versions. | 2023-03-15 | 8.8 | CVE-2022-47427 MISC |
| my_tickets_project -- my_tickets | Cross-Site Request Forgery (CSRF) vulnerability in Joseph C Dolson My Tickets plugin <= 1.9.10 versions. | 2023-03-13 | 8.8 | CVE-2022-47440 MISC |
| multi_rating_project -- multi_rating | Cross-Site Request Forgery (CSRF) vulnerability in Daniel Powney Multi Rating plugin <= 5.0.5 versions. | 2023-03-14 | 8.8 | CVE-2022-47443 MISC |
| akuvox -- e11_firmware | The Akuvox E11 web server backend library allows command injection in the device phone-book contacts functionality. This could allow an attacker to upload files with executable command instructions. | 2023-03-13 | 8.8 | CVE-2023-0351 MISC |
| cm-wp -- auto_featured_image | The Auto Featured Image (Auto Post Thumbnail) WordPress plugin before 3.9.16 includes an AJAX endpoint that allows any user with at least Author privileges to upload arbitrary files, such as PHP files. This is caused by incorrect file extension validation. | 2023-03-13 | 8.8 | CVE-2023-0477 MISC |
| netgear -- rax30_firmware | NETGEAR Nighthawk WiFi6 Router prior to V1.0.10.94 is vulnerable to cross-site request forgery attacks on all endpoints due to improperly implemented CSRF protections. | 2023-03-10 | 8.8 | CVE-2023-1205 MISC |
| hashicorp -- nomad | HashiCorp Nomad and Nomad Enterprise 1.5.0 allow a job submitter to escalate to management-level privileges using workload identity and task API. Fixed in 1.5.1. | 2023-03-14 | 8.8 | CVE-2023-1299 MISC |
| agentejo -- cockpit | Unrestricted Upload of File with Dangerous Type in GitHub repository cockpit-hq/cockpit prior to 2.4.1. | 2023-03-10 | 8.8 | CVE-2023-1313 CONFIRM MISC |
| teacms_project -- teacms | A vulnerability classified as critical was found in XiaoBingBy TeaCMS 2.0. Affected by this vulnerability is an unknown functionality of the file /admin/upload. The manipulation leads to path traversal: '../filedir'. The attack can be launched remotely. The exploit has been disclosed to the public and may be used. The identifier VDB-222985 was assigned to this vulnerability. | 2023-03-14 | 8.8 | CVE-2023-1398 MISC MISC MISC |
| simple_art_gallery_project -- simple_art_gallery | A vulnerability was found in Simple Art Gallery 1.0. It has been declared as critical. This vulnerability affects the function sliderPicSubmit of the file adminHome.php. The manipulation leads to unrestricted upload. The attack can be initiated remotely. VDB-223126 is the identifier assigned to this vulnerability. | 2023-03-15 | 8.8 | CVE-2023-1415 MISC MISC MISC |
| avantfax -- avantfax | A File Upload vulnerability exists in AvantFAX 3.3.7. An authenticated user can bypass PHP file type validation in FileUpload.php by uploading a specially crafted PHP file. | 2023-03-10 | 8.8 | CVE-2023-23328 MISC MISC |
| microsoft -- multiple_products | Windows Bluetooth Driver Elevation of Privilege Vulnerability | 2023-03-14 | 8.8 | CVE-2023-23388 MISC |
| microsoft -- multiple_products | Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability | 2023-03-14 | 8.8 | CVE-2023-23403 MISC |
| microsoft -- multiple_products | Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability | 2023-03-14 | 8.8 | CVE-2023-23406 MISC |
| microsoft -- multiple_products | Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability | 2023-03-14 | 8.8 | CVE-2023-23413 MISC |
| simple_customer_relationship_management_system_project -- simple_customer_relationship_management_system | Simple Customer Relationship Management System v1.0 as discovered to contain a SQL injection vulnerability via the contact parameter in the user profile update function. | 2023-03-15 | 8.8 | CVE-2023-24728 MISC MISC MISC |
| simple_customer_relationship_management_system_project -- simple_customer_relationship_management_system | Simple Customer Relationship Management System v1.0 as discovered to contain a SQL injection vulnerability via the address parameter in the user profile update function. | 2023-03-15 | 8.8 | CVE-2023-24729 MISC MISC MISC |
| simple_customer_relationship_management_system_project -- simple_customer_relationship_management_system | Simple Customer Relationship Management System v1.0 as discovered to contain a SQL injection vulnerability via the company parameter in the user profile update function. | 2023-03-15 | 8.8 | CVE-2023-24730 MISC MISC MISC |
| simple_customer_relationship_management_system_project -- simple_customer_relationship_management_system | Simple Customer Relationship Management System v1.0 as discovered to contain a SQL injection vulnerability via the query parameter in the user profile update function. | 2023-03-15 | 8.8 | CVE-2023-24731 MISC MISC MISC |
| simple_customer_relationship_management_system_project -- simple_customer_relationship_management_system | Simple Customer Relationship Management System v1.0 as discovered to contain a SQL injection vulnerability via the gender parameter in the user profile update function. | 2023-03-15 | 8.8 | CVE-2023-24732 MISC MISC MISC |
| microsoft -- multiple_products | Microsoft PostScript and PCL6 Class Printer Driver Elevation of Privilege Vulnerability | 2023-03-14 | 8.8 | CVE-2023-24864 MISC |
| microsoft -- multiple_products | Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability | 2023-03-14 | 8.8 | CVE-2023-24867 MISC |
| microsoft -- multiple_products | Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability | 2023-03-14 | 8.8 | CVE-2023-24868 MISC |
| microsoft -- multiple_products | Windows Bluetooth Service Remote Code Execution Vulnerability | 2023-03-14 | 8.8 | CVE-2023-24871 MISC |
| microsoft -- multiple_products | Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability | 2023-03-14 | 8.8 | CVE-2023-24872 MISC |
| microsoft -- multiple_products | Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability | 2023-03-14 | 8.8 | CVE-2023-24876 MISC |
| microsoft -- multiple_products | Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability | 2023-03-14 | 8.8 | CVE-2023-24907 MISC |
| microsoft -- multiple_products | Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability | 2023-03-14 | 8.8 | CVE-2023-24909 MISC |
| microsoft -- multiple_products | Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability | 2023-03-14 | 8.8 | CVE-2023-24913 MISC |
| prestashop -- advanced_reviews | PrestaShop ws_productreviews < 3.6.2 is vulnerable to SQL Injection. | 2023-03-14 | 8.8 | CVE-2023-25206 MISC MISC |
| sap -- business_objects_business_intelligence_platform | In some scenario, SAP Business Objects Business Intelligence Platform (CMC) - versions 420, 430, Program Object execution can lead to code injection vulnerability which could allow an attacker to gain access to resources that are allowed by extra privileges. Successful attack could highly impact the confidentiality, Integrity, and Availability of the system. | 2023-03-14 | 8.8 | CVE-2023-25616 MISC MISC |
| sap -- business_objects_business_intelligence_platform | SAP Business Object (Adaptive Job Server) - versions 420, 430, allows remote execution of arbitrary commands on Unix, when program objects execution is enabled, to authenticated users with scheduling rights, using the BI Launchpad, Central Management Console or a custom application based on the public java SDK. Programs could impact the confidentiality, integrity and availability of the system. | 2023-03-14 | 8.8 | CVE-2023-25617 MISC MISC |
| coderex -- wp_vr | Cross-Site Request Forgery (CSRF) vulnerability in Rextheme WP VR – 360 Panorama and Virtual Tour Builder For WordPress plugin <= 8.2.7 versions. | 2023-03-15 | 8.8 | CVE-2023-25708 MISC |
| plainware -- locatoraid | Cross-Site Request Forgery (CSRF) vulnerability in Plainware Locatoraid Store Locator plugin <= 3.9.11 versions. | 2023-03-15 | 8.8 | CVE-2023-25709 MISC |
| cozmoslabs -- client_portal | Cross-Site Request Forgery (CSRF) vulnerability in Cozmoslabs, Madalin Ungureanu, Antohe Cristian Client Portal – Private user pages and login plugin <= 1.1.8 versions. | 2023-03-15 | 8.8 | CVE-2023-25968 MISC |
| autoaffiliatelinks -- auto_affiliate_links | Cross-Site Request Forgery (CSRF) vulnerability in Lucian Apostol Auto Affiliate Links plugin <= 6.3.0.2 versions. | 2023-03-13 | 8.8 | CVE-2023-25973 MISC |
| metagauss -- registrationmagic | Cross-Site Request Forgery (CSRF) vulnerability in RegistrationMagic plugin <= 5.1.9.2 versions. | 2023-03-13 | 8.8 | CVE-2023-25991 MISC |
| ibm -- mq_certified_container | IBM MQ Certified Container 9.3.0.1 through 9.3.0.3 and 9.3.1.0 through 9.3.1.1 could allow authenticated users with the cluster to be granted administration access to the MQ console due to improper access controls. IBM X-Force ID: 248417. | 2023-03-15 | 8.8 | CVE-2023-26284 MISC MISC |
| struktur -- libde265 | Libde265 v1.0.11 was discovered to contain a heap buffer overflow via the function derive_collocated_motion_vectors at motion.cc. | 2023-03-15 | 8.8 | CVE-2023-27103 MISC |
| siemens -- ruggedcom_crossbow | A vulnerability has been identified in RUGGEDCOM CROSSBOW (All versions < V5.2). The client query handler of the affected application fails to check for proper permissions for specific write queries. This could allow an authenticated remote attacker to perform unauthorized actions. | 2023-03-14 | 8.8 | CVE-2023-27309 MISC |
| siemens -- ruggedcom_crossbow | A vulnerability has been identified in RUGGEDCOM CROSSBOW (All versions < V5.2). The client query handler of the affected application fails to check for proper permissions when assigning groups to user accounts. This could allow an authenticated remote attacker to assign administrative groups to otherwise non-privileged user accounts. | 2023-03-14 | 8.8 | CVE-2023-27310 MISC |
| siemens -- ruggedcom_crossbow | A vulnerability has been identified in RUGGEDCOM CROSSBOW (All versions < V5.3). The audit log form of affected applications is vulnerable to SQL injection. This could allow authenticated remote attackers to execute arbitrary SQL queries on the server database. | 2023-03-14 | 8.8 | CVE-2023-27463 MISC |
| github-slug-action_project -- github-slug-action | github-slug-action is a GitHub Action to expose slug value of GitHub environment variables inside of one's GitHub workflow. Starting in version 4.0.0and prior to version 4.4.1, this action uses thegithub.head_ref` parameter in an insecure way. This vulnerability can be triggered by any user on GitHub on any workflow using the action on pull requests. They just need to create a pull request with a branch name, which can contain the attack payload. This can be used to execute code on the GitHub runners and to exfiltrate any secrets one uses in the CI pipeline. A patched action is available in version 4.4.1. No workaround is available. |
2023-03-13 | 8.8 | CVE-2023-27581 MISC MISC MISC MISC |
| netgear -- rax30_firmware | NETGEAR Nighthawk WiFi6 Router prior to V1.0.10.94 contains a file sharing mechanism that unintentionally allows users with upload permissions to execute arbitrary code on the device. | 2023-03-10 | 8.8 | CVE-2023-27851 MISC |
| sap -- netweaver_application_server_for_java | Due to missing authentication check, SAP NetWeaver AS for Java - version 7.50, allows an unauthenticated attacker to attach to an open interface and make use of an open naming and directory API to access services which can be used to perform unauthorized operations affecting users and services across systems. On a successful exploitation, the attacker can read and modify some sensitive information but can also be used to lock up any element or operation of the system making that it unresponsive or unavailable. | 2023-03-14 | 8.6 | CVE-2023-23857 MISC MISC |
| microsoft -- multiple_products | Windows Cryptographic Services Remote Code Execution Vulnerability | 2023-03-14 | 8.4 | CVE-2023-23416 MISC |
| ibm -- spectrum_scale | A vulnerability in the Spectrum Scale 5.0.5.0 through 5.1.6.1 core component could allow unauthorized access to user data or injection of arbitrary data in the communication protocol. IBM X-Force ID: 191695. | 2023-03-15 | 8.2 | CVE-2020-4927 MISC MISC |
| microsoft -- azure_service_fabric | Service Fabric Explorer Spoofing Vulnerability | 2023-03-14 | 8.2 | CVE-2023-23383 MISC |
| microsoft -- multiple_products | Windows Point-to-Point Tunneling Protocol Remote Code Execution Vulnerability | 2023-03-14 | 8.1 | CVE-2023-23404 MISC |
| microsoft -- multiple_products | Remote Procedure Call Runtime Remote Code Execution Vulnerability | 2023-03-14 | 8.1 | CVE-2023-23405 MISC |
| microsoft -- multiple_products | Remote Procedure Call Runtime Remote Code Execution Vulnerability | 2023-03-14 | 8.1 | CVE-2023-24869 MISC |
| microsoft -- multiple_products | Remote Procedure Call Runtime Remote Code Execution Vulnerability | 2023-03-14 | 8.1 | CVE-2023-24908 MISC |
| hashicorp -- vault | HashiCorp Vault and Vault Enterprise’s approle auth method allowed any authenticated user with access to an approle destroy endpoint to destroy the secret ID of any other role by providing the secret ID accessor. This vulnerability is fixed in Vault 1.13.0, 1.12.4, 1.11.8, 1.10.11 and above. | 2023-03-11 | 8.1 | CVE-2023-24999 MISC |
| cisco -- enterprise_nfv_infrastructure_software | A vulnerability in the upgrade signature verification of Cisco Enterprise NFV Infrastructure Software (NFVIS) could allow an unauthenticated, local attacker to provide an unauthentic upgrade file for upload. This vulnerability is due to insufficient cryptographic signature verification of upgrade files. An attacker could exploit this vulnerability by providing an administrator with an unauthentic upgrade file. A successful exploit could allow the attacker to fully compromise the Cisco NFVIS system. | 2023-03-10 | 7.8 | CVE-2022-20929 MISC |
| qualcomm -- apq8009_firmware | Memory corruption in WLAN HAL while arbitrary value is passed in WMI UTF command payload. | 2023-03-10 | 7.8 | CVE-2022-25655 MISC |
| qualcomm -- apq8009w_firmware | Memory corruption in Modem due to usage of Out-of-range pointer offset in UIM | 2023-03-10 | 7.8 | CVE-2022-25694 MISC |
| qualcomm -- apq8009_firmware | Memory corruption in modem due to integer overflow to buffer overflow while handling APDU response | 2023-03-10 | 7.8 | CVE-2022-25705 MISC |
| qualcomm -- ar8035_firmware | Memory corruption in modem due to use of out of range pointer offset while processing qmi msg | 2023-03-10 | 7.8 | CVE-2022-25709 MISC |
| qualcomm -- aqt1000_firmware | Memory corruption due to improper authentication in Qualcomm IPC while loading unsigned lib in audio PD. | 2023-03-10 | 7.8 | CVE-2022-33242 MISC |
| qualcomm -- apq8064au_firmware | Memory corruption in WLAN due to use after free | 2023-03-10 | 7.8 | CVE-2022-33245 MISC |
| qualcomm -- aqt1000_firmware | Memory corruption due to stack based buffer overflow in core while sending command from USB of large size. | 2023-03-10 | 7.8 | CVE-2022-33260 MISC |
| qualcomm -- aqt1000_firmware | Memory corruption due to buffer copy without checking the size of input in HLOS when input message size is larger than the buffer capacity. | 2023-03-10 | 7.8 | CVE-2022-33278 MISC |
| qualcomm -- aqt1000_firmware | Memory corruption in WLAN due to integer overflow to buffer overflow in WLAN during initialization phase. | 2023-03-10 | 7.8 | CVE-2022-40530 MISC |
| qualcomm -- apq8009_firmware | Memory corruption in WLAN due to incorrect type cast while sending WMI_SCAN_SCH_PRIO_TBL_CMDID message. | 2023-03-10 | 7.8 | CVE-2022-40531 MISC |
| qualcomm -- qam8295p_firmware | Memory corruption in Automotive Android OS due to improper validation of array index. | 2023-03-10 | 7.8 | CVE-2022-40539 MISC |
| qualcomm -- sd_8_gen1_5g_firmware | Memory corruption due to buffer copy without checking the size of input while loading firmware in Linux Kernel. | 2023-03-10 | 7.8 | CVE-2022-40540 MISC |
| docker -- docker_desktop | Docker Desktop before 4.17.0 allows an attacker to execute an arbitrary command inside a Dev Environments container during initialization by tricking a user to open a crafted malicious docker-desktop:// URL. | 2023-03-13 | 7.8 | CVE-2023-0628 MISC |
| openharmony -- openharmony | The kernel subsystem function check_permission_for_set_tokenid within OpenHarmony-v3.1.5 and prior versions has an UAF vulnerability which local attackers can exploit this vulnerability to escalate the privilege to root. | 2023-03-10 | 7.8 | CVE-2023-22436 MISC |
| microsoft -- multiple_products | Microsoft Excel Remote Code Execution Vulnerability | 2023-03-14 | 7.8 | CVE-2023-23399 MISC |
| microsoft -- multiple_products | Windows Media Remote Code Execution Vulnerability | 2023-03-14 | 7.8 | CVE-2023-23401 MISC |
| microsoft -- multiple_products | Windows Media Remote Code Execution Vulnerability | 2023-03-14 | 7.8 | CVE-2023-23402 MISC |
| microsoft -- multiple_products | Windows HTTP.sys Elevation of Privilege Vulnerability | 2023-03-14 | 7.8 | CVE-2023-23410 MISC |
| microsoft -- multiple_products | Windows Accounts Picture Elevation of Privilege Vulnerability | 2023-03-14 | 7.8 | CVE-2023-23412 MISC |
| microsoft -- multiple_products | Windows Partition Management Driver Elevation of Privilege Vulnerability | 2023-03-14 | 7.8 | CVE-2023-23417 MISC |
| microsoft -- windows_11 | Windows Resilient File System (ReFS) Elevation of Privilege Vulnerability | 2023-03-14 | 7.8 | CVE-2023-23418 MISC |
| microsoft -- windows_11 | Windows Resilient File System (ReFS) Elevation of Privilege Vulnerability | 2023-03-14 | 7.8 | CVE-2023-23419 MISC |
| microsoft -- windows_server_2012 | Windows Kernel Elevation of Privilege Vulnerability | 2023-03-14 | 7.8 | CVE-2023-23420 MISC |
| microsoft -- windows_server_2012 | Windows Kernel Elevation of Privilege Vulnerability | 2023-03-14 | 7.8 | CVE-2023-23421 MISC |
| microsoft -- windows_server_2012 | Windows Kernel Elevation of Privilege Vulnerability | 2023-03-14 | 7.8 | CVE-2023-23422 MISC |
| microsoft -- windows_server_2012 | Windows Kernel Elevation of Privilege Vulnerability | 2023-03-14 | 7.8 | CVE-2023-23423 MISC |
| draytek -- vigor2960_firmware | DrayTek Vigor2960 v1.5.1.4 was discovered to contain a command injection vulnerability via the mainfunction.cgi component. | 2023-03-15 | 7.8 | CVE-2023-24229 MISC MISC |
| microsoft -- multiple_products | Windows Graphics Component Elevation of Privilege Vulnerability | 2023-03-14 | 7.8 | CVE-2023-24910 MISC |
| microsoft -- onedrive_for_macos | Microsoft OneDrive for MacOS Elevation of Privilege Vulnerability | 2023-03-14 | 7.8 | CVE-2023-24930 MISC |
| trendmicro -- apex_one | An improper access control vulnerability in the Trend Micro Apex One agent could allow a local attacker to gain elevated privileges and create arbitrary directories with arbitrary ownership. | 2023-03-10 | 7.8 | CVE-2023-25144 MISC MISC |
| trendmicro -- apex_one | A link following vulnerability in the scanning function of Trend Micro Apex One agent could allow a local attacker to escalate privileges on affected installations. Please note: an attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. | 2023-03-10 | 7.8 | CVE-2023-25145 MISC MISC |
| trendmicro -- apex_one | A security agent link following vulnerability in the Trend Micro Apex One agent could allow a local attacker to quarantine a file, delete the original folder and replace with a junction to an arbitrary location, ultimately leading to an arbitrary file dropped to an arbitrary location. Please note: an attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. | 2023-03-10 | 7.8 | CVE-2023-25146 MISC MISC |
| trendmicro -- apex_one | A security agent link following vulnerability in Trend Micro Apex One could allow a local attacker to exploit the vulnerability by changing a specific file into a pseudo-symlink, allowing privilege escalation on affected installations. Please note: an attacker must first obtain the ability to execute low-privileged code on the target system in order to exploit this vulnerability. | 2023-03-10 | 7.8 | CVE-2023-25148 MISC MISC |
| webassembly -- webassembly | WebAssembly v1.0.29 was discovered to contain a heap overflow via the component component wabt::Node::operator. | 2023-03-10 | 7.8 | CVE-2023-27117 MISC |
| siemens -- tecnomatix_plant_simulation | A vulnerability has been identified in Tecnomatix Plant Simulation (All versions < V2201.0006). The affected application contains an out of bounds write past the end of an allocated buffer while parsing a specially crafted SPP file. This could allow an attacker to execute code in the context of the current process. (ZDI-CAN-20304) | 2023-03-14 | 7.8 | CVE-2023-27398 MISC |
| siemens -- tecnomatix_plant_simulation | A vulnerability has been identified in Tecnomatix Plant Simulation (All versions < V2201.0006). The affected application contains an out of bounds write past the end of an allocated buffer while parsing a specially crafted SPP file. This could allow an attacker to execute code in the context of the current process. (ZDI-CAN-20299, ZDI-CAN-20346) | 2023-03-14 | 7.8 | CVE-2023-27399 MISC |
| siemens -- tecnomatix_plant_simulation | A vulnerability has been identified in Tecnomatix Plant Simulation (All versions < V2201.0006). The affected application contains an out of bounds write past the end of an allocated buffer while parsing a specially crafted SPP file. This could allow an attacker to execute code in the context of the current process. (ZDI-CAN-20300) | 2023-03-14 | 7.8 | CVE-2023-27400 MISC |
| siemens -- tecnomatix_plant_simulation | A vulnerability has been identified in Tecnomatix Plant Simulation (All versions < V2201.0006). The affected applications contain an out of bounds read past the end of an allocated structure while parsing specially crafted SPP files. This could allow an attacker to execute code in the context of the current process. (ZDI-CAN-20308, ZDI-CAN-20345) | 2023-03-14 | 7.8 | CVE-2023-27401 MISC |
| siemens -- tecnomatix_plant_simulation | A vulnerability has been identified in Tecnomatix Plant Simulation (All versions < V2201.0006). The affected applications contain an out of bounds read past the end of an allocated structure while parsing specially crafted SPP files. This could allow an attacker to execute code in the context of the current process. (ZDI-CAN-20334) | 2023-03-14 | 7.8 | CVE-2023-27402 MISC |
| siemens -- tecnomatix_plant_simulation | A vulnerability has been identified in Tecnomatix Plant Simulation (All versions < V2201.0006). The affected application contains a memory corruption vulnerability while parsing specially crafted SPP files. This could allow an attacker to execute code in the context of the current process. (ZDI-CAN-20303, ZDI-CAN-20348) | 2023-03-14 | 7.8 | CVE-2023-27403 MISC |
| siemens -- tecnomatix_plant_simulation | A vulnerability has been identified in Tecnomatix Plant Simulation (All versions < V2201.0006). The affected application is vulnerable to stack-based buffer while parsing specially crafted SPP files. An attacker could leverage this vulnerability to execute code in the context of the current process. (ZDI-CAN-20433) | 2023-03-14 | 7.8 | CVE-2023-27404 MISC |
| siemens -- tecnomatix_plant_simulation | A vulnerability has been identified in Tecnomatix Plant Simulation (All versions < V2201.0006). The affected applications contain an out of bounds read past the end of an allocated structure while parsing specially crafted SPP files. This could allow an attacker to execute code in the context of the current process. (ZDI-CAN-20432) | 2023-03-14 | 7.8 | CVE-2023-27405 MISC |
| siemens -- tecnomatix_plant_simulation | A vulnerability has been identified in Tecnomatix Plant Simulation (All versions < V2201.0006). The affected application is vulnerable to stack-based buffer while parsing specially crafted SPP files. An attacker could leverage this vulnerability to execute code in the context of the current process. (ZDI-CAN-20449) | 2023-03-14 | 7.8 | CVE-2023-27406 MISC |
| jpegoptim_project -- jpegoptim | jpegoptim v1.5.2 was discovered to contain a heap overflow in the optimize function at jpegoptim.c. | 2023-03-15 | 7.8 | CVE-2023-27781 MISC |
| getadmiral -- ad_blocking_detector | A vulnerability has been found in Ad Blocking Detector Plugin up to 1.2.1 and classified as problematic. This vulnerability affects unknown code of the file ad-blocking-detector.php. The manipulation leads to information disclosure. The attack can be initiated remotely. Upgrading to version 1.2.2 is able to address this issue. The name of the patch is 3312b9cd79e5710d1e282fc9216a4e5ab31b3d94. It is recommended to upgrade the affected component. VDB-222610 is the identifier assigned to this vulnerability. | 2023-03-10 | 7.5 | CVE-2014-125093 MISC MISC MISC MISC |
| ithemes -- backupbuddy | Directory Traversal vulnerability in iThemes BackupBuddy plugin 8.5.8.0 - 8.7.4.1 versions. | 2023-03-13 | 7.5 | CVE-2022-31474 MISC MISC |
| qualcomm -- ar8035_firmware | Transient DOS due to reachable assertion in modem during MIB reception and SIB timeout | 2023-03-10 | 7.5 | CVE-2022-33244 MISC |
| qualcomm -- ar8035_firmware | Transient DOS due to reachable assertion in modem when network repeatedly sent invalid message container for NR to LTE handover. | 2023-03-10 | 7.5 | CVE-2022-33250 MISC |
| qualcomm -- aqt1000_firmware | Transient DOS due to reachable assertion in Modem while processing SIB1 Message. | 2023-03-10 | 7.5 | CVE-2022-33254 MISC |
| qualcomm -- ar8035_firmware | Transient DOS in modem due to reachable assertion. | 2023-03-10 | 7.5 | CVE-2022-33272 MISC |
| qualcomm -- csr8811_firmware | Transient DOS due to buffer over-read in WLAN Firmware while parsing secure FTMR frame with size lesser than 39 Bytes. | 2023-03-10 | 7.5 | CVE-2022-33309 MISC |
| ajax_search_project -- ajax_search | Exposure of Sensitive Information to an Unauthorized Actor vulnerability in Ernest Marcinko Ajax Search Lite plugin <= 4.10.3 versions. | 2023-03-15 | 7.5 | CVE-2022-38456 MISC |
| combodo -- itop | Combodo iTop is an open source, web-based IT service management platform. Prior to versions 2.7.8 and 3.0.2-1, a user who can log in on iTop is able to take over any account just by knowing the account's username. This issue is fixed in versions 2.7.8 and 3.0.2-1. | 2023-03-14 | 7.5 | CVE-2022-39214 MISC MISC MISC |
| qualcomm -- ar8035_firmware | Transient DOS due to reachable assertion in WLAN while processing PEER ID populated by TQM. | 2023-03-10 | 7.5 | CVE-2022-40527 MISC |
| qualcomm -- csr8811_firmware | Transient DOS due to buffer over-read in WLAN while sending a packet to device. | 2023-03-10 | 7.5 | CVE-2022-40535 MISC |
| ibm -- mq_appliance | IBM MQ 9.2 CD, 9.2 LTS, 9.3 CD, and 9.3 LTS is vulnerable to a denial of service attack caused by specially crafted PCF or MQSC messages. IBM X-Force ID: 240832. | 2023-03-10 | 7.5 | CVE-2022-43902 MISC MISC |
| ivanti -- avalanche | An improper authentication vulnerability exists in Avalanche version 6.3.x and below allows unauthenticated attacker to modify properties on specific port. | 2023-03-10 | 7.5 | CVE-2022-44574 MISC |
| wp_csv_to_database_project -- wp_csv_to_database | Cross-Site Request Forgery (CSRF) vulnerability in Tips and Tricks HQ, josh401 WP CSV to Database – Insert CSV file content into WordPress plugin <= 2.6 versions. | 2023-03-14 | 7.5 | CVE-2022-47163 MISC |
| akuvox -- e11_firmware | Akuvox E11 cloud login is performed through an unencrypted HTTP connection. An attacker could gain access to the Akuvox cloud and device if the MAC address of a device if known. | 2023-03-13 | 7.5 | CVE-2023-0346 MISC |
| akuvox -- e11_firmware | Akuvox E11 allows direct SIP calls. No access control is enforced by the SIP servers, which could allow an attacker to contact any device within Akuvox to call any other device. | 2023-03-13 | 7.5 | CVE-2023-0348 MISC |
| akuvox -- e11_firmware | Akuvox E11 uses a hard-coded cryptographic key, which could allow an attacker to decrypt sensitive information. | 2023-03-13 | 7.5 | CVE-2023-0355 MISC |
| saysis -- starcities | Files or Directories Accessible to External Parties vulnerability in Saysis Starcities allows Collect Data from Common Resource Locations.This issue affects Starcities: through 1.3. | 2023-03-10 | 7.5 | CVE-2023-1246 MISC |
| vim -- vim | NULL Pointer Dereference in GitHub repository vim/vim prior to 9.0.1402. | 2023-03-11 | 7.5 | CVE-2023-1355 MISC CONFIRM |
| online_pizza_ordering_system_project -- online_pizza_ordering_system | A vulnerability has been found in SourceCodester Online Pizza Ordering System 1.0 and classified as critical. Affected by this vulnerability is an unknown functionality of the file category.php of the component GET Parameter Handler. The manipulation of the argument id leads to sql injection. The attack can be launched remotely. The exploit has been disclosed to the public and may be used. The associated identifier of this vulnerability is VDB-222871. | 2023-03-13 | 7.5 | CVE-2023-1364 MISC MISC MISC |
| online_pizza_ordering_system_project -- online_pizza_ordering_system | A vulnerability was found in SourceCodester Online Pizza Ordering System 1.0 and classified as critical. Affected by this issue is some unknown functionality of the file /admin/ajax.php. The manipulation of the argument username leads to sql injection. The attack may be launched remotely. The exploit has been disclosed to the public and may be used. The identifier of this vulnerability is VDB-222872. | 2023-03-13 | 7.5 | CVE-2023-1365 MISC MISC MISC |
| openharmony -- openharmony | The kernel subsystem hmdfs within OpenHarmony-v3.1.5 and prior versions has an arbitrary memory accessing vulnerability which network attackers can launch a remote attack to obtain kernel memory data of the target system. | 2023-03-10 | 7.5 | CVE-2023-22301 MISC |
| rocket.chat -- rocket.chat | An improper access control vulnerability exists prior to v6 that could allow an attacker to break the E2E encryption of a chat room by a user changing the group key of a chat room. | 2023-03-10 | 7.5 | CVE-2023-23911 MISC |
| microsoft -- windows_server_2012 | Microsoft PostScript and PCL6 Class Printer Driver Information Disclosure Vulnerability | 2023-03-14 | 7.5 | CVE-2023-24856 MISC |
| microsoft -- windows_server_2012 | Microsoft PostScript and PCL6 Class Printer Driver Information Disclosure Vulnerability | 2023-03-14 | 7.5 | CVE-2023-24857 MISC |
| microsoft -- windows_server_2012 | Microsoft PostScript and PCL6 Class Printer Driver Information Disclosure Vulnerability | 2023-03-14 | 7.5 | CVE-2023-24858 MISC |
| microsoft -- windows_server_2012 | Windows Internet Key Exchange (IKE) Extension Denial of Service Vulnerability | 2023-03-14 | 7.5 | CVE-2023-24859 MISC |
| dlink -- dir-820l_firmware | A stack overflow vulnerability in D-Link DIR820LA1_FW106B02 allows attackers to cause a denial of service via the reserveDHCP_HostName_1.1.1.0 parameter to lan.asp. | 2023-03-13 | 7.5 | CVE-2023-25283 MISC MISC |
| swig-templates_project -- swig-templates | Directory traversal vulnerability in swig-templates thru 2.0.4 and swig thru 1.4.2, allows attackers to read arbitrary files via the include or extends tags. | 2023-03-15 | 7.5 | CVE-2023-25345 MISC |
| apache -- log4j | ** UNSUPPORTED WHEN ASSIGNED ** When using the Chainsaw or SocketAppender components with Log4j 1.x on JRE less than 1.7, an attacker that manages to cause a logging entry involving a specially-crafted (ie, deeply nested) hashmap or hashtable (depending on which logging component is in use) to be processed could exhaust the available memory in the virtual machine and achieve Denial of Service when the object is deserialized. This issue affects Apache Log4j before 2. Affected users are recommended to update to Log4j 2.x. NOTE: This vulnerability only affects products that are no longer supported by the maintainer. | 2023-03-10 | 7.5 | CVE-2023-26464 MISC |
| tenda -- w15e_firmware | Tenda V15V1.0 was discovered to contain a buffer overflow vulnerability via the gotoUrl parameter in the formPortalAuth function. This vulnerability allows attackers to cause a Denial of Service (DoS) via a crafted request. | 2023-03-13 | 7.5 | CVE-2023-27062 MISC |
| tenda -- w15e_firmware | Tenda V15V1.0 V15.11.0.14(1521_3190_1058) was discovered to contain a buffer overflow vulnerability via the index parameter in the formDelDnsForward function. This vulnerability allows attackers to cause a Denial of Service (DoS) via a crafted request. | 2023-03-13 | 7.5 | CVE-2023-27064 MISC |
| tenda -- w15e_firmware | Tenda V15V1.0 V15.11.0.14(1521_3190_1058) was discovered to contain a buffer overflow vulnerability via the picName parameter in the formDelWewifiPi function. This vulnerability allows attackers to cause a Denial of Service (DoS) via a crafted request. | 2023-03-13 | 7.5 | CVE-2023-27065 MISC |
| jellyfin -- jellyfin | Jellyfin up to v10.7.7 was discovered to contain a Server-Side Request Forgery (SSRF) via the component /Repositories. This vulnerability allows attackers to access network resources and sensitive information via a crafted POST request. | 2023-03-10 | 7.5 | CVE-2023-27161 MISC MISC MISC |
| rack_project -- rack | A DoS vulnerability exists in Rack <v3.0.4.2, <v2.2.6.3, <v2.1.4.3 and <v2.0.9.3 within in the Multipart MIME parsing code in which could allow an attacker to craft requests that can be abuse to cause multipart parsing to take longer than expected. | 2023-03-10 | 7.5 | CVE-2023-27530 MISC |
| veeam -- backup_&_replication | Vulnerability in Veeam Backup & Replication component allows encrypted credentials stored in the configuration database to be obtained. This may lead to gaining access to the backup infrastructure hosts. | 2023-03-10 | 7.5 | CVE-2023-27532 MISC |
| jenkins -- jenkins | Jenkins 2.393 and earlier, LTS 2.375.3 and earlier uses the Apache Commons FileUpload library without specifying limits for the number of request parts introduced in version 1.5 for CVE-2023-24998 in hudson.util.MultipartFormDataParser, allowing attackers to trigger a denial of service. | 2023-03-10 | 7.5 | CVE-2023-27900 MISC |
| jenkins -- jenkins | Jenkins 2.393 and earlier, LTS 2.375.3 and earlier uses the Apache Commons FileUpload library without specifying limits for the number of request parts introduced in version 1.5 for CVE-2023-24998 in org.kohsuke.stapler.RequestImpl, allowing attackers to trigger a denial of service. | 2023-03-10 | 7.5 | CVE-2023-27901 MISC |
| ibexa -- digital_experience_platform | An issue was discovered in eZ Platform Ibexa Kernel before 1.3.26. The Company admin role gives excessive privileges. | 2023-03-12 | 7.2 | CVE-2022-48365 MISC MISC MISC MISC |
| bbraun -- battery-pack_sp_with_wifi_firmware | An improper neutralization of directives in dynamically evaluated code vulnerability in the WiFi Battery embedded web server in versions L90/U70 and L92/U92 can be used to gain administrative access to the WiFi communication module. An authenticated user, having access to both the medical device WiFi network (such as a biomedical engineering staff member) and the specific B.Braun Battery Pack SP with WiFi web server credentials, could get administrative (root) access on the infusion pump communication module. This could be used as a vector to start further attacks | 2023-03-13 | 7.2 | CVE-2023-0888 MISC MISC |
| 115cms -- 115cms | A vulnerability was found in Guizhou 115cms 4.2. It has been classified as problematic. Affected is an unknown function of the file /admin/content/index. The manipulation leads to unrestricted upload. It is possible to launch the attack remotely. The exploit has been disclosed to the public and may be used. VDB-222738 is the identifier assigned to this vulnerability. | 2023-03-10 | 7.2 | CVE-2023-1328 MISC MISC MISC |
| yoga_class_registration_system_project -- yoga_class_registration_system | A vulnerability was found in SourceCodester Yoga Class Registration System 1.0. It has been classified as critical. This affects the function query of the file admin/categories/manage_category.php. The manipulation of the argument id leads to sql injection. It is possible to initiate the attack remotely. The exploit has been disclosed to the public and may be used. The identifier VDB-222873 was assigned to this vulnerability. | 2023-03-13 | 7.2 | CVE-2023-1366 MISC MISC MISC |
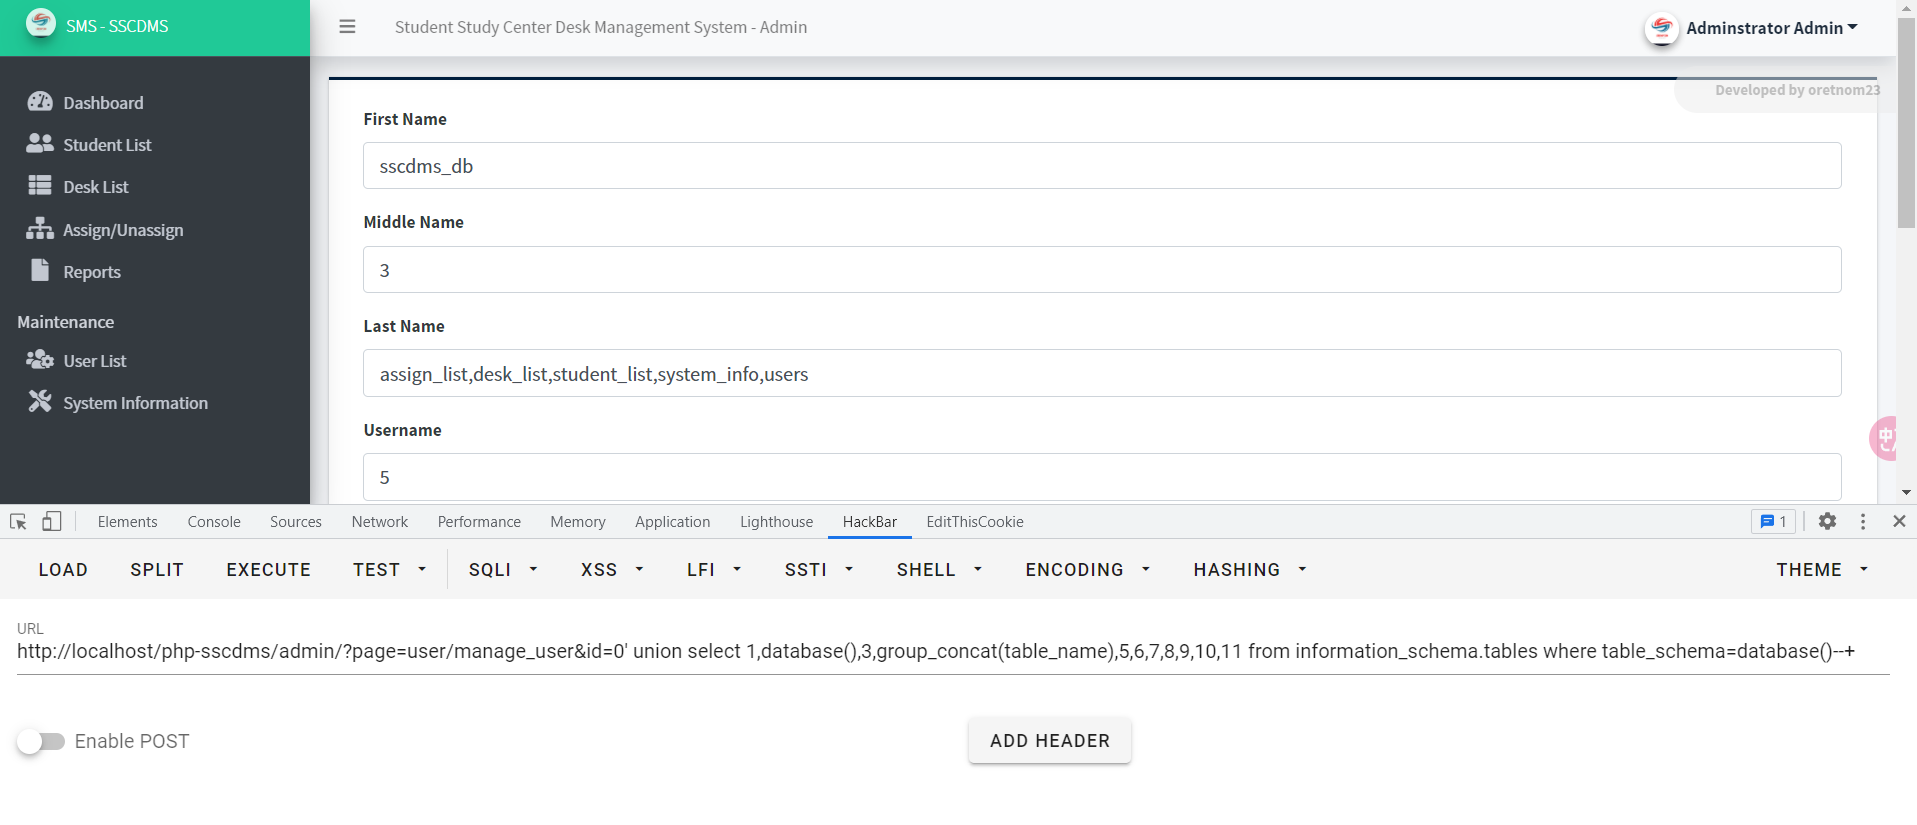
| student_study_center_desk_management_system_project -- student_study_center_desk_management_system | A vulnerability classified as critical was found in SourceCodester Student Study Center Desk Management System 1.0. Affected by this vulnerability is an unknown functionality of the file /admin/user/manage_user.php. The manipulation of the argument id leads to sql injection. The attack can be launched remotely. The exploit has been disclosed to the public and may be used. The associated identifier of this vulnerability is VDB-223111. | 2023-03-15 | 7.2 | CVE-2023-1407 MISC MISC MISC |
| microsoft -- windows_server | Windows DNS Server Remote Code Execution Vulnerability | 2023-03-14 | 7.2 | CVE-2023-23400 MISC |
| jizhicms -- jizhicms | An arbitrary file upload vulnerability in the \admin\c\CommonController.php component of Jizhicms v2.4.5 allows attackers to execute arbitrary code via a crafted phtml file. | 2023-03-15 | 7.2 | CVE-2023-27235 MISC |
| docker -- docker_desktop | Docker Desktop before 4.17.0 allows an unprivileged user to bypass Enhanced Container Isolation (ECI) restrictions by setting the Docker host to docker.raw.sock, or npipe:////.pipe/docker_engine_linux on Windows, via the -H (--host) CLI flag or the DOCKER_HOST environment variable and launch containers without the additional hardening features provided by ECI. This would not affect already running containers, nor containers launched through the usual approach (without Docker's raw socket). The affected functionality is available for Docker Business customers only and assumes an environment where users are not granted local root or Administrator privileges. This issue has been fixed in Docker Desktop 4.17.0. Affected Docker Desktop versions: from 4.13.0 before 4.17.0. | 2023-03-13 | 7.1 | CVE-2023-0629 MISC |
| microsoft -- multiple_products | Microsoft Excel Spoofing Vulnerability | 2023-03-14 | 7.1 | CVE-2023-23398 MISC |
| microsoft -- multiple_products | Windows Point-to-Point Protocol over Ethernet (PPPoE) Remote Code Execution Vulnerability | 2023-03-14 | 7.1 | CVE-2023-23407 MISC |
| microsoft -- multiple_products | Windows Point-to-Point Protocol over Ethernet (PPPoE) Remote Code Execution Vulnerability | 2023-03-14 | 7.1 | CVE-2023-23414 MISC |
| microsoft -- edge | Microsoft Edge (Chromium-based) Webview2 Spoofing Vulnerability | 2023-03-14 | 7.1 | CVE-2023-24892 MISC |
| qualcomm -- aqt1000_firmware | Memory corruption in Core due to time-of-check time-of-use race condition during dump collection in trust zone. | 2023-03-10 | 7 | CVE-2022-33257 MISC |
| microsoft -- multiple_products | Windows Point-to-Point Protocol over Ethernet (PPPoE) Elevation of Privilege Vulnerability | 2023-03-14 | 7 | CVE-2023-23385 MISC |
| microsoft -- multiple_products | Windows BrokerInfrastructure Service Elevation of Privilege Vulnerability | 2023-03-14 | 7 | CVE-2023-23393 MISC |
| microsoft -- multiple_products | Windows Graphics Component Elevation of Privilege Vulnerability | 2023-03-14 | 7 | CVE-2023-24861 MISC |
| jenkins -- jenkins | Jenkins 2.393 and earlier, LTS 2.375.3 and earlier creates a temporary file in the default temporary directory with the default permissions for newly created files when uploading a plugin for installation, potentially allowing attackers with access to the Jenkins controller file system to read and write the file before it is used, potentially resulting in arbitrary code execution. | 2023-03-10 | 7 | CVE-2023-27899 MISC |
| Primary Vendor -- Product | Description | Published | CVSS Score | Source & Patch Info |
|---|---|---|---|---|
| netgear -- rax30_firmware | NETGEAR Nighthawk WiFi6 Router prior to V1.0.10.94 contains a file sharing mechanism that allows users with access to this feature to access arbitrary files on the device. | 2023-03-10 | 6.8 | CVE-2023-27850 MISC |
| google -- android | In telephone service, there is a missing permission check. This could lead to local escalation of privilege with system execution privileges needed. | 2023-03-10 | 6.7 | CVE-2022-47461 MISC |
| google -- android | In telephone service, there is a missing permission check. This could lead to local escalation of privilege with system execution privileges needed. | 2023-03-10 | 6.7 | CVE-2022-47462 MISC |
| mcafee -- advanced_threat_defense | A command injection vulnerability in Trellix Intelligent Sandbox CLI for version 5.2 and earlier, allows a local user to inject and execute arbitrary operating system commands using specially crafted strings. This vulnerability is due to insufficient validation of arguments that are passed to specific CLI command. The vulnerability allows the attack | 2023-03-13 | 6.7 | CVE-2023-0978 MISC |
| trendmicro -- apex_one | An issue in the Trend Micro Apex One agent could allow an attacker who has previously acquired administrative rights via other means to bypass the protection by using a specifically crafted DLL during a specific update process. Please note: an attacker must first obtain administrative access on the target system via another method in order to exploit this. | 2023-03-10 | 6.7 | CVE-2023-25147 MISC |
| ibm -- robotic_process_automation_as_a_service | IBM Robotic Process Automation 21.0.0 - 21.0.7 and 23.0.0 is vulnerable to client-side validation bypass for credential pools. Invalid credential pools may be created as a result. IBM X-Force ID: 242951. | 2023-03-15 | 6.5 | CVE-2022-46773 MISC MISC |
| ibm -- manage_application | IBM Manage Application 8.8.0 and 8.9.0 in the IBM Maximo Application Suite is vulnerable to incorrect default permissions which could give access to a user to actions that they should not have access to. IBM X-Force ID: 242953. | 2023-03-15 | 6.5 | CVE-2022-46774 MISC MISC |
| wpgmaps -- wp_go_maps | Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal') vulnerability in WP Go Maps (formerly WP Google Maps) plugin <= 9.0.15 versions. | 2023-03-14 | 6.5 | CVE-2022-47595 MISC |
| akuvox -- e11_firmware | Akuvox E11 does not ensure that a file extension is associated with the file provided. This could allow an attacker to upload a file to the device by changing the extension of a malicious file to an accepted file type. | 2023-03-13 | 6.5 | CVE-2023-0350 MISC |
| oceanwp -- ocean_extra | The Ocean Extra WordPress plugin before 2.1.3 does not ensure that the template to be loaded via a shortcode is actually a template, allowing any authenticated users such as subscriber to retrieve the content of arbitrary posts, such as draft, private or even password protected ones. | 2023-03-13 | 6.5 | CVE-2023-0749 MISC |
| optinmonster -- optinmonster | The Popup Builder by OptinMonster WordPress plugin before 2.12.2 does not ensure that the campaign to be loaded via some shortcodes is actually a campaign, allowing any authenticated users such as subscriber to retrieve the content of arbitrary posts, like draft, private or even password protected ones. | 2023-03-13 | 6.5 | CVE-2023-0772 MISC |
| devolutions -- devolutions_server | Improper access control in the secure messages feature in Devolutions Server 2022.3.12 and below allows an authenticated attacker that possesses the message UUID to access the data it contains. | 2023-03-10 | 6.5 | CVE-2023-1201 MISC |
| devolutions -- remote_desktop_manager | Improper removal of sensitive data in the entry edit feature of Hub Business submodule in Devolutions Remote Desktop Manager PowerShell Module 2022.3.1.5 and earlier allows an authenticated user to access sensitive data on entries that were edited using the affected submodule. | 2023-03-10 | 6.5 | CVE-2023-1203 MISC |
| bumsys_project -- bumsys | SQL Injection in GitHub repository unilogies/bumsys prior to v2.0.2. | 2023-03-13 | 6.5 | CVE-2023-1361 CONFIRM MISC |
| ibm -- sterling_b2b_integrator | IBM Sterling B2B Integrator Standard Edition 6.0.0.0 through 6.0.3.7 and 6.1.0.0 through 6.1.2.1 could allow a privileged user to obtain sensitive information that could aid in further attacks against the system. IBM X-Force ID: 244364. | 2023-03-15 | 6.5 | CVE-2023-22876 MISC MISC |
| microsoft -- multiple_products | Microsoft Excel Denial of Service Vulnerability | 2023-03-14 | 6.5 | CVE-2023-23396 MISC |
| microsoft -- multiple_products | Windows Hyper-V Denial of Service Vulnerability | 2023-03-14 | 6.5 | CVE-2023-23411 MISC |
| libelfin_project -- libelfin | Libelfin v0.3 was discovered to contain an integer overflow in the load function at elf/mmap_loader.cc. This vulnerability allows attackers to cause a Denial of Service (DoS) via a crafted elf file. | 2023-03-14 | 6.5 | CVE-2023-24180 MISC |
| microsoft -- multiple_products | Microsoft PostScript and PCL6 Class Printer Driver Information Disclosure Vulnerability | 2023-03-14 | 6.5 | CVE-2023-24863 MISC |
| microsoft -- multiple_products | Microsoft PostScript and PCL6 Class Printer Driver Information Disclosure Vulnerability | 2023-03-14 | 6.5 | CVE-2023-24865 MISC |
| microsoft -- multiple_products | Microsoft PostScript and PCL6 Class Printer Driver Information Disclosure Vulnerability | 2023-03-14 | 6.5 | CVE-2023-24866 MISC |
| microsoft -- multiple_products | Microsoft PostScript and PCL6 Class Printer Driver Information Disclosure Vulnerability | 2023-03-14 | 6.5 | CVE-2023-24870 MISC |
| microsoft -- onedrive_for_ios | Microsoft OneDrive for iOS Security Feature Bypass Vulnerability | 2023-03-14 | 6.5 | CVE-2023-24890 MISC |
| microsoft -- multiple_products | Microsoft PostScript and PCL6 Class Printer Driver Information Disclosure Vulnerability | 2023-03-14 | 6.5 | CVE-2023-24906 MISC |
| microsoft -- multiple_products | Microsoft PostScript and PCL6 Class Printer Driver Information Disclosure Vulnerability | 2023-03-14 | 6.5 | CVE-2023-24911 MISC |
| microsoft -- dynamics_365 | Microsoft Dynamics 365 Information Disclosure Vulnerability | 2023-03-14 | 6.5 | CVE-2023-24922 MISC |
| dlink -- dir-820l_firmware | A heap overflow vulnerability in D-Link DIR820LA1_FW106B02 allows attackers to cause a denial of service via the config.log_to_syslog and log_opt_dropPackets parameters to mydlink_api.ccp. | 2023-03-15 | 6.5 | CVE-2023-25282 MISC MISC |
| sap -- netweaver_application_server_abap | SAP NetWeaver Application Server for ABAP and ABAP Platform - versions 700, 701, 702, 731, 740, 750, 751, 752, 753, 754, 755, 756, 757, 791, has multiple vulnerabilities in an unused class for error handling in which an attacker authenticated as a non-administrative user can craft a request with certain parameters which will consume the server's resources sufficiently to make it unavailable. There is no ability to view or modify any information. | 2023-03-14 | 6.5 | CVE-2023-25618 MISC MISC |
| ibm -- robotic_process_automation | IBM Robotic Process Automation 21.0.1 through 21.0.5 is vulnerable to insufficiently protecting credentials. Queue Provider credentials are not obfuscated while editing queue provider details. IBM X-Force ID: 247032. | 2023-03-15 | 6.5 | CVE-2023-25680 MISC MISC |
| online_food_ordering_system_project -- online_food_ordering_system | A Cross-Site Request Forgery (CSRF) in Online Food Ordering System v1.0 allows attackers to change user details and credentials via a crafted POST request. | 2023-03-14 | 6.5 | CVE-2023-27073 MISC |
| readtomyshoe_project -- readtomyshoe | ReadtoMyShoe, a web app that lets users upload articles and listen to them later, generates an error message containing sensitive information prior to commit 8533b01. If an error occurs when adding an article, the website shows the user an error message. If the error originates from the Google Cloud TTS request, then it will include the full URL of the request. The request URL contains the Google Cloud API key. This has been patched in commit 8533b01. Upgrading should be accompanied by deleting the current GCP API key and issuing a new one. There are no known workarounds. | 2023-03-13 | 6.5 | CVE-2023-27587 MISC MISC |
| microsoft -- malware_protection_engine | Microsoft Defender Elevation of Privilege Vulnerability | 2023-03-14 | 6.3 | CVE-2023-23389 MISC |
| a-forms_project -- a-forms | A vulnerability, which was classified as problematic, was found in MMDeveloper A Forms Plugin up to 1.4.2. This affects an unknown part of the file a-forms.php. The manipulation leads to cross site scripting. It is possible to initiate the attack remotely. Upgrading to version 1.4.3 is able to address this issue. The name of the patch is 3e693197bd69b7173cc16d8d2e0a7d501a2a0b06. It is recommended to upgrade the affected component. The identifier VDB-222609 was assigned to this vulnerability. | 2023-03-10 | 6.1 | CVE-2013-10020 MISC MISC MISC |
| wordpress -- debug_bar | A vulnerability was found in dd32 Debug Bar Plugin up to 0.8. It has been declared as problematic. Affected by this vulnerability is the function render of the file panels/class-debug-bar-queries.php. The manipulation leads to cross site scripting. The attack can be launched remotely. Upgrading to version 0.8.1 is able to address this issue. The name of the patch is 0842af8f8a556bc3e39b9ef758173b0a8a9ccbfc. It is recommended to upgrade the affected component. The associated identifier of this vulnerability is VDB-222739. | 2023-03-11 | 6.1 | CVE-2013-10021 MISC MISC MISC MISC |
| mobilevikings -- django_ajax_utilities | A vulnerability was found in Mobile Vikings Django AJAX Utilities up to 1.2.1 and classified as problematic. This issue affects the function Pagination of the file django_ajax/static/ajax-utilities/js/pagination.js of the component Backslash Handler. The manipulation of the argument url leads to cross site scripting. The attack may be initiated remotely. The name of the patch is 329eb1dd1580ca1f9d4f95bc69939833226515c9. It is recommended to apply a patch to fix this issue. The associated identifier of this vulnerability is VDB-222611. | 2023-03-10 | 6.1 | CVE-2017-20182 MISC MISC MISC |
| hcltech -- verse | HCL Verse is susceptible to a Cross Site Scripting (XSS) vulnerability. By tricking a user into clicking a crafted URL, a remote unauthenticated attacker could execute script in a victim's web browser to perform operations as the victim and/or steal the victim's cookies, session tokens, or other sensitive information. | 2023-03-10 | 6.1 | CVE-2021-27788 MISC |
| firmanet -- customer_relation_manager | Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Firmanet Software and Technology Customer Relation Manager allows XSS Targeting HTML Attributes.This issue affects Customer Relation Manager: before 2022.03.13. | 2023-03-14 | 6.1 | CVE-2021-4195 MISC |
| ibexa -- ez_platform_kernel | An issue was discovered in eZ Platform Ibexa Kernel before 1.3.1.1. An XSS attack can occur because JavaScript code can be uploaded in a .html or .js file. | 2023-03-12 | 6.1 | CVE-2021-46875 MISC MISC |
| firmanet -- technology_customer_relation_manager | Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Firmanet Software and Technology Customer Relation Manager allows Cross-Site Scripting (XSS).This issue affects Customer Relation Manager: before 2022.03.13. | 2023-03-14 | 6.1 | CVE-2022-23790 MISC |
| firmanet -- customer_relation_manager | Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Firmanet Software and Technology Customer Relation Manager allows Cross-Site Scripting (XSS).This issue affects Customer Relation Manager: before 2022.03.13. | 2023-03-14 | 6.1 | CVE-2022-23791 MISC |
| ibm -- app_connect_enterprise_certified_container | IBM App Connect Enterprise Certified Container 4.1, 4.2, 5.0, 5.1, 5.2, 6.0, 6.1, 6.2, and 7.0 is vulnerable to cross-site scripting. This vulnerability allows users to embed arbitrary JavaScript code in the Web UI thus altering the intended functionality potentially leading to credentials disclosure within a trusted session. IBM X-Force ID: 239963. | 2023-03-15 | 6.1 | CVE-2022-43874 MISC MISC |
| siri-informatica -- wi400 | A cross-site scripting (XSS) vulnerability in the check_login function of SIPE s.r.l WI400 between version 8 and 11 included allows attackers to execute arbitrary web scripts or HTML via a crafted payload injected into the f parameter. | 2023-03-10 | 6.1 | CVE-2022-48111 MISC MISC MISC MISC MISC |
| sap -- netweaver | Due to insufficient encoding of user input, SAP NetWeaver - versions 700, 701, 702, 731, 740, 750, allows an unauthenticated attacker to inject code that may expose sensitive data like user ID and password, which could lead to reflected Cross-Site scripting. These endpoints are normally exposed over the network and successful exploitation can partially impact confidentiality of the application. | 2023-03-14 | 6.1 | CVE-2023-0021 MISC MISC |
| talentyazilim -- unis | Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Talent Software UNIS allows Reflected XSS.This issue affects UNIS: before 28376. | 2023-03-15 | 6.1 | CVE-2023-0322 MISC |
| gigamon -- gigavue-os | The help page in GigaVUE-FM, when using GigaVUE-OS software version 5.0 202, does not require an authenticated user. An attacker could enforce a user into inserting malicious JavaScript code into the URI, that could lead to a Reflected Cross site Scripting. | 2023-03-10 | 6.1 | CVE-2023-0746 CONFIRM |
| enhancesoft -- osticket | Cross-site Scripting (XSS) - Stored in GitHub repository osticket/osticket prior to v1.16.6. | 2023-03-10 | 6.1 | CVE-2023-1320 CONFIRM MISC |
| hsycms -- hsycms | A vulnerability, which was classified as problematic, has been found in Hsycms 3.1. Affected by this issue is some unknown functionality of the file controller\cate.php of the component Add Category Module. The manipulation of the argument title leads to cross site scripting. The attack may be launched remotely. The exploit has been disclosed to the public and may be used. VDB-222842 is the identifier assigned to this vulnerability. | 2023-03-11 | 6.1 | CVE-2023-1349 MISC MISC MISC |
| design_and_implementation_of_covid-19_directory_on_vaccination_system_project -- design_and_implementation_of_covid-19_directory_on_vaccination_system | A vulnerability, which was classified as problematic, was found in SourceCodester Design and Implementation of Covid-19 Directory on Vaccination System 1.0. Affected is an unknown function of the file verification.php. The manipulation of the argument txtvaccinationID leads to cross site scripting. It is possible to launch the attack remotely. The exploit has been disclosed to the public and may be used. The identifier of this vulnerability is VDB-222852. | 2023-03-11 | 6.1 | CVE-2023-1353 MISC MISC MISC |
| design_and_implementation_of_covid-19_directory_on_vaccination_system_project -- design_and_implementation_of_covid-19_directory_on_vaccination_system | A vulnerability has been found in SourceCodester Design and Implementation of Covid-19 Directory on Vaccination System 1.0 and classified as problematic. Affected by this vulnerability is an unknown functionality of the file register.php. The manipulation of the argument txtfullname/txtage/txtaddress/txtphone leads to cross site scripting. The attack can be launched remotely. The exploit has been disclosed to the public and may be used. The identifier VDB-222853 was assigned to this vulnerability. | 2023-03-11 | 6.1 | CVE-2023-1354 MISC MISC MISC |
| bumsys_project -- bumsys | Improper Restriction of Rendered UI Layers or Frames in GitHub repository unilogies/bumsys prior to v2.0.2. | 2023-03-13 | 6.1 | CVE-2023-1362 MISC CONFIRM |
| webhostings -- wh_testimonials | The WH Testimonials plugin for WordPress is vulnerable to Stored Cross-Site Scripting via several parameters such as wh_homepage, wh_text_short, wh_text_full and in versions up to, and including, 3.0.0 due to insufficient input sanitization and output escaping. This makes it possible for unauthenticated attackers to inject arbitrary web scripts in pages that will execute whenever a user accesses an injected page. | 2023-03-13 | 6.1 | CVE-2023-1372 MISC MISC MISC |
| yoga_class_registration_system_project -- yoga_class_registration_system | A vulnerability was found in SourceCodester Yoga Class Registration System 1.0. It has been declared as problematic. This vulnerability affects the function query of the file admin/user/list.php. The manipulation of the argument name leads to cross site scripting. The attack can be initiated remotely. The exploit has been disclosed to the public and may be used. VDB-222982 is the identifier assigned to this vulnerability. | 2023-03-14 | 6.1 | CVE-2023-1395 MISC MISC MISC |
| online_tours_&travels_management_system_project -- online_tours&_travels_management_system | A vulnerability was found in SourceCodester Online Tours & Travels Management System 1.0. It has been rated as problematic. This issue affects some unknown processing of the file admin/traveller_details.php. The manipulation of the argument address leads to cross site scripting. The attack may be initiated remotely. The exploit has been disclosed to the public and may be used. The associated identifier of this vulnerability is VDB-222983. | 2023-03-14 | 6.1 | CVE-2023-1396 MISC MISC MISC |
| online_student_management_system_project -- online_student_management_system | A vulnerability classified as problematic has been found in SourceCodester Online Student Management System 1.0. Affected is an unknown function of the file profile.php. The manipulation of the argument adminname leads to cross site scripting. It is possible to launch the attack remotely. The exploit has been disclosed to the public and may be used. The identifier of this vulnerability is VDB-222984. | 2023-03-14 | 6.1 | CVE-2023-1397 MISC MISC MISC |
| opennetworking -- onos | A cross-site scripting (XSS) vulnerability in Open Networking Foundation ONOS from version v1.9.0 to v2.7.0 allows attackers to execute arbitrary web scripts or HTML via a crafted payload injected into the url parameter of the API documentation dashboard. | 2023-03-14 | 6.1 | CVE-2023-24279 MISC MISC MISC |
| ibm -- spectrum_symphony | IBM Spectrum Symphony 7.3 is vulnerable to HTTP header injection, caused by improper validation of input by the HOST headers. This could allow an attacker to conduct various attacks against the vulnerable system, including cross-site scripting, cache poisoning or session hijacking. IBM X-Force ID: 247030. | 2023-03-10 | 6.1 | CVE-2023-24975 MISC MISC |
| sap -- content_server | SAP Content Server - version 7.53, does not sufficiently encode user-controlled inputs, resulting in Cross-Site Scripting (XSS) vulnerability. After successful exploitation, an attacker can read and modify some sensitive information but cannot delete the data. | 2023-03-14 | 6.1 | CVE-2023-26457 MISC MISC |
| my-blog_project -- my-blog | Cross Site Scripting vulnerability found in My-Blog allows attackers to cause a denial of service via the Post function. | 2023-03-13 | 6.1 | CVE-2023-27093 MISC |
| icepay -- rest_api | A vulnerability was found in ICEPAY REST-API-NET 0.9. It has been declared as problematic. Affected by this vulnerability is the function RestClient of the file Classes/RestClient.cs of the component Checksum Validation. The manipulation leads to improper validation of integrity check value. The attack can be launched remotely. Upgrading to version 1.0 is able to address this issue. The name of the patch is 61f6b8758e5c971abff5f901cfa9f231052b775f. It is recommended to upgrade the affected component. The associated identifier of this vulnerability is VDB-222847. | 2023-03-12 | 5.9 | CVE-2016-15028 MISC MISC MISC MISC |
| qualcomm -- apq8009_firmware | Information Disclosure in Graphics during GPU context switch. | 2023-03-10 | 5.5 | CVE-2022-22075 MISC |
| hpe -- superdome_flex_280_server_firmware | A potential security vulnerability has been identified in HPE Superdome Flex and Superdome Flex 280 servers. The vulnerability could be locally exploited to allow disclosure of information. HPE has made the following software to resolve the vulnerability in HPE Superdome Flex Servers v3.65.8 and Superdome Flex 280 Servers v1.45.8. | 2023-03-10 | 5.5 | CVE-2022-37939 MISC |
| google -- android | In wcn service, there is a possible missing params check. This could lead to local denial of service in wcn service. | 2023-03-10 | 5.5 | CVE-2022-47453 MISC |
| google -- android | In wlan driver, there is a possible missing params check. This could lead to local denial of service in wlan services. | 2023-03-10 | 5.5 | CVE-2022-47454 MISC |
| google -- android | In wlan driver, there is a possible missing params check. This could lead to local denial of service in wlan services. | 2023-03-10 | 5.5 | CVE-2022-47455 MISC |
| google -- android | In wlan driver, there is a possible missing params check. This could lead to local denial of service in wlan services. | 2023-03-10 | 5.5 | CVE-2022-47456 MISC |
| google -- android | In wlan driver, there is a possible missing params check. This could lead to local denial of service in wlan services. | 2023-03-10 | 5.5 | CVE-2022-47457 MISC |
| google -- android | In wlan driver, there is a possible missing params check. This could lead to local denial of service in wlan services. | 2023-03-10 | 5.5 | CVE-2022-47458 MISC |
| google -- android | In wlan driver, there is a possible missing params check. This could lead to local denial of service in wlan services. | 2023-03-10 | 5.5 | CVE-2022-47459 MISC |
| google -- android | In gpu device, there is a memory corruption due to a use after free. This could lead to local denial of service in kernel. | 2023-03-10 | 5.5 | CVE-2022-47460 MISC |
| google -- android | In telephony service, there is a missing permission check. This could lead to local information disclosure with no additional execution privileges needed. | 2023-03-10 | 5.5 | CVE-2022-47471 MISC |
| google -- android | In telephony service, there is a missing permission check. This could lead to local information disclosure with no additional execution privileges needed. | 2023-03-10 | 5.5 | CVE-2022-47472 MISC |
| google -- android | In telephony service, there is a missing permission check. This could lead to local information disclosure with no additional execution privileges needed. | 2023-03-10 | 5.5 | CVE-2022-47473 MISC |
| google -- android | In telephony service, there is a missing permission check. This could lead to local information disclosure with no additional execution privileges needed. | 2023-03-10 | 5.5 | CVE-2022-47474 MISC |
| google -- android | In telephony service, there is a missing permission check. This could lead to local information disclosure with no additional execution privileges needed. | 2023-03-10 | 5.5 | CVE-2022-47475 MISC |
| google -- android | In telephony service, there is a missing permission check. This could lead to local information disclosure with no additional execution privileges needed. | 2023-03-10 | 5.5 | CVE-2022-47476 MISC |
| google -- android | In telephony service, there is a missing permission check. This could lead to local information disclosure with no additional execution privileges needed. | 2023-03-10 | 5.5 | CVE-2022-47477 MISC |
| google -- android | In telephony service, there is a missing permission check. This could lead to local information disclosure with no additional execution privileges needed. | 2023-03-10 | 5.5 | CVE-2022-47478 MISC |
| google -- android | In telephony service, there is a missing permission check. This could lead to local information disclosure with no additional execution privileges needed. | 2023-03-10 | 5.5 | CVE-2022-47479 MISC |
| google -- android | In telephony service, there is a missing permission check. This could lead to local denial of service in telephone service with no additional execution privileges needed. | 2023-03-10 | 5.5 | CVE-2022-47480 MISC |
| google -- android | In telephony service, there is a missing permission check. This could lead to local denial of service in telephone service with no additional execution privileges needed. | 2023-03-10 | 5.5 | CVE-2022-47481 MISC |
| google -- android | In telephony service, there is a missing permission check. This could lead to local denial of service in telephone service with no additional execution privileges needed. | 2023-03-10 | 5.5 | CVE-2022-47482 MISC |
| google -- android | In telephony service, there is a missing permission check. This could lead to local denial of service in telephone service with no additional execution privileges needed. | 2023-03-10 | 5.5 | CVE-2022-47483 MISC |
| google -- android | In telephony service, there is a missing permission check. This could lead to local denial of service in telephone service with no additional execution privileges needed. | 2023-03-10 | 5.5 | CVE-2022-47484 MISC |
| openharmony -- openharmony | The ArKUI framework subsystem within OpenHarmony-v3.1.5 and prior versions, OpenHarmony-v3.0.7 and prior versions has an Improper Input Validation vulnerability which local attackers can exploit this vulnerability to send malicious data, causing the current application to crash. | 2023-03-10 | 5.5 | CVE-2023-0083 MISC |
| tgsoft -- viragtlt.sys | A vulnerability was found in TG Soft Vir.IT eXplorer 9.4.86.0. It has been rated as problematic. This issue affects some unknown processing in the library VIRAGTLT.sys of the component IoControlCode Handler. The manipulation leads to denial of service. The attack needs to be approached locally. The exploit has been disclosed to the public and may be used. Upgrading to version 9.5 is able to address this issue. It is recommended to upgrade the affected component. The associated identifier of this vulnerability is VDB-222875. | 2023-03-13 | 5.5 | CVE-2023-1369 MISC MISC MISC MISC MISC |
| microsoft -- office_for_android | Office for Android Spoofing Vulnerability | 2023-03-14 | 5.5 | CVE-2023-23391 MISC |
| microsoft -- multiple_products | Client Server Run-Time Subsystem (CSRSS) Information Disclosure Vulnerability | 2023-03-14 | 5.5 | CVE-2023-23394 MISC |
| microsoft -- multiple_products | Client Server Run-Time Subsystem (CSRSS) Information Disclosure Vulnerability | 2023-03-14 | 5.5 | CVE-2023-23409 MISC |
| openharmony -- openharmony | Communication Wi-Fi subsystem within OpenHarmony-v3.1.4 and prior versions, OpenHarmony-v3.0.7 and prior versions has a null pointer reference vulnerability which local attackers can exploit this vulnerability to cause the current application to crash. | 2023-03-10 | 5.5 | CVE-2023-24465 MISC |
| microsoft -- multiple_products | Windows Secure Channel Denial of Service Vulnerability | 2023-03-14 | 5.5 | CVE-2023-24862 MISC |
| microsoft -- onedrive_for_android | Microsoft OneDrive for Android Information Disclosure Vulnerability | 2023-03-14 | 5.5 | CVE-2023-24882 MISC |
| microsoft -- onedrive_for_android | Microsoft OneDrive for Android Information Disclosure Vulnerability | 2023-03-14 | 5.5 | CVE-2023-24923 MISC |
| openharmony -- openharmony | The bundle management subsystem within OpenHarmony-v3.1.4 and prior versions has a null pointer reference vulnerability which local attackers can exploit this vulnerability to cause a DoS attack to the system when installing a malicious HAP package. | 2023-03-10 | 5.5 | CVE-2023-25947 MISC |
| radare -- radare2 | radare2 v5.8.3 was discovered to contain a segmentation fault via the component wasm_dis at p/wasm/wasm.c. | 2023-03-10 | 5.5 | CVE-2023-27114 MISC MISC |
| webassembly -- webassembly | WebAssembly v1.0.29 was discovered to contain a segmentation fault via the component wabt::cat_compute_size. | 2023-03-10 | 5.5 | CVE-2023-27115 MISC MISC |
| webassembly -- webassembly | WebAssembly v1.0.29 discovered to contain an abort in CWriter::MangleType. | 2023-03-10 | 5.5 | CVE-2023-27116 MISC |
| webassembly -- webassembly | WebAssembly v1.0.29 was discovered to contain a segmentation fault via the component wabt::Decompiler::WrapChild. | 2023-03-10 | 5.5 | CVE-2023-27119 MISC |
| connekthq -- ajax_load_more | The WordPress Infinite Scroll WordPress plugin before 5.6.0.3 does not validate and escape some of its shortcode attributes before outputting them back in a page/post where the shortcode is embed, which could allow users with the contributor role and above to perform Stored Cross-Site Scripting attacks. | 2023-03-13 | 5.4 | CVE-2022-4466 MISC |
| pushlabs -- video_background | The Video Background WordPress plugin before 2.7.5 does not validate and escape some of its shortcode attributes before outputting them back in a page/post where the shortcode is embed, which could allow users with the contributor role and above to perform Stored Cross-Site Scripting attacks | 2023-03-13 | 5.4 | CVE-2022-4652 MISC |
| themelocation -- widgets_for_woocommerce_products_on_elementor | The Widgets for WooCommerce Products on Elementor WordPress plugin before 1.0.8 does not validate and escape some of its shortcode attributes before outputting them back in a page/post where the shortcode is embed, which could allow users with the contributor role and above to perform Stored Cross-Site Scripting attacks | 2023-03-13 | 5.4 | CVE-2022-4661 MISC |
| codeermeneer -- companion_sitemap_generator | The Companion Sitemap Generator WordPress plugin through 4.5.1.1 does not validate and escape some of its shortcode attributes before outputting them back in a page/post where the shortcode is embed, which could allow users with the contributor role and above to perform Stored Cross-Site Scripting attacks. | 2023-03-13 | 5.4 | CVE-2023-0066 MISC |
| client_logo_carousel_project -- client_logo_carousel | The Client Logo Carousel WordPress plugin through 3.0.0 does not validate and escape some of its shortcode attributes before outputting them back in a page/post where the shortcode is embed, which could allow users with the contributor role and above to perform Stored Cross-Site Scripting attacks. | 2023-03-13 | 5.4 | CVE-2023-0073 MISC |
| saas.group -- juicer | The Juicer WordPress plugin before 1.11 does not validate and escape some of its shortcode attributes before outputting them back in a page/post where the shortcode is embed, which could allow users with the contributor role and above to perform Stored Cross-Site Scripting attacks | 2023-03-13 | 5.4 | CVE-2023-0172 MISC |
| wpmanageninja -- fluentsmtp | The FluentSMTP WordPress plugin before 2.2.3 does not sanitize or escape email content, making it vulnerable to stored cross-site scripting attacks (XSS) when an administrator views the email logs. This exploit requires other plugins to enable users to send emails with unfiltered HTML. | 2023-03-13 | 5.4 | CVE-2023-0219 MISC |
| campaign_url_builder_project -- campaign_url_builder | The Campaign URL Builder WordPress plugin before 1.8.2 does not validate and escape some of its shortcode attributes before outputting them back in a page/post where the shortcode is embed, which could allow users with the contributor role and above to perform Stored Cross-Site Scripting attacks | 2023-03-13 | 5.4 | CVE-2023-0538 MISC |
| enhancesoft -- osticket | Cross-site Scripting (XSS) - Reflected in GitHub repository osticket/osticket prior to v1.16.6. | 2023-03-10 | 5.4 | CVE-2023-1315 MISC CONFIRM |
| enhancesoft -- osticket | Cross-site Scripting (XSS) - Stored in GitHub repository osticket/osticket prior to v1.16.6. | 2023-03-10 | 5.4 | CVE-2023-1316 CONFIRM MISC |
| enhancesoft -- osticket | Cross-site Scripting (XSS) - Reflected in GitHub repository osticket/osticket prior to v1.16.6. | 2023-03-10 | 5.4 | CVE-2023-1317 CONFIRM MISC |
| enhancesoft -- osticket | Cross-site Scripting (XSS) - Generic in GitHub repository osticket/osticket prior to v1.16.6. | 2023-03-10 | 5.4 | CVE-2023-1318 MISC CONFIRM |
| computer_parts_sales_and_inventory_system_project -- computer_parts_sales_and_inventory_system | A vulnerability, which was classified as problematic, was found in SourceCodester Computer Parts Sales and Inventory System 1.0. Affected is an unknown function of the component Add User Account. The manipulation of the argument username leads to cross site scripting. It is possible to launch the attack remotely. The exploit has been disclosed to the public and may be used. VDB-222870 is the identifier assigned to this vulnerability. | 2023-03-13 | 5.4 | CVE-2023-1363 MISC MISC MISC |
| avantfax -- avantfax | A Stored Cross-Site Scripting (XSS) vulnerability exists in AvantFAX 3.3.7. An authenticated low privilege user can inject arbitrary Javascript into their e-mail address which is executed when an administrator logs into AvantFAX to view the admin dashboard. This may result in stealing an administrator's session cookie and hijacking their session. | 2023-03-10 | 5.4 | CVE-2023-23326 MISC MISC |
| microsoft -- dynamics_365 | Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability | 2023-03-14 | 5.4 | CVE-2023-24879 MISC |
| microsoft -- multiple_products | Windows SmartScreen Security Feature Bypass Vulnerability | 2023-03-14 | 5.4 | CVE-2023-24880 MISC |
| microsoft -- dynamics_365 | Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability | 2023-03-14 | 5.4 | CVE-2023-24891 MISC |
| microsoft -- dynamics_365 | Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability | 2023-03-14 | 5.4 | CVE-2023-24919 MISC |
| microsoft -- dynamics_365 | Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability | 2023-03-14 | 5.4 | CVE-2023-24920 MISC |
| microsoft -- dynamics_365 | Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability | 2023-03-14 | 5.4 | CVE-2023-24921 MISC |
| totaljs -- openplatform | A stored cross-site scripting (XSS) vulnerability in TotalJS OpenPlatform commit b80b09d allows attackers to execute arbitrary web scripts or HTML via a crafted payload injected into the account name field. | 2023-03-14 | 5.4 | CVE-2023-27069 MISC MISC |
| totaljs -- openplatform | A stored cross-site scripting (XSS) vulnerability in TotalJS OpenPlatform commit b80b09d allows attackers to execute arbitrary web scripts or HTML via a crafted payload injected into the platform name field. | 2023-03-14 | 5.4 | CVE-2023-27070 MISC MISC |
| jenkins -- jenkins | Jenkins 2.270 through 2.393 (both inclusive), LTS 2.277.1 through 2.375.3 (both inclusive) does not escape the Jenkins version a plugin depends on when rendering the error message stating its incompatibility with the current version of Jenkins, resulting in a stored cross-site scripting (XSS) vulnerability exploitable by attackers able to provide plugins to the configured update sites and have this message shown by Jenkins instances. | 2023-03-10 | 5.4 | CVE-2023-27898 MISC |
| jenkins -- update-center2 | Jenkins update-center2 3.13 and 3.14 renders the required Jenkins core version on plugin download index pages without sanitization, resulting in a stored cross-site scripting (XSS) vulnerability exploitable by attackers able to provide a plugin for hosting. | 2023-03-10 | 5.4 | CVE-2023-27905 MISC |
| ibexa -- ez_platform_kernel | An issue was discovered in eZ Publish Ibexa Kernel before 7.5.15.1. The /user/sessions endpoint can be abused to determine account existence. | 2023-03-12 | 5.3 | CVE-2021-46876 MISC MISC |
| akuvox -- e11_firmware | The Akuvox E11 Media Access Control (MAC) address, a primary identifier, combined with the Akuvox E11 IP address, could allow an attacker to identify the device on the Akuvox cloud. | 2023-03-13 | 5.3 | CVE-2023-0347 MISC |
| hashicorp -- nomad | HashiCorp Nomad and Nomad Enterprise 1.4.0 up to 1.5.0 did not correctly enforce deny policies applied to a workload’s variables. Fixed in 1.4.6 and 1.5.1. | 2023-03-14 | 5.3 | CVE-2023-1296 MISC |
| sap -- netweaver_application_server_java | SAP NetWeaver Application Server Java for Classload Service - version 7.50, does not perform any authentication checks for functionalities that require user identity, resulting in escalation of privileges. This failure has a low impact on confidentiality of the data such that an unassigned user can read non-sensitive server data. | 2023-03-14 | 5.3 | CVE-2023-24526 MISC MISC |
| apache -- airflow | Generation of Error Message Containing Sensitive Information vulnerability in Apache Software Foundation Apache Airflow.This issue affects Apache Airflow: before 2.5.2. | 2023-03-15 | 5.3 | CVE-2023-25695 MISC MISC |
| roxy-wi -- roxy-wi | Roxy-WI is a Web interface for managing Haproxy, Nginx, Apache, and Keepalived servers. Versions prior to 6.3.5.0 have a limited path traversal vulnerability. An SSH key can be saved into an unintended location, for example the /tmp folder using a payload ../../../../../tmp/test111_dev. This issue has been fixed in version 6.3.5.0. |
2023-03-15 | 5.3 | CVE-2023-25804 MISC |
| jenkins -- jenkins | Jenkins 2.393 and earlier, LTS 2.375.3 and earlier prints an error stack trace on agent-related pages when agent connections are broken, potentially revealing information about Jenkins configuration that is otherwise inaccessible to attackers. | 2023-03-10 | 5.3 | CVE-2023-27904 MISC |
| employee_payslip_generator_system_project -- employee_payslip_generator_system | A vulnerability was found in SourceCodester Employee Payslip Generator with Sending Mail 1.2.0 and classified as critical. This issue affects some unknown processing of the file classes/Users.php?f=save of the component New User Creation. The manipulation of the argument username leads to sql injection. The attack may be initiated remotely. The exploit has been disclosed to the public and may be used. The associated identifier of this vulnerability is VDB-222863. | 2023-03-12 | 4.9 | CVE-2023-1360 MISC MISC MISC |
| avantfax -- avantfax | An Information Disclosure vulnerability exists in AvantFAX 3.3.7. Backups of the AvantFAX sent/received faxes, and database backups are stored using the current date as the filename and hosted on the web server without access controls. | 2023-03-10 | 4.9 | CVE-2023-23327 MISC MISC |
| sap -- abap_platform | Due to insufficient input sanitization, SAP ABAP - versions 751, 753, 753, 754, 756, 757, 791, allows an authenticated high privileged user to alter the current session of the user by injecting the malicious database queries over the network and gain access to the unintended data. This may lead to a high impact on the confidentiality and no impact on the availability and integrity of the application. | 2023-03-14 | 4.9 | CVE-2023-25615 MISC MISC |
| flarum -- flarum | flarum is a forum software package for building communities. In versions prior to 1.7.0 an admin account which has already been compromised by an attacker may use a vulnerability in the LESS parser which can be exploited to read sensitive files on the server through the use of path traversal techniques. An attacker can achieve this by providing an absolute path to a sensitive file in the custom LESS setting, which the LESS parser will then read. For example, an attacker could use the following code to read the contents of the /etc/passwd file on a linux machine. The scope of what files are vulnerable will depend on the permissions given to the running flarum process. The vulnerability has been addressed in version 1.7. Users should upgrade to this version to mitigate the vulnerability. Users unable to upgrade may mitigate the vulnerability by ensuring that their admin accounts are secured with strong passwords and follow other best practices for account security. Additionally, users can limit the exposure of sensitive files on the server by implementing appropriate file permissions and access controls at the operating system level. |
2023-03-10 | 4.9 | CVE-2023-27577 MISC MISC |
| jetbackup -- jetbackup | Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in JetBackup JetBackup – WP Backup, Migrate & Restore plugin <= 1.6.9.0 versions. | 2023-03-15 | 4.8 | CVE-2022-34148 MISC |
| afsanalytics -- afs_analytics | Stored Cross-site Scripting (XSS) vulnerability in AFS Analytics plugin <= 4.18 versions. | 2023-03-15 | 4.8 | CVE-2022-37402 MISC |
| ip_vault_-wp_firewall_project -- ip_vault-_wp_firewall | Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Paul C. Schroeder IP Vault – WP Firewall plugin <= 1.1 versions. | 2023-03-14 | 4.8 | CVE-2022-47171 MISC |
| kibokolabs -- namaste!_lms | The Namaste! LMS WordPress plugin before 2.6 does not sanitize and escape some of its settings, which could allow high-privilege users such as admin to perform Stored Cross-Site Scripting attacks even when the unfiltered_html capability is disallowed (for example in multisite setup). | 2023-03-13 | 4.8 | CVE-2023-0844 MISC |
| pimcore -- pimcore | Cross-site Scripting (XSS) - Reflected in GitHub repository pimcore/pimcore prior to 10.5.19. | 2023-03-10 | 4.8 | CVE-2023-1312 CONFIRM MISC |
| enhancesoft -- osticket | Cross-site Scripting (XSS) - Stored in GitHub repository osticket/osticket prior to v1.16.6. | 2023-03-10 | 4.8 | CVE-2023-1319 MISC CONFIRM |
| gadget_works_online_ordering_system_project -- gadget_works_online_ordering_system | A vulnerability has been found in SourceCodester Gadget Works Online Ordering System 1.0 and classified as problematic. This vulnerability affects unknown code of the file /philosophy/admin/user/controller.php?action=add of the component Add New User. The manipulation of the argument U_NAME leads to cross site scripting. The attack can be initiated remotely. The exploit has been disclosed to the public and may be used. VDB-222862 is the identifier assigned to this vulnerability. | 2023-03-12 | 4.8 | CVE-2023-1359 MISC MISC MISC |
| solidres -- solidres | The Solidres plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the 'currency_name' parameter in versions up to, and including, 0.9.4 due to insufficient input sanitization and output escaping. This makes it possible for authenticated attackers with administrator privileges to inject arbitrary web scripts in pages that will execute whenever a user accesses an injected page. | 2023-03-13 | 4.8 | CVE-2023-1374 MISC MISC MISC |
| s-mall-ssm_project -- s-mall-ssm | Cross site scripting (XSS) vulnerability in xenv S-mall-ssm thru commit 3d9e77f7d80289a30f67aaba1ae73e375d33ef71 on Feb 17, 2020, allows local attackers to execute arbitrary code via the evaluate button. | 2023-03-15 | 4.8 | CVE-2023-26912 MISC |
| halo -- halo | An arbitrary file upload vulnerability in Halo up to v1.6.1 allows attackers to execute arbitrary code via a crafted .md file. | 2023-03-10 | 4.8 | CVE-2023-27164 MISC MISC MISC |
| microsoft -- azure_hdinsights | Azure Apache Ambari Spoofing Vulnerability | 2023-03-14 | 4.5 | CVE-2023-23408 MISC |
| nvidia -- cuda_toolkit | NVIDIA CUDA Toolkit SDK contains a vulnerability in cuobjdump, where a local user running the tool against a malicious binary may cause an out-of-bounds read, which may result in a limited denial of service and limited information disclosure. | 2023-03-10 | 4.4 | CVE-2023-0193 MISC |
| jenkins -- jenkins | Jenkins 2.393 and earlier, LTS 2.375.3 and earlier creates a temporary file in the default temporary directory with the default permissions for newly created files when uploading a file parameter through the CLI, potentially allowing attackers with access to the Jenkins controller file system to read and write the file before it is used. | 2023-03-10 | 4.4 | CVE-2023-27903 MISC |
| rapidload -- power-up_for_autoptimize | The RapidLoad Power-Up for Autoptimize plugin for WordPress is vulnerable to unauthorized loss of data due to a missing capability check on the clear_page_cache function in versions up to, and including, 1.7.1. This makes it possible for authenticated attackers with subscriber-level access to delete the plugin's cache. | 2023-03-10 | 4.3 | CVE-2023-1333 MISC MISC |
| rapidload -- power-up_for_autoptimize | The RapidLoad Power-Up for Autoptimize plugin for WordPress is vulnerable to unauthorized cache modification due to a missing capability check on the queue_posts function in versions up to, and including, 1.7.1. This makes it possible for authenticated attackers with subscriber-level access to modify the plugin's cache. | 2023-03-10 | 4.3 | CVE-2023-1334 MISC MISC |
| rapidload -- power-up_for_autoptimize | The RapidLoad Power-Up for Autoptimize plugin for WordPress is vulnerable to unauthorized plugin settings update due to a missing capability check on the ucss_connect function in versions up to, and including, 1.7.1. This makes it possible for authenticated attackers with subscriber-level access to connect a new license key to the site. | 2023-03-10 | 4.3 | CVE-2023-1335 MISC MISC |
| rapidload -- power-up_for_autoptimize | The RapidLoad Power-Up for Autoptimize plugin for WordPress is vulnerable to unauthorized settings update due to a missing capability check on the ajax_deactivate function in versions up to, and including, 1.7.1. This makes it possible for authenticated attackers with subscriber-level access to disable caching. | 2023-03-10 | 4.3 | CVE-2023-1336 MISC MISC |
| rapidload -- power-up_for_autoptimize | The RapidLoad Power-Up for Autoptimize plugin for WordPress is vulnerable to unauthorized data loss due to a missing capability check on the clear_uucss_logs function in versions up to, and including, 1.7.1. This makes it possible for authenticated attackers with subscriber-level access to delete plugin log files. | 2023-03-10 | 4.3 | CVE-2023-1337 MISC MISC |
| rapidload -- power-up_for_autoptimize | The RapidLoad Power-Up for Autoptimize plugin for WordPress is vulnerable to unauthorized cache modification due to a missing capability check on the attach_rule function in versions up to, and including, 1.7.1. This makes it possible for authenticated attackers with subscriber-level access to modify cache rules. | 2023-03-10 | 4.3 | CVE-2023-1338 MISC MISC |
| rapidload -- power-up_for_autoptimize | The RapidLoad Power-Up for Autoptimize plugin for WordPress is vulnerable to unauthorized settings update due to a missing capability check on the uucss_update_rule function in versions up to, and including, 1.7.1. This makes it possible for authenticated attackers with subscriber-level access to update caching rules. | 2023-03-10 | 4.3 | CVE-2023-1339 MISC MISC |
| rapidload -- power-up_for_autoptimize | The RapidLoad Power-Up for Autoptimize plugin for WordPress is vulnerable to Cross-Site Request Forgery in versions up to, and including, 1.7.1. This is due to missing or incorrect nonce validation on the clear_uucss_logs function. This makes it possible for unauthenticated attackers to clear plugin logs via a forged request granted they can trick a site administrator into performing an action such as clicking on a link. | 2023-03-10 | 4.3 | CVE-2023-1340 MISC MISC |
| rapidload -- power-up_for_autoptimize | The RapidLoad Power-Up for Autoptimize plugin for WordPress is vulnerable to Cross-Site Request Forgery in versions up to, and including, 1.7.1. This is due to missing or incorrect nonce validation on the ajax_deactivate function. This makes it possible for unauthenticated attackers to turn off caching via a forged request granted they can trick a site administrator into performing an action such as clicking on a link. | 2023-03-10 | 4.3 | CVE-2023-1341 MISC MISC |
| rapidload -- power-up_for_autoptimize | The RapidLoad Power-Up for Autoptimize plugin for WordPress is vulnerable to Cross-Site Request Forgery in versions up to, and including, 1.7.1. This is due to missing or incorrect nonce validation on the ucss_connect function. This makes it possible for unauthenticated attackers to connect the site to a new license key via a forged request granted they can trick a site administrator into performing an action such as clicking on a link. | 2023-03-10 | 4.3 | CVE-2023-1342 MISC MISC |
| rapidload -- power-up_for_autoptimize | The RapidLoad Power-Up for Autoptimize plugin for WordPress is vulnerable to Cross-Site Request Forgery in versions up to, and including, 1.7.1. This is due to missing or incorrect nonce validation on the attach_rule function. This makes it possible for unauthenticated attackers to modify the plugin's cache via a forged request granted they can trick a site administrator into performing an action such as clicking on a link. | 2023-03-10 | 4.3 | CVE-2023-1343 MISC MISC |
| rapidload -- power-up_for_autoptimize | The RapidLoad Power-Up for Autoptimize plugin for WordPress is vulnerable to Cross-Site Request Forgery in versions up to, and including, 1.7.1. This is due to missing or incorrect nonce validation on the uucss_update_rule function. This makes it possible for unauthenticated attackers to modify the plugin's cache via a forged request granted they can trick a site administrator into performing an action such as clicking on a link. | 2023-03-10 | 4.3 | CVE-2023-1344 MISC MISC |
| rapidload -- power-up_for_autoptimize | The RapidLoad Power-Up for Autoptimize plugin for WordPress is vulnerable to Cross-Site Request Forgery in versions up to, and including, 1.7.1. This is due to missing or incorrect nonce validation on the queue_posts function. This makes it possible for unauthenticated attackers to modify the plugin's cache via a forged request granted they can trick a site administrator into performing an action such as clicking on a link. | 2023-03-10 | 4.3 | CVE-2023-1345 MISC MISC |
| rapidload -- power-up_for_autoptimize | The RapidLoad Power-Up for Autoptimize plugin for WordPress is vulnerable to Cross-Site Request Forgery in versions up to, and including, 1.7.1. This is due to missing or incorrect nonce validation on the clear_page_cache function. This makes it possible for unauthenticated attackers to clear the plugin's cache via a forged request granted they can trick a site administrator into performing an action such as clicking on a link. | 2023-03-10 | 4.3 | CVE-2023-1346 MISC MISC |
| pixelyoursite -- pixelyoursite | Cross-Site Request Forgery (CSRF) vulnerability in PixelYourSite PixelYourSite – Your smart PIXEL (TAG) Manager plugin <= 9.3.0 versions. | 2023-03-13 | 4.3 | CVE-2023-22700 MISC |
| a2hosting -- a2_optimized | Cross-Site Request Forgery (CSRF) vulnerability in A2 Hosting A2 Optimized WP plugin <= 3.0.4 versions. | 2023-03-13 | 4.3 | CVE-2023-23711 MISC |
| siemens -- ruggedcom_crossbow | A vulnerability has been identified in RUGGEDCOM CROSSBOW (All versions < V5.3). The client query handler of the affected application fails to check for proper permissions for specific read queries. This could allow authenticated remote attackers to access data they are not authorized for. | 2023-03-14 | 4.3 | CVE-2023-27462 MISC |
| jenkins -- jenkins | Jenkins 2.393 and earlier, LTS 2.375.3 and earlier shows temporary directories related to job workspaces, which allows attackers with Item/Workspace permission to access their contents. | 2023-03-10 | 4.3 | CVE-2023-27902 MISC |
| Primary Vendor -- Product | Description | Published | CVSS Score | Source & Patch Info |
|---|---|---|---|---|
| easyappointments -- easyappointments | Code Injection in GitHub repository alextselegidis/easyappointments prior to 1.5.0. | 2023-03-13 | 3.8 | CVE-2023-1367 CONFIRM MISC |
| ibexa -- commerce | An issue was discovered in eZ Platform Ibexa Kernel before 1.3.19. It allows determining account existence via a timing attack. | 2023-03-12 | 3.7 | CVE-2022-48366 MISC MISC MISC |
| ibm -- robotic_process_automation_as_a_service | IBM Robotic Process Automation 21.0.1 through 21.0.7 and 23.0.0 through 23.0.1 could allow a user with physical access to the system due to session tokens for not being invalidated after a password reset. IBM X-Force ID: 243710. | 2023-03-15 | 3.2 | CVE-2023-22591 MISC MISC |
| microsoft -- multiple_products | Microsoft SharePoint Server Spoofing Vulnerability | 2023-03-14 | 3.1 | CVE-2023-23395 MISC |
| Primary Vendor -- Product | Description | Published | CVSS Score | Source & Patch Info |
|---|---|---|---|---|
| markdown_edit -- markdown_edit | Cross Site Scripting vulnerability found in Markdown Edit allows a remote attacker to execute arbitrary code via the edit parameter of the webpage. | 2023-03-16 | not yet calculated | CVE-2020-19947 MISC |
| depositgame -- depositgame | An issue found in DepositGame v.1.0 allows an attacker to gain sensitive information via the GetBonusWithdraw and withdraw functions. | 2023-03-16 | not yet calculated | CVE-2020-22647 MISC |
| ibm -- financial_transaction_manager | IBM Financial Transaction Manager for High Value Payments for Multi-Platform 3.2.0 through 3.2.10 allows web pages to be stored locally which can be read by another user on the system. IBM X-Force ID: 183329. | 2023-03-15 | not yet calculated | CVE-2020-4556 MISC MISC |
| dell -- multiple_products | Dell EMC Unisphere for PowerMax versions before 9.1.0.27, Dell EMC Unisphere for PowerMax Virtual Appliance versions before 9.1.0.27, and PowerMax OS Release 5978 contain an improper certificate validation vulnerability. An unauthenticated remote attacker may potentially exploit this vulnerability to carry out a man-in-the-middle attack by supplying a crafted certificate and intercepting the victim's traffic to view or modify a victim’s data in transit. | 2023-03-17 | not yet calculated | CVE-2021-21548 MISC |
| uwamp.exe -- uwamp.exe | An issue found in UwAmp v.1.1, 1.2, 1.3, 2.0, 2.1, 2.2, 2.2.1, 3.0.0, 3.0.1, 3.0.2 allows a remote attacker to execute arbitrary code via a crafted DLL. | 2023-03-16 | not yet calculated | CVE-2021-31637 MISC |
| wordpress -- wordpress | Unauth. Stored Cross-Site Scripting (XSS) vulnerability in WPMU DEV Forminator – Contact Form, Payment Form & Custom Form Builder plugin <= 1.14.11 versions. | 2023-03-16 | not yet calculated | CVE-2021-36821 MISC |
| pev -- pev | A Buffer Overflow vulnerabilityexists in Pev 0.81 via the pe_exports function from exports.c.. The array offsets_to_Names is dynamically allocated on the stack using exp->NumberOfFunctions as its size. However, the loop uses exp->NumberOfNames to iterate over it and set its components value. Therefore, the loop code assumes that exp->NumberOfFunctions is greater than ordinal at each iteration. This can lead to arbitrary code execution. | 2023-03-13 | not yet calculated | CVE-2021-45423 MISC |
| jackson-databind -- jackson-databind | jackson-databind 2.10.x through 2.12.x before 2.12.6 and 2.13.x before 2.13.1 allows attackers to cause a denial of service (2 GB transient heap usage per read) in uncommon situations involving JsonNode JDK serialization. | 2023-03-18 | not yet calculated | CVE-2021-46877 MISC MISC |
| octopus_deploy -- octopus_server | In affected versions of Octopus Deploy it is possible for a user to view Tagsets without being explicitly assigned permissions to view these items | 2023-03-13 | not yet calculated | CVE-2022-2258 MISC |
| octopus_deploy -- octopus_server | In affected versions of Octopus Deploy it is possible for a user to view Workerpools without being explicitly assigned permissions to view these items | 2023-03-13 | not yet calculated | CVE-2022-2259 MISC |
| abb -- multiple_products | Use of Insufficiently Random Values vulnerability in ABB Pulsar Plus System Controller NE843_S, ABB Infinity DC Power Plant.This issue affects Pulsar Plus System Controller NE843_S : comcode 150042936; Infinity DC Power Plant: H5692448 G104 G842 G224L G630-4 G451C(2) G461(2) – comcode 150047415. | 2023-03-16 | not yet calculated | CVE-2022-26080 MISC |
| dell -- bios_for_poweredge_and_precision | Dell PowerEdge BIOS and Dell Precision BIOS contain an Improper SMM communication buffer verification vulnerability. A local malicious user with high Privileges may potentially exploit this vulnerability to perform arbitrary code execution or cause denial of service. | 2023-03-16 | not yet calculated | CVE-2022-34406 MISC |
| dell -- bios_for_poweredge_and_precision | Dell PowerEdge BIOS and Dell Precision BIOS contain an Improper SMM communication buffer verification vulnerability. A local malicious user with high Privileges may potentially exploit this vulnerability to perform arbitrary code execution or cause denial of service. | 2023-03-16 | not yet calculated | CVE-2022-34407 MISC |
| dell -- bios_for_poweredge_and_precision | Dell PowerEdge BIOS and Dell Precision BIOS contain an Improper SMM communication buffer verification vulnerability. A local malicious user with high Privileges may potentially exploit this vulnerability to perform arbitrary code execution or cause denial of service. | 2023-03-16 | not yet calculated | CVE-2022-34408 MISC |
| dell -- bios_for_poweredge_and_precision | Dell PowerEdge BIOS and Dell Precision BIOS contain an Improper SMM communication buffer verification vulnerability. A local malicious user with high Privileges may potentially exploit this vulnerability to perform arbitrary code execution or cause denial of service. | 2023-03-16 | not yet calculated | CVE-2022-34409 MISC |
| dell -- bios_for_poweredge_and_precision | Dell PowerEdge BIOS and Dell Precision BIOS contain an Improper SMM communication buffer verification vulnerability. A local malicious user with high Privileges may potentially exploit this vulnerability to perform arbitrary code execution or cause denial of service. | 2023-03-16 | not yet calculated | CVE-2022-34410 MISC |
| dell -- bios_for_poweredge_and_precision | Dell PowerEdge BIOS and Dell Precision BIOS contain an Improper SMM communication buffer verification vulnerability. A local malicious user with high Privileges may potentially exploit this vulnerability to perform arbitrary code execution or cause denial of service. | 2023-03-16 | not yet calculated | CVE-2022-34411 MISC |
| dell -- bios_for_poweredge_and_precision | Dell PowerEdge BIOS and Dell Precision BIOS contain an Improper SMM communication buffer verification vulnerability. A local malicious user with high Privileges may potentially exploit this vulnerability to perform arbitrary code execution or cause denial of service. | 2023-03-16 | not yet calculated | CVE-2022-34412 MISC |
| dell -- bios_for_poweredge_and_precision | Dell PowerEdge BIOS and Dell Precision BIOS contain an Improper SMM communication buffer verification vulnerability. A local malicious user with high Privileges may potentially exploit this vulnerability to perform arbitrary code execution or cause denial of service. | 2023-03-16 | not yet calculated | CVE-2022-34413 MISC |
| dell -- bios_for_poweredge_and_precision | Dell PowerEdge BIOS and Dell Precision BIOS contain an Improper SMM communication buffer verification vulnerability. A local malicious user with high Privileges may potentially exploit this vulnerability to perform arbitrary code execution or cause denial of service. | 2023-03-16 | not yet calculated | CVE-2022-34414 MISC |
| dell -- bios_for_poweredge_and_precision | Dell PowerEdge BIOS and Dell Precision BIOS contain an Improper SMM communication buffer verification vulnerability. A local malicious user with high Privileges may potentially exploit this vulnerability to perform arbitrary code execution or cause denial of service. | 2023-03-16 | not yet calculated | CVE-2022-34415 MISC |
| dell -- bios_for_poweredge_and_precision | Dell PowerEdge BIOS and Dell Precision BIOS contain an Improper SMM communication buffer verification vulnerability. A local malicious user with high Privileges may potentially exploit this vulnerability to perform arbitrary code execution or cause denial of service. | 2023-03-16 | not yet calculated | CVE-2022-34416 MISC |
| dell -- bios_for_poweredge_and_precision | Dell PowerEdge BIOS and Dell Precision BIOS contain an Improper SMM communication buffer verification vulnerability. A local malicious user with high Privileges may potentially exploit this vulnerability to perform arbitrary code execution or cause denial of service. | 2023-03-16 | not yet calculated | CVE-2022-34417 MISC |
| dell -- bios_for_poweredge_and_precision | Dell PowerEdge BIOS and Dell Precision BIOS contain an Improper SMM communication buffer verification vulnerability. A local malicious user with high Privileges may potentially exploit this vulnerability to perform arbitrary code execution or cause denial of service. | 2023-03-16 | not yet calculated | CVE-2022-34418 MISC |
| dell -- bios_for_poweredge_and_precision | Dell PowerEdge BIOS and Dell Precision BIOS contain an Improper SMM communication buffer verification vulnerability. A local malicious user with high Privileges may potentially exploit this vulnerability to perform arbitrary code execution or cause denial of service. | 2023-03-16 | not yet calculated | CVE-2022-34419 MISC |
| dell -- bios_for_poweredge_and_precision | Dell PowerEdge BIOS and Dell Precision BIOS contain an Improper SMM communication buffer verification vulnerability. A local malicious user with high Privileges may potentially exploit this vulnerability to perform arbitrary code execution or cause denial of service. | 2023-03-16 | not yet calculated | CVE-2022-34420 MISC |
| dell -- bios_for_poweredge_and_precision | Dell PowerEdge BIOS and Dell Precision BIOS contain an Improper SMM communication buffer verification vulnerability. A local malicious user with high Privileges may potentially exploit this vulnerability to perform arbitrary code execution or cause denial of service. | 2023-03-16 | not yet calculated | CVE-2022-34421 MISC |
| dell -- bios_for_poweredge_and_precision | Dell PowerEdge BIOS and Dell Precision BIOS contain an Improper SMM communication buffer verification vulnerability. A local malicious user with high Privileges may potentially exploit this vulnerability to perform arbitrary code execution or cause denial of service. | 2023-03-16 | not yet calculated | CVE-2022-34422 MISC |
| dell -- bios_for_poweredge_and_precision | Dell PowerEdge BIOS and Dell Precision BIOS contain an Improper SMM communication buffer verification vulnerability. A local malicious user with high Privileges may potentially exploit this vulnerability to perform arbitrary code execution or cause denial of service. | 2023-03-16 | not yet calculated | CVE-2022-34423 MISC |
| wordpress -- wordpress | Cross-Site Request Forgery (CSRF) vulnerability in Social Login WP plugin <= 5.0.0.0 versions. | 2023-03-16 | not yet calculated | CVE-2022-38063 MISC |
| wordpress -- wordpress | Stored Cross-Site Scripting (XSS) vulnerability in ThemeKraft Post Form – Registration Form – Profile Form for User Profiles and Content Forms for User Submissions plugin <= 2.7.5 versions. | 2023-03-16 | not yet calculated | CVE-2022-38971 MISC |
| octopus_deploy -- octopus_server | In affected versions of Octopus Deploy it is possible for a user to introduce code via offline package creation | 2023-03-16 | not yet calculated | CVE-2022-4009 MISC |
| wordpress -- wordpress | Cross-Site Scripting (XSS) vulnerability in Dario Curvino Yasr – Yet Another Stars Rating plugin <= 3.1.2 versions. | 2023-03-16 | not yet calculated | CVE-2022-40699 MISC |
| wordpress -- wordpress | Stored Cross-Site Scripting (XSS) vulnerability in John West Slideshow SE plugin <= 2.5.5 versions. | 2023-03-16 | not yet calculated | CVE-2022-41554 MISC |
| tenable -- multiple_products | A vulnerability was reported where through modifying the scan variables, an authenticated user in Tenable products, that has Scan Policy Configuration roles, could manipulate audit policy variables to execute arbitrary commands on credentialed scan targets. | 2023-03-15 | not yet calculated | CVE-2022-4313 MISC |
| ghost -- node-sqlite3 | A code execution vulnerability exists in the Statement Bindings functionality of Ghost Foundation node-sqlite3 5.1.1. A specially-crafted Javascript file can lead to arbitrary code execution. An attacker can provide malicious input to trigger this vulnerability. | 2023-03-16 | not yet calculated | CVE-2022-43441 MISC MISC |
| wordpress -- wordpress | Stored Cross-Site Scripting (XSS) vulnerability in John West Slideshow SE plugin <= 2.5.5 versions. | 2023-03-17 | not yet calculated | CVE-2022-43461 MISC |
| eip_stack_group_opener -- eip_stack_group_opener | An out-of-bounds write vulnerability exists in the GetAttributeList attribute_count_request functionality of EIP Stack Group OpENer development commit 58ee13c. A specially crafted EtherNet/IP request can lead to an out-of-bounds write, potentially causing the server to crash or allow for remote code execution. An attacker can send a series of EtherNet/IP requests to trigger this vulnerability. | 2023-03-16 | not yet calculated | CVE-2022-43604 MISC |
| eip_stack_group_opener -- eip_stack_group_opener | An out-of-bounds write vulnerability exists in the SetAttributeList attribute_count_request functionality of EIP Stack Group OpENer development commit 58ee13c. A specially crafted EtherNet/IP request can lead to an out of bounds write, potentially causing the server to crash or allow for remote code execution. An attacker can send a series of EtherNet/IP requests to trigger this vulnerability. | 2023-03-16 | not yet calculated | CVE-2022-43605 MISC |
| eip_stack_group_opener -- eip_stack_group_opener | A use-of-uninitialized-pointer vulnerability exists in the Forward Open connection_management_entry functionality of EIP Stack Group OpENer development commit 58ee13c. A specially-crafted EtherNet/IP request can lead to use of a null pointer, causing the server to crash. An attacker can send a series of EtherNet/IP requests to trigger this vulnerability. | 2023-03-16 | not yet calculated | CVE-2022-43606 MISC |
| suse -- opensuse_factory | An Improper Handling of Exceptional Conditions vulnerability in obs-service-go_modules of openSUSE Factory allows attackers that can influence the call to the service to delete files and directories on the system of the victim. This issue affects: SUSE openSUSE Factory obs-service-go_modules versions prior to 0.6.1. | 2023-03-15 | not yet calculated | CVE-2022-45155 CONFIRM |
| wordpress -- wordpress | Stored Cross-Site Scripting (XSS) vulnerability in Fabian von Allmen WP Calendar plugin <= 1.5.3 versions. | 2023-03-17 | not yet calculated | CVE-2022-45814 MISC |
| wordpress -- wordpress | Cross-Site Scripting (XSS) vulnerability in Erin Garscadden GC Testimonials plugin <= 1.3.2 versions. | 2023-03-17 | not yet calculated | CVE-2022-45817 MISC |
| wordpress -- wordpress | Cross-Site Request Forgery (CSRF) vulnerability in Obox Themes Launchpad – Coming Soon & Maintenance Mode plugin <= 1.0.13 versions. | 2023-03-17 | not yet calculated | CVE-2022-46854 MISC |
| wordpress -- wordpress | Cross-Site Request Forgery (CSRF) vulnerability in Chasil Universal Star Rating plugin <= 2.1.0 version. | 2023-03-17 | not yet calculated | CVE-2022-46867 MISC |
| rockwell_automation -- modbus_tcp_server_add_on_instructions | Rockwell Automation Modbus TCP Server AOI prior to 2.04.00 is vulnerable to an unauthorized user sending a malformed message that could cause the controller to respond with a copy of the most recent response to the last valid request. If exploited, an unauthorized user could read the connected device’s Modbus TCP Server AOI information. | 2023-03-17 | not yet calculated | CVE-2023-0027 MISC |
| eclipse_foundation -- business_intelligence_reporting_tool | In Eclipse BIRT, starting from version 2.6.2, the default configuration allowed to retrieve a report from the same host using an absolute HTTP path for the report parameter (e.g. __report= http://xyz.com/report.rptdesign ). If the host indicated in the __report parameter matched the HTTP Host header value, the report would be retrieved. However, the Host header can be tampered with on some configurations where no virtual hosts are put in place (e.g. in the default configuration of Apache Tomcat) or when the default host points to the BIRT server. This vulnerability was patched on Eclipse BIRT 4.13. | 2023-03-15 | not yet calculated | CVE-2023-0100 CONFIRM |
| general_electric_digital -- proficy_ifix | GE Digital Proficy iFIX 2022, GE Digital Proficy iFIX v6.1, and GE Digital Proficy iFIX v6.5 are vulnerable to code injection, which may allow an attacker to insert malicious configuration files in the expected web server execution path and gain full control of the HMI software. | 2023-03-16 | not yet calculated | CVE-2023-0598 MISC MISC |
| omron -- multiple_products | Omron CJ1M unit v4.0 and prior has improper access controls on the memory region where the UM password is stored. If an adversary issues a PROGRAM AREA WRITE command to a specific memory region, they could overwrite the password. This may lead to disabling UM protections or setting a non-ASCII password (non-keyboard characters) and preventing an engineer from viewing or modifying the user program. | 2023-03-16 | not yet calculated | CVE-2023-0811 MISC MISC |
| steptools -- v18sp1_ifcmesh_library | STEPTools v18SP1 ifcmesh library (v18.1) is affected due to a null pointer dereference, which could allow an attacker to deny application usage when reading a specially constructed file, resulting in an application crash. | 2023-03-13 | not yet calculated | CVE-2023-0973 MISC |
| utarit_information_technologies -- persolus | Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in Utarit Information Technologies Persolus allows SQL Injection. This issue affects Persolus: before 2.03.93. | 2023-03-17 | not yet calculated | CVE-2023-1152 MISC |
| wordpress -- wordpress | The Bookly plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the full name value in versions up to, and including, 21.5 due to insufficient input sanitization and output escaping. This makes it possible for unauthenticated attackers to inject arbitrary web scripts in pages that will execute whenever a user accesses an injected page. | 2023-03-17 | not yet calculated | CVE-2023-1172 MISC MISC |
| aveva -- plant_scada/telemetry_server | The listed versions of AVEVA Plant SCADA and AVEVA Telemetry Server are vulnerable to an improper authorization exploit which could allow an unauthenticated user to remotely read data, cause denial of service, and tamper with alarm states. | 2023-03-16 | not yet calculated | CVE-2023-1256 MISC |
| netgear -- rax30_(ax2400) | Netgear RAX30 (AX2400), prior to version 1.0.6.74, was affected by an authentication bypass vulnerability, allowing an unauthenticated attacker to gain administrative access to the device's web management interface by resetting the admin password. | 2023-03-14 | not yet calculated | CVE-2023-1327 MISC |
| sourcecodester -- friendly_island_pizza_website_and_ordering_system | A vulnerability was found in SourceCodester Friendly Island Pizza Website and Ordering System 1.0. It has been rated as critical. This issue affects some unknown processing of the file addmem.php of the component POST Parameter Handler. The manipulation of the argument firstname leads to sql injection. The attack may be initiated remotely. The exploit has been disclosed to the public and may be used. The associated identifier of this vulnerability is VDB-223127. | 2023-03-15 | not yet calculated | CVE-2023-1379 MISC MISC MISC |
| tp-link -- archer_ax21_(ax1800)_firmware | TP-Link Archer AX21 (AX1800) firmware versions before 1.1.4 Build 20230219 contained a command injection vulnerability in the country form of the /cgi-bin/luci;stok=/locale endpoint on the web management interface. Specifically, the country parameter of the write operation was not sanitized before being used in a call to popen(), allowing an unauthenticated attacker to inject commands, which would be run as root, with a simple POST request. | 2023-03-15 | not yet calculated | CVE-2023-1389 MISC |
| linux -- kernel | A remote denial of service vulnerability was found in the Linux kernel’s TIPC kernel module. The while loop in tipc_link_xmit() hits an unknown state while attempting to parse SKBs, which are not in the queue. Sending two small UDP packets to a system with a UDP bearer results in the CPU utilization for the system to instantly spike to 100%, causing a denial of service condition. | 2023-03-16 | not yet calculated | CVE-2023-1390 MISC MISC MISC |
| simple_art_gallery -- simple_art_gallery | A vulnerability classified as critical has been found in Simple Art Gallery 1.0. Affected is an unknown function of the file adminHome.php. The manipulation of the argument social_facebook leads to sql injection. It is possible to launch the attack remotely. The exploit has been disclosed to the public and may be used. The identifier of this vulnerability is VDB-223128. | 2023-03-15 | not yet calculated | CVE-2023-1416 MISC MISC MISC |
| sourcecodester -- friendly_island_pizza_website_and_ordering_system | A vulnerability classified as problematic was found in SourceCodester Friendly Island Pizza Website and Ordering System 1.0. Affected by this vulnerability is an unknown functionality of the file cashconfirm.php of the component POST Parameter Handler. The manipulation of the argument transactioncode leads to cross site scripting. The attack can be launched remotely. The exploit has been disclosed to the public and may be used. The identifier VDB-223129 was assigned to this vulnerability. | 2023-03-15 | not yet calculated | CVE-2023-1418 MISC MISC MISC |
| mattermost -- mattermost | A reflected cross-site scripting vulnerability in the OAuth flow completion endpoints in Mattermost allows an attacker to send AJAX requests on behalf of the victim via sharing a crafted link with a malicious state parameter. | 2023-03-15 | not yet calculated | CVE-2023-1421 MISC |
| pimcore -- pimcore | Cross-site Scripting (XSS) - Reflected in GitHub repository pimcore/pimcore prior to 10.5.19. | 2023-03-16 | not yet calculated | CVE-2023-1429 CONFIRM MISC |
| wordpress -- wordpress | The WP Simple Shopping Cart plugin for WordPress is vulnerable to Sensitive Information Exposure in versions up to, and including, 4.6.3 due to the plugin saving shopping cart data exports in a publicly accessible location (/wp-content/plugins/wordpress-simple-paypal-shopping-cart/includes/admin/). This makes it possible for unauthenticated attackers to view information that should be limited to administrators only and can include data like first name, last name, email, address, IP Address, and more. | 2023-03-16 | not yet calculated | CVE-2023-1431 MISC MISC |
| sourcecodester -- online_food_ordering_system | A vulnerability was found in SourceCodester Online Food Ordering System 2.0 and classified as critical. Affected by this issue is some unknown functionality of the file /fos/admin/ajax.php?action=save_settings of the component POST Request Handler. The manipulation leads to improper access controls. The attack may be launched remotely. VDB-223214 is the identifier assigned to this vulnerability. | 2023-03-16 | not yet calculated | CVE-2023-1432 MISC MISC |
| sourcecodester -- gadget_works_online_ordering_system | A vulnerability was found in SourceCodester Gadget Works Online Ordering System 1.0. It has been classified as problematic. This affects an unknown part of the file admin/products/controller.php?action=add of the component Products Handler. The manipulation of the argument filename leads to unrestricted upload. It is possible to initiate the attack remotely. The exploit has been disclosed to the public and may be used. The associated identifier of this vulnerability is VDB-223215. | 2023-03-16 | not yet calculated | CVE-2023-1433 MISC MISC MISC |
| sourcecodester -- medicine_tracker_system | A vulnerability, which was classified as critical, has been found in SourceCodester Medicine Tracker System 1.0. This issue affects some unknown processing of the file medicines/view_details.php of the component GET Parameter Handler. The manipulation of the argument GET leads to sql injection. The attack may be initiated remotely. The exploit has been disclosed to the public and may be used. The associated identifier of this vulnerability is VDB-223283. | 2023-03-17 | not yet calculated | CVE-2023-1439 MISC MISC MISC |
| sourcecodester -- automatic_question_paper_generator_system | A vulnerability, which was classified as critical, was found in SourceCodester Automatic Question Paper Generator System 1.0. Affected is an unknown function of the file users/user/manage_user.php of the component GET Parameter Handler. The manipulation of the argument id leads to sql injection. It is possible to launch the attack remotely. The exploit has been disclosed to the public and may be used. The identifier of this vulnerability is VDB-223284. | 2023-03-17 | not yet calculated | CVE-2023-1440 MISC MISC MISC |
| sourcecodester -- automatic_question_paper_generator_system | A vulnerability has been found in SourceCodester Automatic Question Paper Generator System 1.0 and classified as critical. Affected by this vulnerability is an unknown functionality of the file admin/courses/view_course.php of the component GET Parameter Handler. The manipulation of the argument id leads to sql injection. The attack can be launched remotely. The exploit has been disclosed to the public and may be used. The identifier VDB-223285 was assigned to this vulnerability. | 2023-03-17 | not yet calculated | CVE-2023-1441 MISC MISC MISC |
| qykcms -- qykcms | A vulnerability was found in Meizhou Qingyunke QYKCMS 4.3.0. It has been classified as problematic. This affects an unknown part of the file /admin_system/api.php of the component Update Handler. The manipulation of the argument downurl leads to unrestricted upload. It is possible to initiate the attack remotely. The exploit has been disclosed to the public and may be used. The associated identifier of this vulnerability is VDB-223287. | 2023-03-17 | not yet calculated | CVE-2023-1442 MISC MISC MISC |
| filseclab -- twister_antivirus_8 | A vulnerability was found in Filseclab Twister Antivirus 8. It has been declared as problematic. This vulnerability affects unknown code in the library fildds.sys of the component IoControlCode Handler. The manipulation leads to denial of service. The attack can be initiated remotely. The exploit has been disclosed to the public and may be used. The identifier of this vulnerability is VDB-223288. | 2023-03-17 | not yet calculated | CVE-2023-1443 MISC MISC MISC MISC |
| filseclab -- twister_antivirus_8 | A vulnerability was found in Filseclab Twister Antivirus 8. It has been rated as critical. This issue affects some unknown processing in the library fildds.sys of the component IoControlCode Handler. The manipulation leads to denial of service. The attack may be initiated remotely. The exploit has been disclosed to the public and may be used. The identifier VDB-223289 was assigned to this vulnerability. | 2023-03-17 | not yet calculated | CVE-2023-1444 MISC MISC MISC MISC |
| filseclab -- twister_antivirus_8 | A vulnerability classified as problematic has been found in Filseclab Twister Antivirus 8. Affected is an unknown function in the library fildds.sys of the component IoControlCode Handler. The manipulation leads to denial of service. The attack needs to be approached locally. The exploit has been disclosed to the public and may be used. VDB-223290 is the identifier assigned to this vulnerability. | 2023-03-17 | not yet calculated | CVE-2023-1445 MISC MISC MISC MISC |
| watchdog -- anti-virus | A vulnerability classified as problematic was found in Watchdog Anti-Virus 1.4.214.0. Affected by this vulnerability is an unknown functionality in the library wsdk-driver.sys of the component IoControlCode Handler. The manipulation leads to denial of service. An attack has to be approached locally. The exploit has been disclosed to the public and may be used. The associated identifier of this vulnerability is VDB-223291. | 2023-03-17 | not yet calculated | CVE-2023-1446 MISC MISC MISC MISC |
| sourcecodester -- medicine_tracker_system | A vulnerability, which was classified as problematic, has been found in SourceCodester Medicine Tracker System 1.0. Affected by this issue is some unknown functionality of the file app/?page=medicines/manage_medicine.They. The manipulation of the argument name/description with the input alert('2') leads to cross site scripting. The attack may be launched remotely. The identifier of this vulnerability is VDB-223292. | 2023-03-17 | not yet calculated | CVE-2023-1447 MISC MISC |
| gpac -- gpac | A vulnerability, which was classified as problematic, was found in GPAC 2.3-DEV-rev35-gbbca86917-master. This affects the function gf_m2ts_process_sdt of the file media_tools/mpegts.c. The manipulation leads to heap-based buffer overflow. Attacking locally is a requirement. The exploit has been disclosed to the public and may be used. It is recommended to apply a patch to fix this issue. The identifier VDB-223293 was assigned to this vulnerability. | 2023-03-17 | not yet calculated | CVE-2023-1448 MISC MISC MISC MISC |
| gpac -- gpac | A vulnerability has been found in GPAC 2.3-DEV-rev35-gbbca86917-master and classified as problematic. This vulnerability affects the function gf_av1_reset_state of the file media_tools/av_parsers.c. The manipulation leads to double free. It is possible to launch the attack on the local host. The exploit has been disclosed to the public and may be used. It is recommended to apply a patch to fix this issue. VDB-223294 is the identifier assigned to this vulnerability. | 2023-03-17 | not yet calculated | CVE-2023-1449 MISC MISC MISC MISC |
| mp4v2_trackdump -- mp4v2_trackdump | A vulnerability was found in MP4v2 2.1.2 and classified as problematic. This issue affects the function DumpTrack of the file mp4trackdump.cpp. The manipulation leads to denial of service. The attack needs to be approached locally. The exploit has been disclosed to the public and may be used. The associated identifier of this vulnerability is VDB-223295. | 2023-03-17 | not yet calculated | CVE-2023-1450 MISC MISC MISC MISC |
| mp4v2_trackdump -- mp4v2_trackdump | A vulnerability was found in MP4v2 2.1.2. It has been classified as problematic. Affected is the function mp4v2::impl::MP4Track::GetSampleFileOffset of the file mp4track.cpp. The manipulation leads to denial of service. An attack has to be approached locally. The exploit has been disclosed to the public and may be used. The identifier of this vulnerability is VDB-223296. | 2023-03-17 | not yet calculated | CVE-2023-1451 MISC MISC MISC MISC |
| gpac -- gpac | A vulnerability was found in GPAC 2.3-DEV-rev35-gbbca86917-master. It has been declared as critical. Affected by this vulnerability is an unknown functionality of the file filters/load_text.c. The manipulation leads to buffer overflow. Local access is required to approach this attack. The exploit has been disclosed to the public and may be used. It is recommended to apply a patch to fix this issue. The identifier VDB-223297 was assigned to this vulnerability. | 2023-03-17 | not yet calculated | CVE-2023-1452 MISC MISC MISC MISC |
| watchdog -- watchdog_antivirus | A vulnerability was found in Watchdog Anti-Virus 1.4.214.0. It has been rated as critical. Affected by this issue is some unknown functionality in the library wsdk-driver.sys of the component IoControlCode Handler. The manipulation leads to improper access controls. Attacking locally is a requirement. The exploit has been disclosed to the public and may be used. VDB-223298 is the identifier assigned to this vulnerability. | 2023-03-17 | not yet calculated | CVE-2023-1453 MISC MISC MISC MISC |
| jeecg_boot_sqli -- jeecg_boot_sqli | A vulnerability classified as critical has been found in jeecg-boot 3.5.0. This affects an unknown part of the file jmreport/qurestSql. The manipulation of the argument apiSelectId leads to sql injection. It is possible to initiate the attack remotely. The exploit has been disclosed to the public and may be used. The associated identifier of this vulnerability is VDB-223299. | 2023-03-17 | not yet calculated | CVE-2023-1454 MISC MISC MISC |
| sourcecodester -- online_pizza_ordering_system | A vulnerability classified as critical was found in SourceCodester Online Pizza Ordering System 1.0. This vulnerability affects unknown code of the file admin/ajax.php?action=login2 of the component Login Page. The manipulation of the argument email with the input abc%40qq.com' AND (SELECT 9110 FROM (SELECT(SLEEP(5)))XSlc) AND 'jFNl'='jFNl leads to sql injection. The attack can be initiated remotely. The exploit has been disclosed to the public and may be used. The identifier of this vulnerability is VDB-223300. | 2023-03-17 | not yet calculated | CVE-2023-1455 MISC MISC |
| sourcecodester -- canteen_management_system | A vulnerability was found in SourceCodester Canteen Management System 1.0 and classified as critical. Affected by this issue is some unknown functionality of the file changeUsername.php. The manipulation of the argument username leads to sql injection. The attack may be launched remotely. The exploit has been disclosed to the public and may be used. The identifier of this vulnerability is VDB-223304. | 2023-03-17 | not yet calculated | CVE-2023-1459 MISC MISC MISC |
| sourcecoderster -- online_pizza_ordering_system | A vulnerability was found in SourceCodester Online Pizza Ordering System 1.0. It has been classified as critical. This affects an unknown part of the file admin/ajax.php?action=save_user of the component Password Change Handler. The manipulation leads to improper authentication. It is possible to initiate the attack remotely. The identifier VDB-223305 was assigned to this vulnerability. | 2023-03-17 | not yet calculated | CVE-2023-1460 MISC MISC |
| sourcecodester -- canteen_management_system | A vulnerability was found in SourceCodester Canteen Management System 1.0. It has been declared as critical. This vulnerability affects the function query of the file createCategories.php. The manipulation of the argument categoriesStatus leads to sql injection. The attack can be initiated remotely. VDB-223306 is the identifier assigned to this vulnerability. | 2023-03-17 | not yet calculated | CVE-2023-1461 MISC MISC MISC |
| teampass -- teampass | Improper Authorization in GitHub repository nilsteampassnet/teampass prior to 3.0.0.23. | 2023-03-17 | not yet calculated | CVE-2023-1463 CONFIRM MISC |
| sourcecodester -- medicine_tracker_system | A vulnerability, which was classified as critical, was found in SourceCodester Medicine Tracker System 1.0. This affects an unknown part of the file Users.php?f=save_user. The manipulation of the argument firstname/middlename/lastname/username/password leads to improper authentication. It is possible to initiate the attack remotely. The associated identifier of this vulnerability is VDB-223311. | 2023-03-17 | not yet calculated | CVE-2023-1464 MISC MISC |
| sourcecodester -- student_study_center_desk_management_system | A vulnerability was found in SourceCodester Student Study Center Desk Management System 1.0. It has been rated as critical. This issue affects the function view_student of the file admin/?page=students/view_student. The manipulation of the argument id with the input 3' AND (SELECT 2100 FROM (SELECT(SLEEP(5)))FWlC) AND 'butz'='butz leads to sql injection. The attack may be initiated remotely. The exploit has been disclosed to the public and may be used. The identifier VDB-223325 was assigned to this vulnerability. | 2023-03-17 | not yet calculated | CVE-2023-1466 MISC MISC |
| sourcecodester -- student_study_center_desk_management_system | A vulnerability classified as critical has been found in SourceCodester Student Study Center Desk Management System 1.0. Affected is an unknown function of the file Master.php?f=delete_img of the component POST Parameter Handler. The manipulation of the argument path with the input C%3A%2Ffoo.txt leads to path traversal. It is possible to launch the attack remotely. The exploit has been disclosed to the public and may be used. VDB-223326 is the identifier assigned to this vulnerability. | 2023-03-17 | not yet calculated | CVE-2023-1467 MISC MISC |
| sourcecodester -- student_study_center_desk_management_system | A vulnerability classified as critical was found in SourceCodester Student Study Center Desk Management System 1.0. Affected by this vulnerability is an unknown functionality of the file admin/?page=reports&date_from=2023-02-17&date_to=2023-03-17 of the component Report Handler. The manipulation of the argument date_from/date_to leads to sql injection. The attack can be launched remotely. The associated identifier of this vulnerability is VDB-223327. | 2023-03-17 | not yet calculated | CVE-2023-1468 MISC MISC |
| wordpress -- wordpress | The WP Express Checkout plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the ‘pec_coupon[code]’ parameter in versions up to, and including, 2.2.8 due to insufficient input sanitization and output escaping. This makes it possible for authenticated attackers with administrator-level access to inject arbitrary web scripts in pages that will execute whenever a user accesses an injected page. Note: This can potentially be exploited by lower-privileged users if the Admin Dashboard Access Permission setting it set for those users to access the dashboard. |
2023-03-17 | not yet calculated | CVE-2023-1469 MISC MISC |
| wordpress -- wordpress | The eCommerce Product Catalog plugin for WordPress is vulnerable to Stored Cross-Site Scripting via some of its settings parameters in versions up to, and including, 3.3.8 due to insufficient input sanitization and output escaping. This makes it possible for authenticated attackers, with administrator-level permissions and above, to inject arbitrary web scripts in pages that will execute whenever a user accesses an injected page. This only affects multi-site installations and installations where unfiltered_html has been disabled. | 2023-03-17 | not yet calculated | CVE-2023-1470 MISC MISC |
| wordpress -- wordpress | The WP Popup Banners plugin for WordPress is vulnerable to SQL Injection via the 'banner_id' parameter in versions up to, and including, 1.2.5 due to insufficient escaping on the user supplied parameter and lack of sufficient preparation on the existing SQL query. This makes it possible for authenticated attackers with minimal permissions, such as a subscrber, to append additional SQL queries into already existing queries that can be used to extract sensitive information from the database. | 2023-03-17 | not yet calculated | CVE-2023-1471 MISC MISC MISC |
| wordpress -- wordpress | The RapidLoad Power-Up for Autoptimize plugin for WordPress is vulnerable to Cross-Site Request Forgery in versions up to, and including, 1.7.1. This is due to missing or incorrect nonce validation on its AJAX actions. This makes it possible for unauthenticated attackers to invoke those functions, via forged request granted they can trick a site administrator into performing an action such as clicking on a link. Actions include resetting the API key, accessing or deleting log files, and deleting cache among others. | 2023-03-17 | not yet calculated | CVE-2023-1472 MISC MISC |
| sourcecodester -- automatic_question_paper_generator_system | A vulnerability classified as critical was found in SourceCodester Automatic Question Paper Generator System 1.0. This vulnerability affects unknown code of the file users/question_papers/manage_question_paper.php of the component GET Parameter Handler. The manipulation of the argument id leads to sql injection. The attack can be initiated remotely. The exploit has been disclosed to the public and may be used. The identifier of this vulnerability is VDB-223336. | 2023-03-17 | not yet calculated | CVE-2023-1474 MISC MISC MISC |
| sourcecodester -- canteen_management_system | A vulnerability, which was classified as critical, has been found in SourceCodester Canteen Management System 1.0. This issue affects the function query of the file createuser.php. The manipulation of the argument uemail leads to sql injection. The attack may be initiated remotely. The exploit has been disclosed to the public and may be used. The identifier VDB-223337 was assigned to this vulnerability. | 2023-03-17 | not yet calculated | CVE-2023-1475 MISC MISC MISC |
| sourcecodester -- monitoring_of_students_cyber_accounts_system | A vulnerability classified as critical has been found in SourceCodester Simple Music Player 1.0. Affected is an unknown function of the file save_music.php. The manipulation of the argument filename leads to unrestricted upload. It is possible to launch the attack remotely. The exploit has been disclosed to the public and may be used. VDB-223362 is the identifier assigned to this vulnerability. | 2023-03-18 | not yet calculated | CVE-2023-1479 MISC MISC MISC |
| sourcecodester -- monitoring_of_students_cyber_accounts_system | A vulnerability classified as critical was found in SourceCodester Monitoring of Students Cyber Accounts System 1.0. Affected by this vulnerability is an unknown functionality of the file login.php of the component POST Parameter Handler. The manipulation of the argument un leads to sql injection. The attack can be launched remotely. The exploit has been disclosed to the public and may be used. The associated identifier of this vulnerability is VDB-223363. | 2023-03-18 | not yet calculated | CVE-2023-1480 MISC MISC MISC |
| sourcecodester -- monitoring_of_students_cyber_accounts_system | A vulnerability, which was classified as problematic, has been found in SourceCodester Monitoring of Students Cyber Accounts System 1.0. Affected by this issue is some unknown functionality of the file modules/balance/index.php?view=balancelist of the component POST Parameter Handler. The manipulation of the argument id with the input ">alert(111) leads to cross site scripting. The attack may be launched remotely. The exploit has been disclosed to the public and may be used. The identifier of this vulnerability is VDB-223364. | 2023-03-18 | not yet calculated | CVE-2023-1481 MISC MISC MISC |
| hkcms -- hkcms | A vulnerability, which was classified as problematic, was found in HkCms 2.2.4.230206. This affects an unknown part of the file /admin.php/appcenter/local.html?type=addon of the component External Plugin Handler. The manipulation leads to code injection. It is possible to initiate the attack remotely. The exploit has been disclosed to the public and may be used. The identifier VDB-223365 was assigned to this vulnerability. | 2023-03-18 | not yet calculated | CVE-2023-1482 MISC MISC MISC |
| xiaobingby -- teacms | A vulnerability has been found in XiaoBingBy TeaCMS up to 2.0.2 and classified as critical. This vulnerability affects unknown code of the file /admin/getallarticleinfo. The manipulation of the argument searchInfo leads to sql injection. The attack can be initiated remotely. VDB-223366 is the identifier assigned to this vulnerability. | 2023-03-18 | not yet calculated | CVE-2023-1483 MISC MISC MISC |
| xzjie -- cms | A vulnerability was found in xzjie cms up to 1.0.3 and classified as critical. This issue affects some unknown processing of the file /api/upload. The manipulation of the argument uploadFile leads to unrestricted upload. The attack may be initiated remotely. The associated identifier of this vulnerability is VDB-223367. | 2023-03-18 | not yet calculated | CVE-2023-1484 MISC MISC MISC |
| sourcecodester -- young_entrepreneur_e-negosyo_system | A vulnerability classified as problematic has been found in SourceCodester Young Entrepreneur E-Negosyo System 1.0. This affects an unknown part of the file /bsenordering/index.php of the component GET Parameter Handler. The manipulation of the argument category with the input alert(222) leads to cross site scripting. It is possible to initiate the attack remotely. The exploit has been disclosed to the public and may be used. The associated identifier of this vulnerability is VDB-223371. | 2023-03-18 | not yet calculated | CVE-2023-1485 MISC MISC MISC |
| lespeed -- wisecleaner_wise_force_deleter | A vulnerability classified as problematic was found in Lespeed WiseCleaner Wise Force Deleter 1.5.3.54. This vulnerability affects unknown code in the library WiseUnlock64.sys of the component IoControlCode Handler. The manipulation leads to improper access controls. Local access is required to approach this attack. The exploit has been disclosed to the public and may be used. The identifier of this vulnerability is VDB-223372. | 2023-03-18 | not yet calculated | CVE-2023-1486 MISC MISC MISC MISC |
| lespeed -- wisecleaner_wise_system_monitor | A vulnerability, which was classified as problematic, has been found in Lespeed WiseCleaner Wise System Monitor 1.5.3.54. This issue affects some unknown processing in the library WiseHDInfo64.dll of the component IoControlCode Handler. The manipulation leads to denial of service. Attacking locally is a requirement. The exploit has been disclosed to the public and may be used. The identifier VDB-223373 was assigned to this vulnerability. | 2023-03-18 | not yet calculated | CVE-2023-1487 MISC MISC MISC MISC |
| lespeed -- wisecleaner_wise_system_monitor | A vulnerability, which was classified as problematic, was found in Lespeed WiseCleaner Wise System Monitor 1.5.3.54. Affected is an unknown function in the library WiseHDInfo64.dll of the component IoControlCode Handler. The manipulation leads to denial of service. It is possible to launch the attack on the local host. The exploit has been disclosed to the public and may be used. VDB-223374 is the identifier assigned to this vulnerability. | 2023-03-18 | not yet calculated | CVE-2023-1488 MISC MISC MISC MISC |
| lespeed -- wisecleaner_wise_system_monitor | A vulnerability has been found in Lespeed WiseCleaner Wise System Monitor 1.5.3.54 and classified as critical. Affected by this vulnerability is an unknown functionality in the library WiseHDInfo64.dll of the component IoControlCode Handler. The manipulation leads to improper access controls. The attack needs to be approached locally. The exploit has been disclosed to the public and may be used. The associated identifier of this vulnerability is VDB-223375. | 2023-03-18 | not yet calculated | CVE-2023-1489 MISC MISC MISC MISC |
| max_secure -- anti_virus_plus | A vulnerability was found in Max Secure Anti Virus Plus 19.0.2.1 and classified as critical. Affected by this issue is some unknown functionality in the library SDActMon.sys of the component IoControlCode Handler. The manipulation leads to improper access controls. An attack has to be approached locally. The exploit has been disclosed to the public and may be used. The identifier of this vulnerability is VDB-223376. | 2023-03-18 | not yet calculated | CVE-2023-1490 MISC MISC MISC MISC |
| max_secure -- anti_virus_plus | A vulnerability was found in Max Secure Anti Virus Plus 19.0.2.1. It has been classified as critical. This affects an unknown part in the library MaxCryptMon.sys of the component IoControlCode Handler. The manipulation leads to improper access controls. Local access is required to approach this attack. The exploit has been disclosed to the public and may be used. The identifier VDB-223377 was assigned to this vulnerability. | 2023-03-18 | not yet calculated | CVE-2023-1491 MISC MISC MISC MISC |
| max_secure -- anti_virus_plus | A vulnerability was found in Max Secure Anti Virus Plus 19.0.2.1. It has been declared as problematic. This vulnerability affects unknown code in the library MaxProc64.sys of the component IoControlCode Handler. The manipulation of the argument SystemBuffer leads to denial of service. Attacking locally is a requirement. The exploit has been disclosed to the public and may be used. VDB-223378 is the identifier assigned to this vulnerability. | 2023-03-18 | not yet calculated | CVE-2023-1492 MISC MISC MISC MISC |
| max_secure -- anti_virus_plus | A vulnerability was found in Max Secure Anti Virus Plus 19.0.2.1. It has been rated as problematic. This issue affects some unknown processing in the library MaxProctetor64.sys of the component IoControlCode Handler. The manipulation leads to denial of service. It is possible to launch the attack on the local host. The exploit has been disclosed to the public and may be used. The associated identifier of this vulnerability is VDB-223379. | 2023-03-18 | not yet calculated | CVE-2023-1493 MISC MISC MISC MISC |
| ibos -- ibos | A vulnerability classified as critical has been found in IBOS 4.5.5. Affected is an unknown function of the file ApiController.php. The manipulation of the argument emailids leads to sql injection. It is possible to launch the attack remotely. The exploit has been disclosed to the public and may be used. The identifier of this vulnerability is VDB-223380. | 2023-03-18 | not yet calculated | CVE-2023-1494 MISC MISC MISC |
| samsung_mobile -- multiple_mobile_devices | Improper access control vulnerability in Call application prior to SMR Mar-2023 Release 1 allows local attackers to access sensitive information without proper permission. | 2023-03-16 | not yet calculated | CVE-2023-21449 MISC |
| samsung_mobile -- multiple_mobile_devices | Improper usage of implicit intent in Bluetooth prior to SMR Mar-2023 Release 1 allows attacker to get MAC address of connected device. | 2023-03-16 | not yet calculated | CVE-2023-21452 MISC |
| samsung_mobile -- multiple_mobile_devices | Improper input validation vulnerability in SoftSim TA prior to SMR Mar-2023 Release 1 allows local attackers access to protected data. | 2023-03-16 | not yet calculated | CVE-2023-21453 MISC |
| samsung_mobile -- multiple_mobile_devices | Improper authorization in Samsung Keyboard prior to SMR Mar-2023 Release 1 allows physical attacker to access users text history on the lockscreen. | 2023-03-16 | not yet calculated | CVE-2023-21454 MISC |
| samsung_mobile -- exynos | Improper authorization implementation in Exynos baseband prior to SMR Mar-2023 Release 1 allows incorrect handling of unencrypted message. | 2023-03-16 | not yet calculated | CVE-2023-21455 MISC |
| samsung_mobile -- multiple_mobile_devices | Path traversal vulnerability in Galaxy Themes Service prior to SMR Mar-2023 Release 1 allows attacker to access arbitrary file with system uid. | 2023-03-16 | not yet calculated | CVE-2023-21456 MISC |
| samsung_mobile -- multiple_mobile_devices | Improper access control vulnerability in Bluetooth prior to SMR Mar-2023 Release 1 allows attackers to send file via Bluetooth without related permission. | 2023-03-16 | not yet calculated | CVE-2023-21457 MISC |
| samsung_mobile -- multiple_mobile_devices | Improper privilege management vulnerability in PhoneStatusBarPolicy in System UI prior to SMR Mar-2023 Release 1 allows attacker to turn off Do not disturb via unprotected intent. | 2023-03-16 | not yet calculated | CVE-2023-21458 MISC |
| samsung_mobile -- multiple_mobile_devices | Use after free vulnerability in decon driver prior to SMR Mar-2023 Release 1 allows attackers to cause memory access fault. | 2023-03-16 | not yet calculated | CVE-2023-21459 MISC |
| samsung_mobile -- multiple_mobile_devices | Improper authentication in SecSettings prior to SMR Mar-2023 Release 1 allows attacker to reset the setting. | 2023-03-16 | not yet calculated | CVE-2023-21460 MISC |
| samsung_mobile -- multiple_mobile_devices | Improper authorization vulnerability in AutoPowerOnOffConfirmDialog in Settings prior to SMR Mar-2023 Release 1 allows local attacker to turn device off via unprotected activity. | 2023-03-16 | not yet calculated | CVE-2023-21461 MISC |
| samsung_mobile -- multiple_mobile_devices | The sensitive information exposure vulnerability in Quick Share Agent prior to versions 3.5.14.18 in Android 12 and 3.5.16.20 in Android 13 allows to local attacker to access MAC address without related permission. | 2023-03-16 | not yet calculated | CVE-2023-21462 MISC |
| samsung_mobile -- multiple_mobile_devices | Improper access control vulnerability in MyFiles application prior to versions 12.2.09.0 in Android 11, 13.1.03.501 in Android 12 and 14.1.03.0 in Android 13 allows local attacker to get sensitive information of secret mode in Samsung Internet application with specific conditions. | 2023-03-16 | not yet calculated | CVE-2023-21463 MISC |
| samsung_mobile -- multiple_mobile_devices | Improper access control in Samsung Calendar prior to versions 12.4.02.9000 in Android 13 and 12.3.08.2000 in Android 12 allows local attacker to configure improper status. | 2023-03-16 | not yet calculated | CVE-2023-21464 MISC |
| samsung_mobile -- bixby_touch | Improper access control vulnerability in BixbyTouch prior to version 3.2.02.5 in China models allows untrusted applications access local files. | 2023-03-16 | not yet calculated | CVE-2023-21465 MISC |
| zoom_video_communications -- multiple_products | Zoom for Windows clients before version 5.13.3, Zoom Rooms for Windows clients before version 5.13.5 and Zoom VDI for Windows clients before 5.13.1 contain an information disclosure vulnerability. A recent update to the Microsoft Edge WebView2 runtime used by the affected Zoom clients, transmitted text to Microsoft’s online Spellcheck service instead of the local Windows Spellcheck. Updating Zoom remediates this vulnerability by disabling the feature. Updating Microsoft Edge WebView2 Runtime to at least version 109.0.1481.0 and restarting Zoom remediates this vulnerability by updating Microsoft’s telemetry behavior. | 2023-03-16 | not yet calculated | CVE-2023-22880 MISC |
| zoom_video_communications -- zoom | Zoom clients before version 5.13.5 contain a STUN parsing vulnerability. A malicious actor could send specially crafted UDP traffic to a victim Zoom client to remotely cause the client to crash, causing a denial of service. | 2023-03-16 | not yet calculated | CVE-2023-22881 MISC |
| zoom_video_communications -- zoom | Zoom clients before version 5.13.5 contain a STUN parsing vulnerability. A malicious actor could send specially crafted UDP traffic to a victim Zoom client to remotely cause the client to crash, causing a denial of service. | 2023-03-16 | not yet calculated | CVE-2023-22882 MISC |
| zoom_video_communications -- zoom | Zoom Client for IT Admin Windows installers before version 5.13.5 contain a local privilege escalation vulnerability. A local low-privileged user could exploit this vulnerability in an attack chain during the installation process to escalate their privileges to the SYSTEM user. | 2023-03-16 | not yet calculated | CVE-2023-22883 MISC |
| seamax -- sa-wr915nd | SA-WR915ND router firmware v17.35.1 was discovered to be vulnerable to code execution. | 2023-03-16 | not yet calculated | CVE-2023-23150 MISC MISC |
| discourse -- discourse | Discourse is an open-source discussion platform. Prior to version 3.0.1 of the stable branch and version 3.1.0.beta2 of the beta and tests-passed branches, the count of topics displayed for a tag is a count of all regular topics regardless of whether the topic is in a read restricted category or not. As a result, any users can technically poll a sensitive tag to determine if a new topic is created in a category which the user does not have excess to. In version 3.0.1 of the stable branch and version 3.1.0.beta2 of the beta and tests-passed branches, the count of topics displayed for a tag defaults to only counting regular topics which are not in read restricted categories. Staff users will continue to see a count of all topics regardless of the topic's category read restrictions. |
2023-03-17 | not yet calculated | CVE-2023-23622 MISC MISC MISC MISC MISC |
| discourse -- discourse | Discourse is an open-source messaging platform. In versions 3.0.1 and prior on the stable branch and versions 3.1.0.beta2 and prior on the beta and tests-passed branches, the count of personal messages displayed for a tag is a count of all personal messages regardless of whether the personal message is visible to a given user. As a result, any users can technically poll a sensitive tag to determine if a new personal message is created even if the user does not have access to the personal message. In the patched versions, the count of personal messages tagged with a given tag is hidden by default. To revert to the old behaviour of displaying the count of personal messages for a given tag, an admin may enable the display_personal_messages_tag_counts site setting. |
2023-03-16 | not yet calculated | CVE-2023-23935 MISC MISC |
| census -- squidex | Squidex before 7.4.0 was discovered to contain a squid.svg cross-site scripting (XSS) vulnerability. | 2023-03-18 | not yet calculated | CVE-2023-24278 MISC MISC |
| temenos -- t24 | Incorrect access control in Temenos T24 Release 20 allows attackers to gain unauthorized access to sensitive information via a crafted POST request to HELPTEXT.MAINMENU. | 2023-03-13 | not yet calculated | CVE-2023-24368 MISC |
| dell -- bios | Dell BIOS contains an Improper Input Validation vulnerability. A local authenticated malicious user with administrator privileges could potentially exploit this vulnerability to perform arbitrary code execution. | 2023-03-16 | not yet calculated | CVE-2023-24571 MISC |
| mcafee -- total_protection | McAfee Total Protection prior to 16.0.50 allows attackers to elevate user privileges due to Improper Link Resolution via registry keys. This could enable a user with lower privileges to execute unauthorized tasks. | 2023-03-13 | not yet calculated | CVE-2023-24577 MISC MISC |
| mcafee -- total_protection | McAfee Total Protection prior to 16.0.49 allows attackers to elevate user privileges due to DLL sideloading. This could enable a user with lower privileges to execute unauthorized tasks. | 2023-03-13 | not yet calculated | CVE-2023-24578 MISC MISC |
| mcafee -- total_protection | McAfee Total Protection prior to 16.0.51 allows attackers to trick a victim into uninstalling the application via the command prompt. | 2023-03-13 | not yet calculated | CVE-2023-24579 MISC MISC |
| vx_search -- vx_search | VX Search v13.8 and v14.7 was discovered to contain an unquoted service path vulnerability which allows attackers to execute arbitrary commands at elevated privileges via a crafted executable file. | 2023-03-16 | not yet calculated | CVE-2023-24671 MISC MISC |
| centralite -- pearl_thermostat | A vulnerability in Centralite Pearl Thermostat 0x04075010 allows attackers to cause a Denial of Service (DoS) via a crafted Zigbee message. | 2023-03-17 | not yet calculated | CVE-2023-24678 MISC MISC |
| ofcms -- ofcms | An issue found in Ofcms v.1.1.4 allows a remote attacker to to escalate privileges via the respwd method in SysUserController. | 2023-03-16 | not yet calculated | CVE-2023-24760 MISC MISC |
| jcg-cn -- jhr-n916r | Command execution vulnerability was discovered in JHR-N916R router firmware version<=21.11.1.1483. | 2023-03-16 | not yet calculated | CVE-2023-24795 MISC |
| prestashop -- prestashop | PrestaShop is an open source e-commerce web application that, prior to version 8.0.1, is vulnerable to cross-site request forgery (CSRF). When authenticating users, PrestaShop preserves session attributes. Because this does not clear CSRF tokens upon login, this might enable same-site attackers to bypass the CSRF protection mechanism by performing an attack similar to a session-fixation. The problem is fixed in version 8.0.1. | 2023-03-13 | not yet calculated | CVE-2023-25170 MISC |
| discourse -- discourse | Discourse is an open-source discussion platform. Prior to version 3.0.1 of the stable branch and version 3.1.0.beta2 of the beta and tests-passed branches, a maliciously crafted URL can be included in a user's full name field to to carry out cross-site scripting attacks on sites with a disabled or overly permissive CSP (Content Security Policy). Discourse's default CSP prevents this vulnerability. The vulnerability is patched in version 3.0.1 of the stable branch and version 3.1.0.beta2 of the beta and tests-passed branches. As a workaround, enable and/or restore your site's CSP to the default one provided with Discourse. |
2023-03-17 | not yet calculated | CVE-2023-25172 MISC MISC MISC MISC MISC |
| gfi -- kerio_connect | An issue was discovered in GFI Kerio Connect 9.4.1 patch 1 (fixed in 10.0.0). There is a stack-based Buffer Overflow in the webmail component's 2FASetup function via an authenticated request with a long primaryEMailAddress field to the webmail/api/jsonrpc URI. | 2023-03-15 | not yet calculated | CVE-2023-25267 MISC MISC |
| d-link -- dir820la1_fw105b03 | OS Command injection vulnerability in D-Link DIR820LA1_FW105B03 allows attackers to escalate privileges to root via a crafted payload with the ping_addr parameter to ping.ccp. | 2023-03-16 | not yet calculated | CVE-2023-25280 MISC MISC |
| d-link -- dir820la1_fw105b03 | A stack overflow vulnerability exists in pingV4Msg component in D-Link DIR820LA1_FW105B03, allows attackers to cause a denial of service via the nextPage parameter to ping.ccp. | 2023-03-16 | not yet calculated | CVE-2023-25281 MISC MISC |
| roxy-wi -- roxy-wi | Roxy-WI is a Web interface for managing Haproxy, Nginx, Apache, and Keepalived servers. Versions prior to 6.3.6.0 don't correctly neutralize dir/../filename sequences, such as /etc/nginx/../passwd, allowing an actor to gain information about a server. Version 6.3.6.0 has a patch for this issue. |
2023-03-13 | not yet calculated | CVE-2023-25802 MISC MISC |
| roxy-wi -- roxy-wi | Roxy-WI is a Web interface for managing Haproxy, Nginx, Apache, and Keepalived servers. Versions prior to 6.3.5.0 have a directory traversal vulnerability that allows the inclusion of server-side files. This issue is fixed in version 6.3.5.0. | 2023-03-13 | not yet calculated | CVE-2023-25803 MISC |
| discourse -- discourse | Discourse is an open-source discussion platform. Between versions 3.1.0.beta2 and 3.1.0.beta3 of the tests-passed branch, editing or responding to a chat message containing malicious content could lead to a cross-site scripting attack. This issue is patched in version 3.1.0.beta3 of the tests-passed branch. There are no known workarounds. |
2023-03-17 | not yet calculated | CVE-2023-26040 MISC MISC |
| arm-software -- aarch64cryptolib | The armv8_dec_aes_gcm_full() API of Arm AArch64cryptolib before 86065c6 fails to the verify the authentication tag of AES-GCM protected data, leading to a man-in-the-middle attack. This occurs because of an improperly initialized variable. | 2023-03-15 | not yet calculated | CVE-2023-26084 MISC |
| collection.js -- collection.js | Versions of the package collection.js before 6.8.1 are vulnerable to Prototype Pollution via the extend function in Collection.js/dist/node/iterators/extend.js. | 2023-03-18 | not yet calculated | CVE-2023-26113 MISC MISC MISC MISC MISC |
| sitecore_xp/xm -- sitecore_xp/xm | An issue was discovered in Sitecore XP/XM 10.3. As an authenticated Sitecore user, a unrestricted language file upload vulnerability exists the can lead to direct code execution on the content management (CM) server. | 2023-03-14 | not yet calculated | CVE-2023-26262 MISC MISC |
| sap_se -- netweaver_as for abap and abap_platform | Due to improper input controls In SAP NetWeaver AS for ABAP and ABAP Platform - versions 700, 701, 702, 731, 740, 750, 751, 752, 753, 754, 755, 756, 757, 791, an attacker authenticated as a non-administrative user can craft a request which will trigger the application server to send a request to an arbitrary URL which can reveal, modify or make unavailable non-sensitive information, leading to low impact on Confidentiality, Integrity and Availability. | 2023-03-14 | not yet calculated | CVE-2023-26459 MISC MISC |
| sap_se -- netweaver_application_server_for_java | Cache Management Service in SAP NetWeaver Application Server for Java - version 7.50, does not perform any authentication checks for functionalities that require user identity | 2023-03-14 | not yet calculated | CVE-2023-26460 MISC MISC |
| sap_se -- netweaver | SAP NetWeaver allows (SAP Enterprise Portal) - version 7.50, allows an authenticated attacker with sufficient privileges to access the XML parser which can submit a crafted XML file which when parsed will enable them to access but not modify sensitive files and data. It allows the attacker to view sensitive data which is owned by certain privileges. | 2023-03-14 | not yet calculated | CVE-2023-26461 MISC MISC |
| kubevirt -- kubevirt | KubeVirt is a virtual machine management add-on for Kubernetes. In versions 0.59.0 and prior, if a malicious user has taken over a Kubernetes node where virt-handler (the KubeVirt node-daemon) is running, the virt-handler service account can be used to modify all node specs. This can be misused to lure-in system-level-privileged components which can, for instance, read all secrets on the cluster, or can exec into pods on other nodes. This way, a compromised node can be used to elevate privileges beyond the node until potentially having full privileged access to the whole cluster. The simplest way to exploit this, once a user could compromise a specific node, is to set with the virt-handler service account all other nodes to unschedulable and simply wait until system-critical components with high privileges appear on its node. No patches are available as of time of publication. As a workaround, gatekeeper users can add a webhook which will block the virt-handler service account to modify the spec of a node. |
2023-03-15 | not yet calculated | CVE-2023-26484 MISC MISC |
| propius_machineselector -- propius_machineselector | A Hard Coded Admin Credentials issue in the Web-UI Admin Panel in Propius MachineSelector 6.6.0 and 6.6.1 allows remote attackers to gain access to the admin panel Propiusadmin.php, which allows taking control of the affected system. | 2023-03-14 | not yet calculated | CVE-2023-26511 MISC |
| liblouis -- liblouis | Buffer Overflow vulnerability found in Liblouis v.3.24.0 allows a remote attacker to cause a denial of service via the lou_logFile function at logginc.c endpoint. | 2023-03-16 | not yet calculated | CVE-2023-26767 MISC MISC |
| liblouis -- liblouis | Buffer Overflow vulnerability found in Liblouis v.3.24.0 allows a remote attacker to cause a denial of service via the compileTranslationTable.c and lou_setDataPath functions. | 2023-03-16 | not yet calculated | CVE-2023-26768 MISC MISC |
| liblouis -- liblouis | Buffer Overflow vulnerability found in Liblouis Lou_Trace v.3.24.0 allows a remote attacker to cause a denial of service via the resolveSubtable function at compileTranslationTabel.c. | 2023-03-16 | not yet calculated | CVE-2023-26769 MISC MISC MISC |
| kirin -- fortress_machine | SQL Injection vulnerability found in Kirin Fortress Machine v.1.7-2020-0610 allows attackers to execute arbitrary code via the /admin.php?controller=admin_commonuser parameter. | 2023-03-16 | not yet calculated | CVE-2023-26784 MISC MISC |
| onekeyadmin -- onekeyadmin | onekeyadmin v1.3.9 was discovered to contain a stored cross-site scripting (XSS) vulnerability via the Member List module. | 2023-03-16 | not yet calculated | CVE-2023-26951 MISC |
| wondershare_dr.fone -- wondershare_dr.fone | Wondershare Dr.Fone v12.9.6 was discovered to contain weak permissions for the service WsDrvInst. This vulnerability allows attackers to escalate privileges via modifying or overwriting the executable. | 2023-03-13 | not yet calculated | CVE-2023-27010 MISC MISC |
| qibosoft -- qibocms | Qibosoft QiboCMS v7 was discovered to contain a remote code execution (RCE) vulnerability via the Get_Title function at label_set_rs.php | 2023-03-16 | not yet calculated | CVE-2023-27037 MISC |
| simple_image_gallery -- simple_image_gallery | Simple Image Gallery v1.0 was discovered to contain a remote code execution (RCE) vulnerability via the username parameter. | 2023-03-16 | not yet calculated | CVE-2023-27040 MISC |
| school_registration_and_fee_system -- school_registration_and_fee_system | School Registration and Fee System v1.0 was discovered to contain a SQL injection vulnerability via the id parameter at/bilal final/edit_user.php. | 2023-03-16 | not yet calculated | CVE-2023-27041 MISC |
| churchcrm -- churchcrm | A cross-site scripting (XSS) vulnerability in the Edit Group function of ChurchCRM v4.5.3 allows attackers to execute arbitrary web scripts or HTML via a crafted payload injected into the Edit Group Name text field. | 2023-03-16 | not yet calculated | CVE-2023-27059 MISC |
| dreamer_cms -- dreamer_cms | Permissions vulnerability found in isoftforce Dreamer CMS v.4.0.1 allows local attackers to obtain sensitive information via the AttachmentController parameter. | 2023-03-16 | not yet calculated | CVE-2023-27084 MISC MISC |
| hippo4j -- hippo4j | Insecure Permissions vulnerability found in OpenGoofy Hippo4j v.1.4.3 allows attacker toescalate privileges via the AddUser method of the UserController function in Tenant Management module. | 2023-03-16 | not yet calculated | CVE-2023-27095 MISC |
| libde265 -- libde265 | Libde265 v1.0.11 was discovered to contain a segmentation violation via the function decoder_context::process_slice_segment_header at decctx.cc. | 2023-03-15 | not yet calculated | CVE-2023-27102 MISC |
| typecho -- typecho | Cross Site Scripting vulnerability found in Typecho v.1.2.0 allows a remote attacker to execute arbitrary code via an arbitrarily supplied URL parameter. | 2023-03-16 | not yet calculated | CVE-2023-27130 MISC MISC |
| typecho -- typecho | Cross Site Scripting vulnerability found in Typecho v.1.2.0 allows a remote attacker to execute arbitrary code viathe Post Editorparameter. | 2023-03-16 | not yet calculated | CVE-2023-27131 MISC |
| jizhicms -- jizhicms | A Cross-Site Request Forgery (CSRF) in /Sys/index.html of Jizhicms v2.4.5 allows attackers to arbitrarily make configuration changes within the application. | 2023-03-15 | not yet calculated | CVE-2023-27234 MISC |
| tenda -- ax3 | Tenda AX3 V16.03.12.11 was discovered to contain a stack overflow via the shareSpeed parameter at /goform/WifiGuestSet. | 2023-03-15 | not yet calculated | CVE-2023-27239 MISC |
| tenda -- ax3 | Tenda AX3 V16.03.12.11 was discovered to contain a command injection vulnerability via the lanip parameter at /goform/AdvSetLanip. | 2023-03-15 | not yet calculated | CVE-2023-27240 MISC |
| online_book_store_project -- online_book_store_project | Online Book Store Project v1.0 is vulnerable to SQL Injection via /bookstore/bookPerPub.php. | 2023-03-16 | not yet calculated | CVE-2023-27250 MISC |
| netgate -- pfsense | A command injection vulnerability in the function restore_rrddata() of Netgate pfSense v2.7.0 allows authenticated attackers to execute arbitrary commands via manipulating the contents of an XML file supplied to the component config.xml. | 2023-03-17 | not yet calculated | CVE-2023-27253 MISC MISC |
| sap -- netweaver_as_java | SAP NetWeaver AS Java (Object Analyzing Service) - version 7.50, does not perform necessary authorization checks, allowing an unauthenticated attacker to attach to an open interface and make use of an open naming and directory API to access a service which will enable them to access but not modify server settings and data with no effect on availability., resulting in escalation of privileges. | 2023-03-14 | not yet calculated | CVE-2023-27268 MISC MISC |
| sap -- netweaver_application_server | SAP NetWeaver Application Server for ABAP and ABAP Platform - versions 700, 701, 702, 731, 740, 750, 751, 752, 753, 754, 755, 756, 757, 791, allows an attacker with non-administrative authorizations to exploit a directory traversal flaw in an available service to overwrite the system files. In this attack, no data can be read but potentially critical OS files can be overwritten making the system unavailable. | 2023-03-14 | not yet calculated | CVE-2023-27269 MISC MISC |
| sap -- netweaver_application_server | SAP NetWeaver Application Server for ABAP and ABAP Platform - versions 700, 701, 702, 731, 740, 750, 751, 752, 753, 754, 755, 756, 757, 791, has multiple vulnerabilities in a class for test purposes in which an attacker authenticated as a non-administrative user can craft a request with certain parameters, which will consume the server's resources sufficiently to make it unavailable. There is no ability to view or modify any information. | 2023-03-14 | not yet calculated | CVE-2023-27270 MISC MISC |
| sap -- businessobjects_business_intelligence_platform | In SAP BusinessObjects Business Intelligence Platform (Web Services) - versions 420, 430, an attacker can control a malicious BOE server, forcing the application server to connect to its own admintools, leading to a high impact on availability. | 2023-03-14 | not yet calculated | CVE-2023-27271 MISC MISC |
| streamlit -- streamlit | Streamlit, software for turning data scripts into web applications, had a cross-site scripting (XSS) vulnerability in versions 0.63.0 through 0.80.0. Users of hosted Streamlit app(s) were vulnerable to a reflected XSS vulnerability. An attacker could craft a malicious URL with Javascript payloads to a Streamlit app. The attacker could then trick the user into visiting the malicious URL and, if successful, the server would render the malicious javascript payload as-is, leading to XSS. Version 0.81.0 contains a patch for this vulnerability. | 2023-03-16 | not yet calculated | CVE-2023-27494 MISC MISC |
| sap -- host_agent | SAP Host Agent (SAPOSCOL) - version 7.22, allows an unauthenticated attacker with network access to a server port assigned to the SAP Start Service to submit a crafted request which results in a memory corruption error. This error can be used to reveal but not modify any technical information about the server. It can also make a particular service temporarily unavailable | 2023-03-14 | not yet calculated | CVE-2023-27498 MISC MISC |
| sap -- saprsbro | An attacker with non-administrative authorizations can exploit a directory traversal flaw in program SAPRSBRO to over-write system files. In this attack, no data can be read but potentially critical OS files can be over-written making the system unavailable. | 2023-03-14 | not yet calculated | CVE-2023-27500 MISC MISC |
| codeigniter -- shield | CodeIgniter Shield provides authentication and authorization for the CodeIgniter 4 PHP framework. An improper implementation was found in the password storage process. All hashed passwords stored in Shield v1.0.0-beta.3 or earlier are easier to crack than expected due to the vulnerability. Therefore, they should be removed as soon as possible. If an attacker gets (1) the user's hashed password by Shield, and (2) the hashed password (SHA-384 hash without salt) from somewhere, the attacker may easily crack the user's password. Upgrade to Shield v1.0.0-beta.4 or later to fix this issue. After upgrading, all users’ hashed passwords should be updated (saved to the database). There are no known workarounds. | 2023-03-13 | not yet calculated | CVE-2023-27580 MISC MISC MISC MISC MISC MISC |
| pjsip -- pjsip | PJSIP is a free and open source multimedia communication library written in C. A buffer overflow vulnerability in versions 2.13 and prior affects applications that use PJSIP DNS resolver. It doesn't affect PJSIP users who do not utilise PJSIP DNS resolver. This vulnerability is related to CVE-2022-24793. A patch is available as commit d1c5e4d in the master branch. A workaround is to disable DNS resolution in PJSIP config (by setting nameserver_count to zero) or use an external resolver implementation instead. |
2023-03-14 | not yet calculated | CVE-2023-27585 MISC MISC MISC MISC |
| hasura -- graphql_engine | Hasura is an open-source product that provides users GraphQL or REST APIs. A path traversal vulnerability has been discovered within Hasura GraphQL Engine prior to versions 1.3.4, 2.55.1, 2.20.1, and 2.21.0-beta1. Projects running on Hasura Cloud were not vulnerable. Self-hosted Hasura Projects with deployments that are publicly exposed and not protected by a WAF or other HTTP protection layer should be upgraded to version 1.3.4, 2.55.1, 2.20.1, or 2.21.0-beta1 to receive a patch. | 2023-03-14 | not yet calculated | CVE-2023-27588 MISC MISC MISC MISC MISC MISC |
| minio -- minio | Minio is a Multi-Cloud Object Storage framework. Starting with RELEASE.2020-12-23T02-24-12Z and prior to RELEASE.2023-03-13T19-46-17Z, a user with consoleAdmin permissions can potentially create a user that matches the root credential accessKey. Once this user is created successfully, the root credential ceases to work appropriately. The issue is patched in RELEASE.2023-03-13T19-46-17Z. There are ways to work around this via adding higher privileges to the disabled root user via mc admin policy set. |
2023-03-14 | not yet calculated | CVE-2023-27589 MISC MISC |
| rizin -- rizin | Rizin is a UNIX-like reverse engineering framework and command-line toolset. In version 0.5.1 and prior, converting a GDB registers profile file into a Rizin register profile can result in a stack-based buffer overflow when the name, type, or groups fields have longer values than expected. Users opening untrusted GDB registers files (e.g. with the drpg or arpg commands) are affected by this flaw. Commit d6196703d89c84467b600ba2692534579dc25ed4 contains a patch for this issue. As a workaround, review the GDB register profiles before loading them with drpg/arpg commands. |
2023-03-14 | not yet calculated | CVE-2023-27590 MISC MISC MISC MISC MISC |
| miniflux -- miniflux | Miniflux is a feed reader. Prior to version 2.0.43, an unauthenticated user can retrieve Prometheus metrics from a publicly reachable Miniflux instance where the METRICS_COLLECTOR configuration option is enabled and METRICS_ALLOWED_NETWORKS is set to 127.0.0.1/8 (the default). A patch is available in Miniflux 2.0.43. As a workaround, set METRICS_COLLECTOR to false (default) or run Miniflux behind a trusted reverse-proxy. |
2023-03-17 | not yet calculated | CVE-2023-27591 MISC MISC MISC MISC |
| miniflux -- miniflux | Miniflux is a feed reader. Since v2.0.25, Miniflux will automatically proxy images served over HTTP to prevent mixed content errors. When an outbound request made by the Go HTTP client fails, the html.ServerError is returned unescaped without the expected Content Security Policy header added to valid responses. By creating an RSS feed item with the inline description containing an <img> tag with a srcset attribute pointing to an invalid URL like http:a<script>alert(1)</script>, we can coerce the proxy handler into an error condition where the invalid URL is returned unescaped and in full. This results in JavaScript execution on the Miniflux instance as soon as the user is convinced (e.g. by a message in the alt text) to open the broken image. An attacker can execute arbitrary JavaScript in the context of a victim Miniflux user when they open a broken image in a crafted RSS feed. This can be used to perform actions on the Miniflux instance as that user and gain administrative access to the Miniflux instance if it is reachable and the victim is an administrator. A patch is available in version 2.0.43. As a workaround sisable image proxy; default value is http-only. |
2023-03-17 | not yet calculated | CVE-2023-27592 MISC MISC MISC MISC MISC MISC MISC |
| cilium -- cilium | Cilium is a networking, observability, and security solution with an eBPF-based dataplane. Prior to versions 1.11.15, 1.12.8, and 1.13.1, an attacker with access to a Cilium agent pod can write to /opt/cni/bin due to a hostPath mount of that directory in the agent pod. By replacing the CNI binary with their own malicious binary and waiting for the creation of a new pod on the node, the attacker can gain access to the underlying node. The issue has been fixed and the fix is available on versions 1.11.15, 1.12.8, and 1.13.1. Some workarounds are available. Kubernetes RBAC should be used to deny users and service accounts exec access to Cilium agent pods. In cases where a user requires exec access to Cilium agent pods, but should not have access to the underlying node, no workaround is possible. |
2023-03-17 | not yet calculated | CVE-2023-27593 MISC MISC MISC MISC MISC MISC |
| cilium -- cilium | Cilium is a networking, observability, and security solution with an eBPF-based dataplane. Prior to versions 1.11.15, 1.12.8, and 1.13.1, under specific conditions, Cilium may misattribute the source IP address of traffic to a cluster, identifying external traffic as coming from the host on which Cilium is running. As a consequence, network policies for that cluster might be bypassed, depending on the specific network policies enabled. This issue only manifests when Cilium is routing IPv6 traffic and NodePorts are used to route traffic to pods. IPv6 and endpoint routes are both disabled by default. The problem has been fixed and is available on versions 1.11.15, 1.12.8, and 1.13.1. As a workaround, disable IPv6 routing. | 2023-03-17 | not yet calculated | CVE-2023-27594 MISC MISC MISC MISC |
| cilium -- cilium | Cilium is a networking, observability, and security solution with an eBPF-based dataplane. In version 1.13.0, when Cilium is started, there is a short period when Cilium eBPF programs are not attached to the host. During this period, the host does not implement any of Cilium's featureset. This can cause disruption to newly established connections during this period due to the lack of Load Balancing, or can cause Network Policy bypass due to the lack of Network Policy enforcement during the window. This vulnerability impacts any Cilium-managed endpoints on the node (such as Kubernetes Pods), as well as the host network namespace (including Host Firewall). This vulnerability is fixed in Cilium 1.13.1 or later. Cilium releases 1.12.x, 1.11.x, and earlier are not affected. There are no known workarounds. | 2023-03-17 | not yet calculated | CVE-2023-27595 MISC MISC MISC |
| opensips -- opensips | OpenSIPS is a Session Initiation Protocol (SIP) server implementation. Prior to versions 3.1.8 and 3.2.5, OpenSIPS crashes when a malformed SDP body is sent multiple times to an OpenSIPS configuration that makes use of the stream_process function. This issue was discovered during coverage guided fuzzing of the function codec_delete_except_re. By abusing this vulnerability, an attacker is able to crash the server. It affects configurations containing functions that rely on the affected code, such as the function codec_delete_except_re. This issue has been fixed in version 3.1.8 and 3.2.5. |
2023-03-15 | not yet calculated | CVE-2023-27596 MISC MISC |
| opensips -- opensips | OpenSIPS is a Session Initiation Protocol (SIP) server implementation. Prior to versions 3.1.8 and 3.2.5, when a specially crafted SIP message is processed by the function rewrite_ruri, a crash occurs due to a segmentation fault. This issue causes the server to crash. It affects configurations containing functions that make use of the affected code, such as the function setport. This issue has been fixed in version 3.1.8 and 3.2.5. |
2023-03-15 | not yet calculated | CVE-2023-27597 MISC MISC |
| opensips -- opensips | OpenSIPS is a Session Initiation Protocol (SIP) server implementation. Prior to versions 3.1.7 and 3.2.4, sending a malformed Via header to OpenSIPS triggers a segmentation fault when the function calc_tag_suffix is called. A specially crafted Via header, which is deemed correct by the parser, will pass uninitialized strings to the function MD5StringArray which leads to the crash. Abuse of this vulnerability leads to Denial of Service due to a crash. Since the uninitialized string points to memory location 0x0, no further exploitation appears to be possible. No special network privileges are required to perform this attack, as long as the OpenSIPS configuration makes use of functions such as sl_send_reply or sl_gen_totag that trigger the vulnerable code. This issue has been fixed in versions 3.1.7 and 3.2.4. |
2023-03-15 | not yet calculated | CVE-2023-27598 MISC MISC MISC |
| opensips -- opensips | OpenSIPS is a Session Initiation Protocol (SIP) server implementation. Prior to versions 3.1.7 and 3.2.4, when the function append_hf handles a SIP message with a malformed To header, a call to the function abort() is performed, resulting in a crash. This is due to the following check in data_lump.c:399 in the function anchor_lump. An attacker abusing this vulnerability will crash OpenSIPS leading to Denial of Service. It affects configurations containing functions that make use of the affected code, such as the function append_hf. This issue has been fixed in versions 3.1.7 and 3.2.4. |
2023-03-15 | not yet calculated | CVE-2023-27599 MISC MISC MISC |
| opensips -- opensips | OpenSIPS is a Session Initiation Protocol (SIP) server implementation. Prior to versions 3.1.7 and 3.2.4, OpenSIPS crashes when a malformed SDP body is received and is processed by the delete_sdp_line function in the sipmsgops module. This issue can be reproduced by calling the function with an SDP body that does not terminate by a line feed (i.e. \n). The vulnerability was found while performing black-box fuzzing against an OpenSIPS server running a configuration that made use of the functions codec_delete_except_re and codec_delete_re. The same issue was also discovered while performing coverage guided fuzzing on the function codec_delete_except_re. The crash happens because the function delete_sdp_line expects that an SDP line is terminated by a line feed (\n). By abusing this vulnerability, an attacker is able to crash the server. It affects configurations containing functions that rely on the affected code, such as the function codec_delete_except_re. Due to the sanity check that is performed in the del_lump function, exploitation of this issue will generate an abort in the lumps processing function, resulting in a Denial of Service. This issue is patched in versions 3.1.7 and 3.2.4. |
2023-03-15 | not yet calculated | CVE-2023-27600 MISC MISC MISC MISC |
| opensips -- opensips | OpenSIPS is a Session Initiation Protocol (SIP) server implementation. Prior to versions 3.1.7 and 3.2.4, OpenSIPS crashes when a malformed SDP body is received and is processed by the delete_sdp_line function in the sipmsgops module. This issue can be reproduced by calling the function with an SDP body that does not terminate by a line feed (i.e. \n). The vulnerability was found while performing black-box fuzzing against an OpenSIPS server running a configuration that made use of the functions codec_delete_except_re and codec_delete_re. The same issue was also discovered while performing coverage guided fuzzing on the function codec_delete_except_re. The crash happens because the function delete_sdp_line expects that an SDP line is terminated by a line feed (\n): By abusing this vulnerability, an attacker is able to crash the server. It affects configurations containing functions that rely on the affected code, such as the function codec_delete_except_re. Due to the sanity check that is performed in the del_lump function, exploitation of this issue will generate an abort in the lumps processing function, resulting in a Denial of Service. This issue has been fixed in versions 3.1.7 and 3.2.4. |
2023-03-15 | not yet calculated | CVE-2023-27601 MISC MISC MISC MISC |
| dedecms -- dedecms | SQL injection vulnerability found in DedeCMS v.5.7.106 allows a remote attacker to execute arbitrary code via the rank_* parameter in the /dede/group_store.php endpoint. | 2023-03-16 | not yet calculated | CVE-2023-27707 MISC |
| dedecms -- dedecms | SQL injection vulnerability found in DedeCMS v.5.7.106 allows a remote attacker to execute arbitrary code via the rank_* parameter in the /dedestory_catalog.php endpoint. | 2023-03-16 | not yet calculated | CVE-2023-27709 MISC |
| typecho -- typecho | Cross Site Scripting vulnerability found in Typecho v.1.2.0 allows a remote attacker to execute arbitrary code via the Comment Manager /admin/manage-comments.php component. | 2023-03-16 | not yet calculated | CVE-2023-27711 MISC MISC |
| tcpreplay -- tcprewrite | An issue found in TCPreplay tcprewrite v.4.4.3 allows a remote attacker to cause a denial of service via the tcpedit_dlt_cleanup function at plugins/dlt_plugins.c. | 2023-03-16 | not yet calculated | CVE-2023-27783 MISC MISC |
| tcpreplay -- tcpreplay | An issue found in TCPReplay v.4.4.3 allows a remote attacker to cause a denial of service via the read_hexstring function at the utils.c:309 endpoint. | 2023-03-16 | not yet calculated | CVE-2023-27784 MISC |
| tcpreplay -- tcpprep | An issue found in TCPreplay TCPprep v.4.4.3 allows a remote attacker to cause a denial of service via the parse endpoints function. | 2023-03-16 | not yet calculated | CVE-2023-27785 MISC |
| tcpprep -- tcpprep | An issue found in TCPprep v.4.4.3 allows a remote attacker to cause a denial of service via the macinstring function. | 2023-03-16 | not yet calculated | CVE-2023-27786 MISC MISC |
| tcpprep -- tcpprep | An issue found in TCPprep v.4.4.3 allows a remote attacker to cause a denial of service via the parse_list function at the list.c:81 endpoint. | 2023-03-16 | not yet calculated | CVE-2023-27787 MISC |
| tcpreplay -- tcprewrite | An issue found in TCPrewrite v.4.4.3 allows a remote attacker to cause a denial of service via the ports2PORT function at the portmap.c:69 endpoint. | 2023-03-16 | not yet calculated | CVE-2023-27788 MISC |
| tcpprep -- tcpprep | An issue found in TCPprep v.4.4.3 allows a remote attacker to cause a denial of service via the cidr2cidr function at the cidr.c:178 endpoint. | 2023-03-16 | not yet calculated | CVE-2023-27789 MISC MISC |
| ibm -- aspera_faspex | IBM Aspera Faspex 5.0.4 could allow an authenticated user to change other user's credentials due to improper access controls. IBM X-Force ID: 249847. | 2023-03-16 | not yet calculated | CVE-2023-27875 MISC MISC |
| sap -- solution_manager_and_abap_managed_systems | An attacker authenticated as a user with a non-administrative role and a common remote execution authorization in SAP Solution Manager and ABAP managed systems (ST-PI) - versions 2088_1_700, 2008_1_710, 740, can use a vulnerable interface to execute an application function to perform actions which they would not normally be permitted to perform. Depending on the function executed, the attack can read or modify any user or application data and can make the application unavailable. | 2023-03-14 | not yet calculated | CVE-2023-27893 MISC MISC |
| sap -- businessobjects_business_intelligence_platform | SAP BusinessObjects Business Intelligence Platform (Web Services) - versions 420, 430, allows an attacker to inject arbitrary values as CMS parameters to perform lookups on the internal network which is otherwise not accessible externally. On successful exploitation, attacker can scan internal network to determine internal infrastructure for further attacks like remote file inclusion, retrieve server files, bypass firewall and force the vulnerable server to execute malicious requests, resulting in sensitive information disclosure. This causes limited impact on confidentiality of data. | 2023-03-14 | not yet calculated | CVE-2023-27894 MISC MISC |
| sap -- authenticator_for_android | SAP Authenticator for Android - version 1.3.0, allows the screen to be captured, if an authorized attacker installs a malicious app on the mobile device. The attacker could extract the currently views of the OTP and the secret OTP alphanumeric token during the token setup. On successful exploitation, an attacker can read some sensitive information but cannot modify and delete the data. | 2023-03-14 | not yet calculated | CVE-2023-27895 MISC MISC |
| sap -- businessobjects_business_intelligence_platform | In SAP BusinessObjects Business Intelligence Platform - version 420, 430, an attacker can control a malicious BOE server, forcing the application server to connect to its own CMS, leading to a high impact on availability. | 2023-03-14 | not yet calculated | CVE-2023-27896 MISC MISC |
| opensips -- opensips | OpenSIPS is a Session Initiation Protocol (SIP) server implementation. Versions prior to 3.1.7 and 3.2.4 have a potential issue in msg_translator.c:2628 which might lead to a server crash. This issue was found while fuzzing the function build_res_buf_from_sip_req but could not be reproduced against a running instance of OpenSIPS. This issue could not be exploited against a running instance of OpenSIPS since no public function was found to make use of this vulnerable code. Even in the case of exploitation through unknown vectors, it is highly unlikely that this issue would lead to anything other than Denial of Service. This issue has been fixed in versions 3.1.7 and 3.2.4. |
2023-03-15 | not yet calculated | CVE-2023-28095 MISC MISC MISC |
| opensips -- opensips | OpenSIPS, a Session Initiation Protocol (SIP) server implementation, has a memory leak starting in the 2.3 branch and priot to versions 3.1.8 and 3.2.5. The memory leak was detected in the function parse_mi_request while performing coverage-guided fuzzing. This issue can be reproduced by sending multiple requests of the form {"jsonrpc": "2.0","method": "log_le. This malformed message was tested against an instance of OpenSIPS via FIFO transport layer and was found to increase the memory consumption over time. To abuse this memory leak, attackers need to reach the management interface (MI) which typically should only be exposed on trusted interfaces. In cases where the MI is exposed to the internet without authentication, abuse of this issue will lead to memory exhaustion which may affect the underlying system’s availability. No authentication is typically required to reproduce this issue. On the other hand, memory leaks may occur in other areas of OpenSIPS where the cJSON library is used for parsing JSON objects. The issue has been fixed in versions 3.1.8 and 3.2.5. |
2023-03-15 | not yet calculated | CVE-2023-28096 MISC MISC MISC |
| opensips -- opensips | OpenSIPS is a Session Initiation Protocol (SIP) server implementation. Prior to versions 3.1.9 and 3.2.6, a malformed SIP message containing a large Content-Length value and a specially crafted Request-URI causes a segmentation fault in OpenSIPS. This issue occurs when a large amount of shared memory using the -m flag was allocated to OpenSIPS, such as 10 GB of RAM. On the test system, this issue occurred when shared memory was set to 2362 or higher. This issue is fixed in versions 3.1.9 and 3.2.6. The only workaround is to guarantee that the Content-Length value of input messages is never larger than 2147483647. |
2023-03-15 | not yet calculated | CVE-2023-28097 MISC MISC MISC |
| opensips -- opensips | OpenSIPS is a Session Initiation Protocol (SIP) server implementation. Prior to versions 3.1.7 and 3.2.4, a specially crafted Authorization header causes OpenSIPS to crash or behave in an unexpected way due to a bug in the function parse_param_name() . This issue was discovered while performing coverage guided fuzzing of the function parse_msg. The AddressSanitizer identified that the issue occurred in the function q_memchr() which is being called by the function parse_param_name(). This issue may cause erratic program behaviour or a server crash. It affects configurations containing functions that make use of the affected code, such as the function www_authorize() . Versions 3.1.7 and 3.2.4 contain a fix. |
2023-03-15 | not yet calculated | CVE-2023-28098 MISC MISC MISC |
| opensips -- opensips | OpenSIPS is a Session Initiation Protocol (SIP) server implementation. Prior to versions 3.1.9 and 3.2.6, if ds_is_in_list() is used with an invalid IP address string (NULL is illegal input), OpenSIPS will attempt to print a string from a random address (stack garbage), which could lead to a crash. All users of ds_is_in_list() without the $si variable as 1st parameter could be affected by this vulnerability to a larger, lesser or no extent at all, depending if the data passed to the function is a valid IPv4 or IPv6 address string or not. Fixes will are available starting with the 3.1.9 and 3.2.6 minor releases. There are no known workarounds. |
2023-03-15 | not yet calculated | CVE-2023-28099 MISC MISC MISC |
| flatpak -- flatpak | Flatpak is a system for building, distributing, and running sandboxed desktop applications on Linux. Versions prior to 1.10.8, 1.12.8, 1.14.4, and 1.15.4 contain a vulnerability similar to CVE-2017-5226, but using the TIOCLINUX ioctl command instead of TIOCSTI. If a Flatpak app is run on a Linux virtual console such as /dev/tty1, it can copy text from the virtual console and paste it into the command buffer, from which the command might be run after the Flatpak app has exited. Ordinary graphical terminal emulators like xterm, gnome-terminal and Konsole are unaffected. This vulnerability is specific to the Linux virtual consoles /dev/tty1, /dev/tty2 and so on. A patch is available in versions 1.10.8, 1.12.8, 1.14.4, and 1.15.4. As a workaround, don't run Flatpak on a Linux virtual console. Flatpak is primarily designed to be used in a Wayland or X11 graphical environment. |
2023-03-16 | not yet calculated | CVE-2023-28100 MISC MISC MISC |
| flatpak -- flatpak | Flatpak is a system for building, distributing, and running sandboxed desktop applications on Linux. In versions prior to 1.10.8, 1.12.8, 1.14.4, and 1.15.4, if an attacker publishes a Flatpak app with elevated permissions, they can hide those permissions from users of the flatpak(1) command-line interface by setting other permissions to crafted values that contain non-printable control characters such as ESC. A fix is available in versions 1.10.8, 1.12.8, 1.14.4, and 1.15.4. As a workaround, use a GUI like GNOME Software rather than the command-line interface, or only install apps whose maintainers you trust. |
2023-03-16 | not yet calculated | CVE-2023-28101 MISC MISC MISC MISC |
| silverstripe -- silverstripe_graphql | silverstripe/graphql serves Silverstripe data as GraphQL representations. In versions 4.2.2 and 4.1.1, an attacker could use a specially crafted graphql query to execute a denial of service attack against a website which has a publicly exposed graphql endpoint. This mostly affects websites with particularly large/complex graphql schemas. Users should upgrade to silverstripe/graphql 4.2.3 or 4.1.2 to remedy the vulnerability. |
2023-03-16 | not yet calculated | CVE-2023-28104 MISC MISC MISC MISC |
| go-used-util -- go-used-util | go-used-util has commonly used utility functions for Go. Versions prior to 0.0.34 have a ZipSlip issue when using fsutil package to unzip files. When users use zip.Unzip to unzip zip files from a malicious attacker, they may be vulnerable to path traversal. The issue has been fixed in version 0.0.34. There are no known workarounds. |
2023-03-16 | not yet calculated | CVE-2023-28105 MISC MISC |
| pimcore -- pimcore | Pimcore is an open source data and experience management platform. Prior to version 10.5.19, an attacker can use cross-site scripting to send a malicious script to an unsuspecting user. Users may upgrade to version 10.5.19 to receive a patch or, as a workaround, apply the patch manually. | 2023-03-16 | not yet calculated | CVE-2023-28106 MISC MISC MISC MISC |
| discourse -- discourse | Discourse is an open-source discussion platform. Prior to version 3.0.2 of the stable branch and version 3.1.0.beta3 of the beta and tests-passed branches, a user logged as an administrator can request backups multiple times, which will eat up all the connections to the DB. If this is done on a site using multisite, then it can affect the whole cluster. The vulnerability is patched in version 3.0.2 of the stable branch and version 3.1.0.beta3 of the beta and tests-passed branches. There are no known workarounds. |
2023-03-17 | not yet calculated | CVE-2023-28107 MISC MISC MISC MISC MISC |
| pimcore -- pimcore | Pimcore is an open source data and experience management platform. Prior to version 10.5.19, quoting is not done properly in UUID DAO model. There is the theoretical possibility to inject custom SQL if the developer is using this methods with input data and not doing proper input validation in advance and so relies on the auto-quoting being done by the DAO class. Users should update to version 10.5.19 to receive a patch or, as a workaround, apply the patch manually. | 2023-03-16 | not yet calculated | CVE-2023-28108 MISC MISC MISC |
| docker -- docker | Play With Docker is a browser-based Docker playground. Versions 0.0.2 and prior are vulnerable to domain hijacking. Because CORS configuration was not correct, an attacker could use play-with-docker.com as an example and set the origin header in an http request as evil-play-with-docker.com. The domain would echo in response header, which successfully bypassed the CORS policy and retrieved basic user information. This issue has been fixed in commit ed82247c9ab7990ad76ec2bf1498c2b2830b6f1a. There are no known workarounds. |
2023-03-16 | not yet calculated | CVE-2023-28109 MISC MISC |
| jumpserver -- jumpserver | Jumpserver is a popular open source bastion host, and Koko is a Jumpserver component that is the Go version of coco, refactoring coco's SSH/SFTP service and Web Terminal service. Prior to version 2.28.8, using illegal tokens to connect to a Kubernetes cluster through Koko can result in the execution of dangerous commands that may disrupt the Koko container environment and affect normal usage. The vulnerability has been fixed in v2.28.8. | 2023-03-16 | not yet calculated | CVE-2023-28110 MISC MISC |
| discourse -- discourse | Discourse is an open-source discussion platform. Prior to version 3.1.0.beta3 of the beta and tests-passed branches, attackers are able to bypass Discourse's server-side request forgery (SSRF) protection for private IPv4 addresses by using a IPv4-mapped IPv6 address. The issue is patched in the latest beta and tests-passed version of Discourse. version 3.1.0.beta3 of the beta and tests-passed branches. There are no known workarounds. |
2023-03-17 | not yet calculated | CVE-2023-28111 MISC MISC MISC |
| discourse -- discourse | Discourse is an open-source discussion platform. Prior to version 3.1.0.beta3 of the beta and tests-passed branches, some user provided URLs were being passed to FastImage without SSRF protection. Insufficient protections could enable attackers to trigger outbound network connections from the Discourse server to private IP addresses. This affects any site running the tests-passed or beta branches versions 3.1.0.beta2 and prior. This issue is patched in version 3.1.0.beta3 of the beta and tests-passed branches. There are no known workarounds. |
2023-03-17 | not yet calculated | CVE-2023-28112 MISC MISC MISC |
| warp-tech -- russh | russh is a Rust SSH client and server library. Starting in version 0.34.0 and prior to versions 0.36.2 and 0.37.1, Diffie-Hellman key validation is insufficient, which can lead to insecure shared secrets and therefore breaks confidentiality. Connections between a russh client and server or those of a russh peer with some other misbehaving peer are most likely to be problematic. These may vulnerable to eavesdropping. Most other implementations reject such keys, so this is mainly an interoperability issue in such a case. This issue is fixed in versions 0.36.2 and 0.37.1 | 2023-03-16 | not yet calculated | CVE-2023-28113 MISC MISC MISC CONFIRM MISC MISC |
| knp_labs -- snappy | Snappy is a PHP library allowing thumbnail, snapshot or PDF generation from a url or a html page. Prior to version 1.4.2, Snappy is vulnerable to PHAR deserialization due to a lack of checking on the protocol before passing it into the file_exists() function. If an attacker can upload files of any type to the server he can pass in the phar:// protocol to unserialize the uploaded file and instantiate arbitrary PHP objects. This can lead to remote code execution especially when snappy is used with frameworks with documented POP chains like Laravel/Symfony vulnerable developer code. If a user can control the output file from the generateFromHtml() function, it will invoke deserialization. This vulnerability is capable of remote code execution if Snappy is used with frameworks or developer code with vulnerable POP chains. It has been fixed in version 1.4.2. |
2023-03-17 | not yet calculated | CVE-2023-28115 MISC MISC MISC MISC MISC MISC |
| contiki-ng -- contiki-ng | Contiki-NG is an open-source, cross-platform operating system for internet of things (IoT) devices. In versions 4.8 and prior, an out-of-bounds write can occur in the BLE L2CAP module of the Contiki-NG operating system. The network stack of Contiki-NG uses a global buffer (packetbuf) for processing of packets, with the size of PACKETBUF_SIZE. In particular, when using the BLE L2CAP module with the default configuration, the PACKETBUF_SIZE value becomes larger then the actual size of the packetbuf. When large packets are processed by the L2CAP module, a buffer overflow can therefore occur when copying the packet data to the packetbuf. The vulnerability has been patched in the "develop" branch of Contiki-NG, and will be included in release 4.9. The problem can be worked around by applying the patch manually. | 2023-03-17 | not yet calculated | CVE-2023-28116 MISC MISC |
| kdab -- hotspot | KDAB Hotspot 1.3.x and 1.4.x through 1.4.1, in a non-default configuration, allows privilege escalation because of race conditions involving symlinks and elevate_perf_privileges.sh chown calls. | 2023-03-14 | not yet calculated | CVE-2023-28144 MISC MISC |
| netgear -- nighthawk_wifi6_(rax30) | When uploading a firmware image to a Netgear Nighthawk Wifi6 Router (RAX30), a hidden “forceFWUpdate” parameter may be provided to force the upgrade to complete and bypass certain validation checks. End users can use this to upload modified, unofficial, and potentially malicious firmware to the device. | 2023-03-15 | not yet calculated | CVE-2023-28337 MISC |
| netgear -- nighthawk_wifi6_(rax30) | Any request send to a Netgear Nighthawk Wifi6 Router (RAX30)'s web service containing a “Content-Type” of “multipartboundary=” will result in the request body being written to “/tmp/mulipartFile” on the device itself. A sufficiently large file will cause device resources to be exhausted, resulting in the device becoming unusable until it is rebooted. | 2023-03-15 | not yet calculated | CVE-2023-28338 MISC |
| openbsd -- opendoas | OpenDoas through 6.8.2, when TIOCSTI is available, allows privilege escalation because of sharing a terminal with the original session. NOTE: TIOCSTI is unavailable in OpenBSD 6.0 and later, and can be made unavailable in the Linux kernel 6.2 and later. | 2023-03-14 | not yet calculated | CVE-2023-28339 MISC |
| altenergy_power_systems -- control_software_c1.2.5 | OS command injection affects Altenergy Power Control Software C1.2.5 via shell metacharacters in the index.php/management/set_timezone timezone parameter, because of set_timezone in models/management_model.php. | 2023-03-14 | not yet calculated | CVE-2023-28343 MISC MISC |
| stellarium -- stellarium | In Stellarium through 1.2, attackers can write to files that are typically unintended, such as ones with absolute pathnames or .. directory traversal. | 2023-03-15 | not yet calculated | CVE-2023-28371 MISC MISC MISC |
| dnsmasq_by_simon_kelley -- dnsmasq | An issue was discovered in Dnsmasq before 2.90. The default maximum EDNS.0 UDP packet size was set to 4096 but should be 1232 because of DNS Flag Day 2020. | 2023-03-15 | not yet calculated | CVE-2023-28450 MISC MISC MISC MISC |
| array_networks -- apv_products | A command injection vulnerability was discovered in Array Networks APV products. A remote attacker can send a crafted packet after logging into the affected appliance as an administrator, resulting in arbitrary shell code execution. This is fixed in 8.6.1.262 or newer and 10.4.2.93 or newer. | 2023-03-15 | not yet calculated | CVE-2023-28460 MISC |
| array_networks -- ag_series_and_vxag | Array Networks Array AG Series and vxAG (9.4.0.481 and earlier) allow remote code execution. An attacker can browse the filesystem on the SSL VPN gateway using a flags attribute in an HTTP header without authentication. The product could then be exploited through a vulnerable URL. The 2023-03-09 vendor advisory stated "a new Array AG release with the fix will be available soon." | 2023-03-15 | not yet calculated | CVE-2023-28461 MISC |
| linux -- kernel | do_tls_getsockopt in net/tls/tls_main.c in the Linux kernel through 6.2.6 lacks a lock_sock call, leading to a race condition (with a resultant use-after-free or NULL pointer dereference). | 2023-03-16 | not yet calculated | CVE-2023-28466 MISC |
| sudo -- sudo | Sudo before 1.9.13 does not escape control characters in log messages. | 2023-03-16 | not yet calculated | CVE-2023-28486 MISC MISC |
| sudo -- sudo | Sudo before 1.9.13 does not escape control characters in sudoreplay output. | 2023-03-16 | not yet calculated | CVE-2023-28487 MISC MISC |
| openssh -- openssh | ssh-add in OpenSSH before 9.3 adds smartcard keys to ssh-agent without the intended per-hop destination constraints. | 2023-03-17 | not yet calculated | CVE-2023-28531 MISC |
| misp -- misp | js/event-graph.js in MISP before 2.4.169 allows XSS via event-graph node tooltips. | 2023-03-18 | not yet calculated | CVE-2023-28606 MISC MISC |
| misp -- misp | js/event-graph.js in MISP before 2.4.169 allows XSS via the event-graph relationship tooltip. | 2023-03-18 | not yet calculated | CVE-2023-28607 MISC MISC |
| ansible_semaphore -- ansible_semaphore | api/auth.go in Ansible Semaphore before 2.8.89 mishandles authentication. | 2023-03-18 | not yet calculated | CVE-2023-28609 MISC MISC |
Continue reading...[/code]